


WebSocket tests verify that a real-time connection behaves correctly across connection, message exchange, error handling, and closure. Effective WebSocket testing combines functional validation, load and latency measurement, and protocol compliance checks using tools like k6 and the Autobahn Test Suite. If you ship real-time features without this coverage, you find out about broken handshakes and dropped frames from your users instead of your pipeline.
Real-time features are the parts of your application users notice immediately when they break. A chat message that never arrives, a live dashboard that freezes, a collaborative editor that silently loses edits: every one of these traces back to a WebSocket layer that was never systematically tested. Most teams test their REST APIs thoroughly and then treat the WebSocket connection as an afterthought, assuming that if the handshake succeeds, everything else will follow.
That assumption fails in production. WebSockets carry stateful, long-lived connections that behave very differently from request-response APIs under load, network instability, and adversarial input. This guide walks through the full discipline of websocket tests: what the protocol actually guarantees, the categories of tests you need, how to build a test environment, which tools to use, and how to wire everything into CI/CD so reliability is verified continuously rather than assumed.
Understanding the WebSocket Protocol
The WebSocket protocol, standardized in RFC 6455 by the IETF, upgrades an ordinary HTTP request into a persistent, bidirectional connection. A client sends an HTTP upgrade request, the server responds with a successful switching-protocols status, and from that point both sides exchange framed messages over the same TCP connection. Frames can carry text or binary payloads, and each frame includes an opcode, a payload length, and a masking key when sent from the client.
The protocol also defines a close handshake, where either side signals intent to shut down and the other acknowledges, plus a set of standard close codes that describe why the connection ended. Ping and pong control frames act as keep-alives and liveness probes. Understanding these mechanics matters for testing because every one of them, the upgrade, the framing, the close codes, and the keep-alives, is a distinct surface where implementations can and do fail.
Why WebSocket Tests Matter
Untested WebSocket code fails in ways that unit tests on your business logic never catch. A server that drops connections after exactly 60 seconds because an intermediary proxy times out idle sockets will pass every functional test on localhost and fall over in production. Latency spikes that appear only at high concurrency, memory leaks that accumulate across thousands of long-lived connections, and malformed frames that crash a poorly validated parser are all failure modes invisible without dedicated websocket tests.
Security adds another dimension. Because WebSocket connections persist and often carry authenticated sessions, a mishandled close code or an unvalidated frame can leak state between users or expose the server to denial-of-service attacks. Real-world postmortems from real-time platforms consistently show that the root cause was an untested edge in the connection lifecycle, not the application logic riding on top of it.
Types of WebSocket Tests
A mature WebSocket test strategy covers four distinct categories, each answering a different question about your implementation.
Functional WebSocket Tests
Functional tests verify the basics: a connection can be established, text and binary messages round-trip correctly, the negotiated sub-protocol matches expectations, and both clean and abnormal closures are handled. These tests are the foundation, and they should run on every commit.
Performance and Load WebSocket Tests
Load tests answer how the system behaves at scale. They measure how many concurrent connections the server sustains, message throughput under pressure, and how round-trip latency degrades as connection counts climb. Performance testing reveals bottlenecks like per-connection memory overhead and event-loop saturation.
Security and Compliance WebSocket Tests
Security tests validate that the connection is encrypted, that authentication is enforced at handshake time, and that the server rejects malformed or oversized frames instead of crashing or misinterpreting them. Compliance testing, most notably with the Autobahn Test Suite, checks the implementation against the full RFC 6455 specification.
Interoperability WebSocket Tests
Interoperability tests confirm that different client libraries and server implementations talk to each other correctly. A browser client, a Node.js client, and a mobile client should all negotiate the same handshake and interpret the same frames identically. Cross-library testing catches subtle divergences in how masking, fragmentation, and close semantics are implemented.
Setting Up a Test Environment
Your test environment determines what your tests can actually tell you, so set it up deliberately rather than defaulting to whatever is running locally.
Local Development Server
Start with a minimal echo server, a server that accepts a connection and returns every message it receives. An echo server removes application logic from the picture, letting you validate connection behavior, framing, and closure in isolation. Once the transport layer is proven, point the same tests at your real server. This two-stage approach separates transport bugs from application bugs, which saves hours of debugging.
Test Client Frameworks
Choose a test client that matches your application's language and ecosystem. Node.js projects can use the language's native WebSocket support within its standard test runners, Python projects can use popular async WebSocket client libraries alongside pytest, and mobile teams should test with the same client library the app actually ships. Testing with the production client library, rather than a generic one, is what makes interoperability results meaningful.
Network Considerations
Localhost testing is fast and deterministic, but it hides real network behavior. Intermediate proxies, load balancers, and NAT devices all interact with long-lived connections in ways a loopback connection never exercises. For production realism, run tests against a staged environment behind the same proxy chain as production. If your real-time layer involves peer media or NAT traversal, remember that STUN and TURN infrastructure, the same relay mechanisms used in WebRTC deployments, becomes part of the environment you must test. VideoSDK's real-time communication platform, for example, handles this infrastructure layer for teams building video and audio calling, but if you operate raw WebSocket infrastructure yourself, the traversal path is yours to verify.
Popular WebSocket Testing Tools
The tooling landscape is mature, and each tool occupies a distinct niche. Picking the right one for each test category matters more than trying to force a single tool to do everything.
k6 WebSocket Load Testing
k6, the open-source load testing tool from Grafana Labs, treats WebSocket testing as a first-class citizen. Its virtual user model lets you describe realistic connection lifecycles: a simulated user connects, exchanges messages over time, occasionally disconnects and reconnects, and eventually closes cleanly. k6 records built-in metrics for connection duration, message round-trip times, and sent and received message counts, and it supports thresholds so a pipeline can fail automatically when latency percentiles regress. For teams already using k6 for HTTP load testing, extending coverage to WebSocket endpoints is a natural step.
Autobahn Test Suite
The Autobahn Test Suite is the reference standard for WebSocket protocol compliance. It runs hundreds of individual cases against your server, probing edge cases in framing, fragmentation, UTF-8 validation, close handling, and reserved bit behavior. It then produces a detailed report showing exactly which specification requirements your implementation violates. If you are building your own WebSocket server or library rather than using a battle-tested one, running Autobahn is non-negotiable. Even teams using established libraries benefit from an occasional compliance run to catch regressions after upgrades.
wsperf and Custom Scripts
For lightweight, targeted load generation, wsperf and similar minimal tools generate connection and message pressure without the overhead of a full load-testing platform. Language-native libraries also work well for custom scenarios: a Python or Node script can simulate your exact application's message patterns, including realistic JSON payloads and binary frames, which generic tools often approximate poorly. Custom scripts trade convenience for fidelity, and for application-specific performance questions, that fidelity is worth it.
Choosing the Right Tool
Match the tool to the question you are asking. Use Autobahn when the question is whether your implementation conforms to RFC 6455. Use k6 when the question is how many concurrent connections you sustain and what latency looks like under load. Use custom language-native scripts when the question is how your specific message patterns perform. A complete strategy typically layers all three: compliance verified once and after upgrades, load tested continuously in CI, and custom scenarios added as the application evolves.
Designing Effective Functional Tests
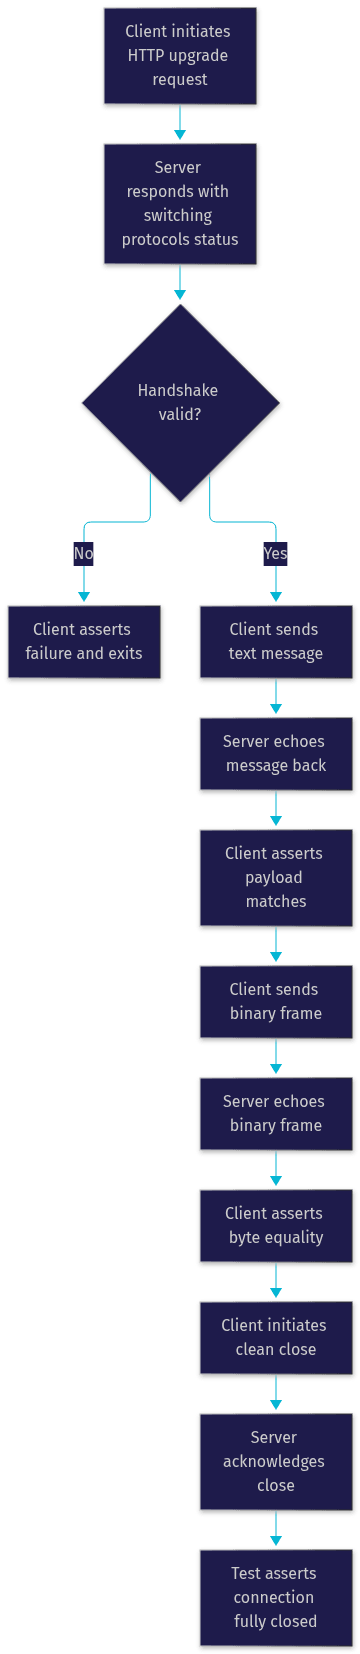
Functional websocket tests should mirror the full connection lifecycle, from handshake through closure, with explicit assertions at every stage.
Handshake Validation
Every functional test begins by asserting the handshake succeeded. The client should confirm the upgrade response carries the switching-protocols status, that the negotiated sub-protocol matches what the application expects, and that any authentication token sent during the upgrade was accepted. A handshake that succeeds but negotiates the wrong sub-protocol will produce confusing downstream failures, so catch it at the source.
Message Exchange Scenarios
Cover all three payload types your application uses: plain text, structured JSON, and binary data. For text messages, assert the round-tripped content matches exactly, including edge cases like empty strings and multi-byte characters. For JSON, assert semantic equality rather than string equality, since key ordering is not guaranteed. For binary payloads, include tests with empty frames, single-byte frames, and large multi-frame messages that exercise fragmentation and reassembly.
Error-Handling Paths
Error handling is where most implementations hide their bugs. Test that an unexpected close code from the server triggers your reconnection logic, that a protocol violation results in a clean rejection rather than a crash, and that a client that stops responding eventually times out according to your keep-alive policy. Every close code your application can emit should have a corresponding test asserting the client responds appropriately.
Using Mermaid for Test Flow Diagrams
Documenting the expected connection lifecycle as a diagram keeps the whole team aligned on what a correct interaction looks like, and it doubles as a review artifact when tests fail.
Performance and Load Testing Strategies
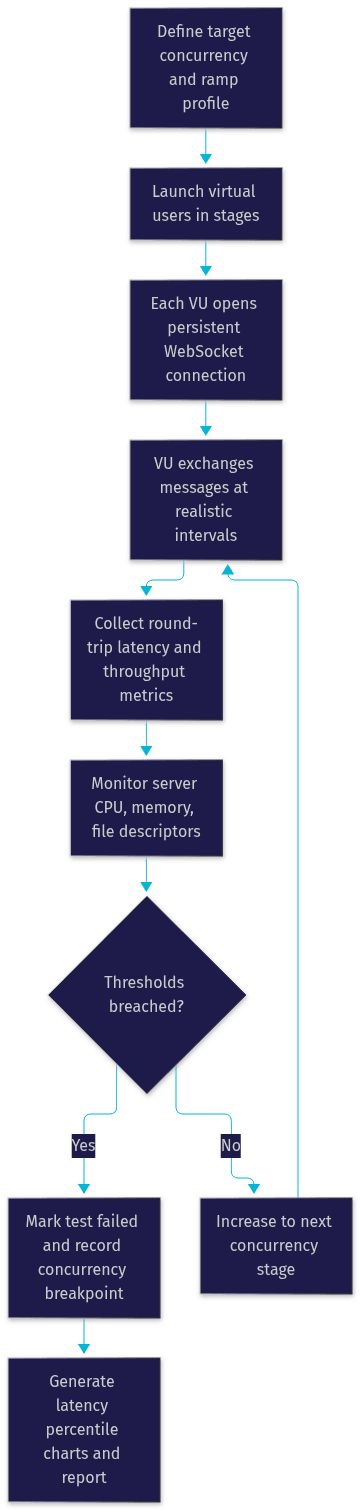
Load testing WebSockets differs from load testing HTTP because connections are long-lived and stateful, so the strategy must account for connection lifetime, not just request volume.
Simulating Concurrent Connections
Scale virtual users gradually rather than all at once. A ramp-up pattern, where connections join steadily over a defined window, reveals the exact concurrency level where latency degrades or connections start failing. A step pattern, which holds at each concurrency level before increasing, gives you stable measurements at each tier. Both patterns tell you more than a single massive spike, which usually just tells you the server falls over without telling you where the cliff is.
Measuring Latency and Throughput
Capture round-trip time for individual messages, not just aggregate response rates, because WebSocket users feel per-message latency directly. Track messages per second in both directions, and record latency percentiles rather than averages: a 95th or 99th percentile that climbs sharply while the average stays flat is the classic signature of a server struggling with a subset of connections. k6 records these metrics natively, which is one reason it dominates this niche.
Resource Monitoring
Pair client-side metrics with server-side resource monitoring. Watch CPU, memory, and file descriptor counts as connections scale, because WebSocket servers are frequently bound by per-connection memory or operating system connection limits long before they are bound by CPU. A memory curve that climbs linearly with connection count and never plateaus points to a per-connection leak.
Visualising Results
Chart latency percentiles over time alongside the concurrency ramp so you can see exactly when performance degrades. A graph showing the 99th percentile latency jumping at four thousand concurrent connections is a finding a table of averages will never surface. Grafana dashboards pair naturally with k6 for this, and the visual history becomes your performance baseline for detecting regressions.
Security and Compliance Testing
WebSocket security testing verifies that the connection itself is trustworthy, not just that the application logic on top of it is correct.
TLS and Certificate Validation
Test that production endpoints accept only encrypted connections over the secure WebSocket scheme, that plain unencrypted upgrade requests are refused, and that certificate validation behaves correctly on the client side. If your clients pin certificates, test what happens when a pinned certificate rotates, because a rotation that skips testing becomes an outage. Verify handshake failure handling for expired and self-signed certificates as well.
Authentication Flows
Validate that unauthenticated upgrade requests are rejected before any message exchange occurs, that tokens passed during the handshake are validated server-side, and that expired or revoked tokens result in connection termination with the appropriate close code. Test session expiry mid-connection: a long-lived connection established with a token that expires an hour later should be handled according to your policy, whether that is revalidation or graceful closure, not left dangling with stale credentials.
Fuzzing Malformed Frames
The Autobahn Test Suite doubles as a fuzzer for protocol-level robustness. It sends oversized payloads, frames with invalid opcodes, fragmented messages assembled incorrectly, and payloads with invalid UTF-8 sequences, then verifies the server responds with the protocol-mandated failure rather than crashing or misbehaving. Any server that accepts malformed input silently is a server an attacker can eventually desynchronize.
Rate-Limiting and DoS Checks
Simulate burst traffic to verify your rate limiting actually engages. Open hundreds of connections in rapid succession, send messages at rates far beyond legitimate use, and confirm the server sheds load gracefully rather than degrading for everyone. Also test slow-loris style behavior, connections that open but send data at a trickle, since these consume resources without tripping naive rate limiters.
Automating WebSocket Tests in CI/CD
Manual testing catches problems after they exist; automation catches them before they merge.
Pipeline Integration
Run functional WebSocket tests on every pull request alongside your existing unit and integration suites. Add a k6 load test with conservative thresholds as a required check for changes touching the real-time layer, and run the full Autobahn compliance suite on a schedule, such as nightly or whenever a dependency version changes. GitHub Actions and GitLab CI both handle this well: the functional suite needs only a running server and a test runner, and k6 publishes machine-readable results the pipeline can evaluate against thresholds.
Reporting and Flake Mitigation
Network-dependent tests are inherently flaky, so engineer against it. Capture full connection logs on failure so a flaky test is diagnosable rather than just retried blindly. Generate JUnit-format reports so results integrate with your pipeline's existing test visualization. Apply bounded retry strategies for genuinely transient network failures, but treat repeated flakes as a signal worth investigating, because intermittent connection failures in CI often preview intermittent failures in production.
Continuous Monitoring
Beyond pass/fail gates, run a nightly performance baseline against a staged environment. Comparing each night's latency percentiles and throughput against the historical baseline turns performance regression detection from a quarterly firefight into a daily diff. When a dependency upgrade quietly doubles round-trip latency, you want to know the next morning, not at your next load test.
Best Practices and Common Pitfalls
Keep tests deterministic by controlling timing explicitly: inject clocks and delays rather than relying on real network timing, which varies between runs. Avoid hard-coded ports, since parallel test runs in CI will collide; let the test environment assign ports dynamically. Always clean up connections in test teardown, because leaked connections accumulate across a suite and produce baffling failures in later tests. Isolate tests from each other so one test's abandoned connection does not become another test's unexpected message.
The most common pitfall is testing only the happy path. A suite that verifies messages round-trip but never tests abnormal closures, expired tokens, or malformed frames provides false confidence. The second most common is ignoring the proxy layer: always run at least a subset of tests through the same load balancer and proxy chain production uses, because intermediaries rewrite, buffer, and time out WebSocket connections in ways your server cannot control.
Definitions Glossary
WebSocket handshake: The HTTP upgrade exchange defined in RFC 6455 that converts a standard HTTP connection into a persistent bidirectional WebSocket connection, confirmed by a switching-protocols response from the server.
Close code: A numeric status code sent during the WebSocket close handshake that describes why the connection ended, such as normal closure, protocol error, or authentication failure, and which client logic should handle distinctly.
Frame masking: A protocol requirement that all client-to-server frames apply an XOR mask to their payload, which compliant servers must validate and unmask correctly.
Virtual user (VU): A simulated participant in load testing tools like k6 that opens connections and exchanges messages according to a scripted lifecycle, used to model realistic concurrency.
Latency percentile: A distribution statistic, such as the 99th percentile, describing the latency experienced by the slowest portion of messages, which surfaces tail degradation that averages hide.
Protocol compliance testing: Verification that a WebSocket implementation conforms to the full RFC 6455 specification, typically performed with the Autobahn Test Suite's matrix of framing, fragmentation, and close-handling cases.
Key Takeaways
- WebSocket tests must cover four categories: functional message exchange, performance under concurrent load, security and compliance, and cross-library interoperability.
- The Autobahn Test Suite is the reference standard for RFC 6455 compliance and doubles as a fuzzer for malformed frame handling.
- k6 provides scriptable virtual users with native WebSocket metrics and threshold-based pass/fail gates, making it the strongest choice for CI-integrated load testing.
- Functional tests should assert the full lifecycle: handshake status, sub-protocol negotiation, text and binary payload integrity, and every close code the application can emit.
- Always test through the same proxy and load balancer chain as production, because intermediaries time out and buffer long-lived connections in ways localhost testing never reveals.
Conclusion
A disciplined approach to websocket tests turns your real-time layer from an assumed-reliable component into a verified one. Start with functional lifecycle coverage on every commit, add k6 load testing with latency thresholds in CI, run Autobahn compliance checks on a schedule, and maintain a nightly performance baseline so regressions surface as diffs rather than incidents. The tools are mature and the patterns are proven, so the only real risk is skipping the coverage. If you are building real-time features beyond raw sockets, including embedded video and audio calling, explore how VideoSDK's real-time communication platform handles the transport, scaling, and traversal complexity for you. What are you building with WebSockets? Drop a comment, I'd love to hear what kind of real-time use case you're testing for.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ