


A WebSocket is a persistent, full-duplex communication channel that starts as an HTTP upgrade and then stays open so client and server can push messages to each other at any time. Unlike request-response HTTP, it removes per-message overhead, which is why real-time apps like chat, live dashboards, and multiplayer games rely on it. If you are building real-time features, this WebSocket guide walks you from the handshake through production scaling, and shows where a managed real-time platform like VideoSDK can save you the infrastructure work entirely.
Modern users expect apps to update the instant something happens. A chat message should appear without a refresh, a live auction bid should land in milliseconds, and a collaborative whiteboard should reflect every stroke as it is drawn. Classic HTTP was never designed for that rhythm, because every piece of new information traditionally required the client to ask for it.
That expectation gap is exactly why the WebSocket protocol exists. It gives browsers and servers a way to hold one open connection and exchange messages in both directions whenever either side has something to say. By the end of this WebSocket guide, you will understand how the protocol works under the hood, how the browser and server sides fit together, and what it takes to run WebSockets reliably in production.
What is a WebSocket?
A WebSocket is defined as a communication protocol, standardized by the IETF in RFC 6455, that provides a single, long-lived TCP connection over which both client and server can send messages at any time. It is full-duplex, meaning data flows in both directions simultaneously, and it is persistent, meaning the connection stays open rather than being re-established for every exchange.
Compare that to classic HTTP. In a traditional request-response cycle, the client opens a connection, sends a request, waits for the server to respond, and the connection is then closed or reused for a completely separate exchange. If the server has new information, it has no way to push it. The client must poll, which wastes requests, or the app must fake real-time behavior with tricks like long polling.
WebSockets work by reusing the initial HTTP connection for something better. After a brief negotiation, the same TCP connection switches from HTTP semantics to a lightweight frame-based protocol. Each message is wrapped in a small frame header, typically just a few bytes, instead of the hundreds of bytes of headers an HTTP request carries. That low overhead is what makes WebSockets suitable for high-frequency messaging like live trading feeds or game state updates.
One detail worth locking in early: WebSocket URLs use the ws scheme for plain connections and the wss scheme for connections encrypted with TLS, in the same way plain HTTP relates to HTTPS. In production, always use the encrypted wss scheme, which we cover in the security section.
The WebSocket Handshake Explained
Every WebSocket connection begins its life as an ordinary HTTP request. The handshake is the mechanism that turns that HTTP request into a persistent WebSocket connection, and understanding it explains most of the odd errors you will hit later.
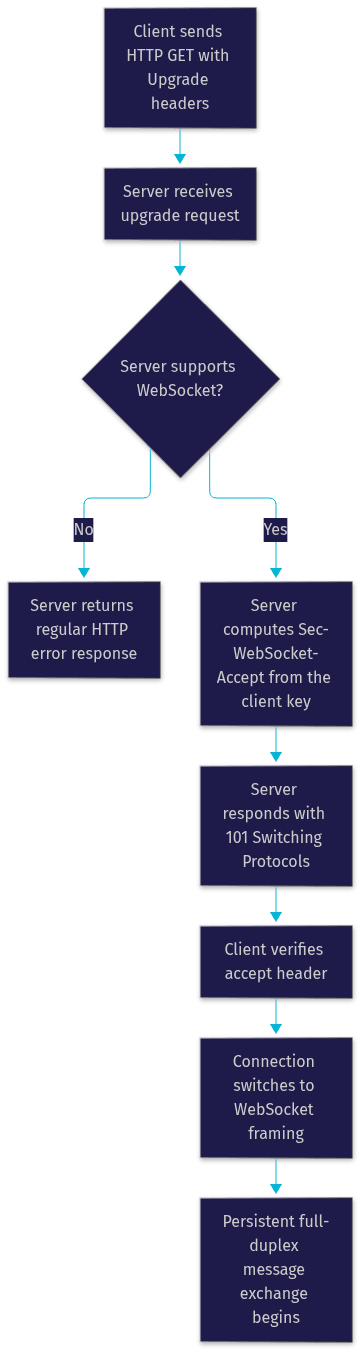
The process works like this. The client sends an HTTP GET request containing special headers that declare its intent to upgrade the protocol. The most important is the Upgrade header, which names WebSocket as the target protocol, paired with a Connection header that signals the upgrade is intended for this specific exchange rather than being a generic hop-by-hop instruction.
If the server supports WebSockets and agrees to the upgrade, it responds with the HTTP status code 101, Switching Protocols. From that moment forward, the connection is no longer speaking HTTP. Both sides switch to the WebSocket framing protocol, and the TCP connection remains open until either side closes it or the network drops it.
The handshake also includes a safety mechanism. The client sends a random value in the Sec-WebSocket-Key header, and the server proves it genuinely understands the protocol by combining that key with a fixed GUID defined in RFC 6455, hashing the result, and returning it in the Sec-WebSocket-Accept header. The client verifies the response before committing to the connection. This prevents a plain HTTP server from accidentally accepting an upgrade request, and it also stops misbehaving intermediaries like caching proxies from pretending to complete a handshake.
Handshake Headers Deep Dive
A handful of headers carry the entire negotiation. The Upgrade header tells the server the client wants the WebSocket protocol specifically. The Connection header, set to the upgrade value, marks the upgrade request as end-to-end rather than hop-by-hop, which matters when proxies sit in the path. Sec-WebSocket-Key carries the random challenge value, and Sec-WebSocket-Version declares which protocol revision the client speaks, currently version 13. Finally, the Origin header tells the server which website initiated the connection, which is your primary defense against cross-site hijacking attempts, since servers should reject upgrades from origins they do not trust.
Browser WebSocket API Overview
Browsers expose WebSockets through a small, event-driven API centered on the WebSocket constructor. You create a connection by instantiating it with a WebSocket URL using either the plain ws scheme or the encrypted wss scheme, optionally declaring sub-protocols the app speaks, and the browser handles the entire handshake on your behalf.
Once created, the connection object moves through a defined lifecycle, and each stage fires an event your code can react to. The open event fires when the handshake completes and the connection is ready for messages. The message event fires every time a frame arrives, delivering the payload as text or binary data depending on how it was sent. The error event signals something went wrong, such as a failed handshake or a dropped connection. The close event fires when the connection ends, whether you closed it deliberately or the network did, and it includes a code and reason you can inspect.
The typical usage pattern in prose looks like this: create the connection, wait for it to open, send messages whenever the app has something to share, react to incoming messages as they arrive, and when the connection closes, decide whether to reconnect. That last decision, reconnection, is entirely your responsibility, because the browser API deliberately does not reconnect for you.
Server-Side WebSocket Foundations
On the server side, a WebSocket implementation has three core responsibilities: accept upgrade requests, manage the resulting connections, and route messages between them. Every runtime, from Node.js to Python to Go, wraps those same responsibilities in different syntax.
Accepting upgrades means intercepting the HTTP request before it completes normally, validating the handshake headers, and responding with the 101 status. Most developers never write this by hand. Popular libraries in Node.js and Python handle the handshake, frame parsing, and masking, letting you register callbacks for connection, message, and disconnection events.
Managing connections is where real architecture begins. A server needs a connection manager, a structure that tracks every live socket, associates each with identity and metadata such as which room or channel it belongs to, and removes entries cleanly when sockets disconnect. Without deliberate cleanup, dead connections accumulate and leak memory, a classic production failure.
Broadcasting is the third responsibility. In a chat app, when one client sends a message, the server decides which other connected sockets should receive it and writes the same frame to each. That fan-out pattern, combined with room-based grouping, is the backbone of nearly every real-time application.
One concept that surprises developers moving from scripting to servers is the event loop. Both Node.js and Python's asyncio runtimes handle thousands of concurrent WebSocket connections on a single process by interleaving work rather than spawning a thread per connection. That works beautifully for I/O-bound messaging, but any long-running computation inside a message handler stalls every connected client, so heavy work should be handed off to background workers.
Scaling WebSocket Servers
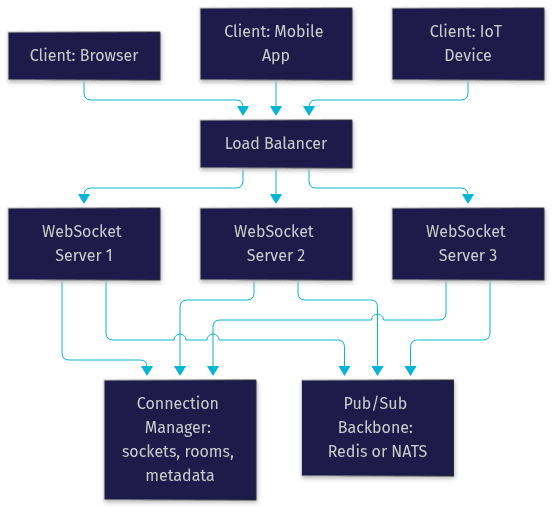
A single server process eventually saturates, and scaling WebSockets horizontally introduces a problem HTTP does not have: statefulness. Each server holds live connections, so a message arriving at server one cannot reach a client connected to server two unless the servers share information.
The standard solution is a shared pub/sub backbone such as Redis or NATS. When a client sends a message, the receiving server publishes it to a channel, and every server subscribed to that channel delivers it to its own connected clients. This turns your fleet into one logical broadcast domain.
The second concern is routing. Load balancers must use sticky sessions, directing all traffic from one client to one server, because a WebSocket handshake cannot be re-balanced mid-connection. Alternatively, some teams route by room or channel identifier so all participants of one conversation land on the same server.
Finally, cloud-native options exist. Managed real-time platforms handle connection distribution, presence, and failover for you, which is exactly the problem space VideoSDK's real-time communication SDKs are built for, letting you focus on product features instead of pub/sub plumbing.
WebSocket Security Best Practices
WebSocket security starts with transport encryption. Every production connection should use the encrypted wss scheme, which wraps the WebSocket in TLS so payloads and credentials cannot be read or modified in transit. Plain, unencrypted WebSocket connections should never leave localhost.
Authentication deserves special attention because browsers cannot set custom headers on WebSocket connections the way they can on HTTP requests. The common patterns are passing a signed token as a query parameter or a sub-protocol during the handshake, or sending an authentication message as the first frame after the connection opens. Whatever you choose, validate it server-side before accepting any further messages, and use short-lived tokens that can be refreshed.
Origin checking is your defense against cross-site WebSocket hijacking. Because browsers send the Origin header during the handshake, your server should reject any upgrade request from a domain it does not expect. Without this check, a malicious page can open a WebSocket to your server using the victim's browser context.
Rate limiting matters more than most teams realize. A WebSocket connection is a cheap way for an attacker to hold server resources open, so limit connections per IP and per user, cap message frequency, and enforce maximum payload sizes. Pair that with infrastructure-level protections such as connection timeouts and DDoS mitigation at your edge.
Certificate management follows standard TLS practice: obtain certificates from a trusted authority, automate renewal, and terminate TLS either at your WebSocket server or at a reverse proxy like Nginx, which can also handle origin validation and rate limits before traffic reaches your app.
Keeping WebSocket Connections Healthy
Long-lived connections die quietly. Proxies, load balancers, and firewalls often terminate connections that appear idle, and half-open connections, where one side has vanished without sending a close frame, leave servers holding ghost sockets.
The fix is a heartbeat mechanism built on the protocol's native ping and pong control frames. The server periodically sends a ping, and any healthy client responds with a pong. If no pong arrives within a timeout window, the server closes the connection and frees its resources. Many client libraries implement the same logic in reverse.
Reconnection logic is equally essential, because the browser API will not reconnect for you. A robust client detects the close event, waits using exponential backoff so a server outage is not hammered by thousands of simultaneous retries, and re-authenticates on the new connection. Well-designed apps also resubscribe to channels and fetch any state missed while offline, since messages sent during the gap are otherwise lost forever.
Idle timeout handling rounds out the picture. Decide deliberately how long an authenticated but silent connection may remain open, and close it gracefully with an appropriate close code so the client knows whether reconnecting immediately makes sense.
When to Choose WebSocket vs. Alternatives
WebSockets are powerful, but they are not always the right tool. The honest decision depends on whether you need bidirectional flow, how many connections you can afford to hold open, and how much server complexity you can operate.
Server-Sent Events, or SSE, deliver a simpler model when the flow is one-directional from server to client. SSE rides on plain HTTP, reconnects automatically in the browser, and is dramatically easier to scale behind ordinary HTTP infrastructure. Long polling remains a fallback for environments where even SSE is blocked, at the cost of latency and wasted requests. WebTransport, built on HTTP/3 and QUIC, is the emerging option, promising WebSocket-like bidirectionality with better congestion control and connection migration, though browser support is still maturing as of 2026.
| Criterion | WebSocket | Server-Sent Events | Long Polling | WebTransport |
|---|---|---|---|---|
| Direction | Full-duplex, both ways | Server to client only | Client asks, server holds | Full-duplex, both ways |
| Latency | Very low, push-based | Low for server pushes | Moderate, request per update | Very low, QUIC-based |
| Browser support | Universal | Universal | Universal | Partial, growing in 2026 |
| Server complexity | High: stateful connections, pub/sub | Low: plain HTTP | Low to medium | High, newer ecosystem |
| Best for | Chat, games, collaborative apps | Live feeds, notifications, dashboards | Legacy environments, constrained networks | High-performance, loss-tolerant streaming |
The practical rule: if the client only listens, choose SSE and save yourself the stateful infrastructure. If the client talks back frequently, WebSockets win. If you are already operating real-time video, voice, or interactive streaming, a managed SDK removes the comparison entirely, since VideoSDK's interactive live streaming handles the transport layer for you.
Debugging and Performance Tips
Debugging WebSockets starts in the browser's developer tools. The Network tab lists WebSocket connections, and selecting one opens a frames view showing every message sent and received with timestamps and payload sizes. This is the fastest way to confirm whether a problem is transport-level, such as a handshake failing, or application-level, such as messages being sent but ignored.
For handshake failures, check three usual suspects. A missing or malformed Sec-WebSocket-Key means a client library is broken or something rewrote the request. Proxy interference appears when corporate proxies or misconfigured reverse proxies strip Upgrade headers, so the server never sees a valid upgrade request. Firewall blocks often manifest as connections that open and immediately close, since some networks only permit plain HTTP patterns.
On performance, measure round-trip latency by timestamping messages on both sides, and watch payload size. Large messages fragment across frames and add buffering delay, so prefer many small messages over few large ones, and compress large payloads at the application layer if bandwidth matters. Also monitor connection counts and memory per process, since leaked ghost sockets are the most common slow degradation in WebSocket servers.
Production Checklist for WebSocket Deployments
Before shipping, run through this checklist:
- Security: enforce encrypted wss transport everywhere, validate Origin on every handshake, authenticate before accepting messages, and use short-lived tokens.
- Limits: cap message size, rate-limit per connection and per IP, and set idle timeouts.
- Scaling: use sticky sessions at the load balancer and a shared pub/sub backbone across server instances.
- Health: implement ping/pong heartbeats with server-side timeout enforcement.
- Resilience: build client reconnection with exponential backoff and state resynchronization. | Observability: log connect, disconnect, and error events with correlation IDs, and alert on abnormal close rates.
- Operations: support graceful shutdown so deploys drain connections instead of dropping them, and version your message schemas.
Definitions Glossary
WebSocket: A persistent, full-duplex communication protocol standardized in RFC 6455 that begins as an HTTP upgrade and then carries lightweight framed messages in both directions over a single TCP connection.
Handshake: The HTTP exchange in which a client requests a protocol upgrade and the server responds with status 101, switching the connection from HTTP to WebSocket framing.
Sec-WebSocket-Accept: A header the server returns during the handshake, computed by hashing the client's random key with a fixed GUID, proving the server genuinely implements the WebSocket protocol.
Heartbeat (ping/pong): A keep-alive mechanism where one side sends periodic ping control frames and expects pong replies, used to detect dead or half-open connections.
Sticky sessions: A load-balancing strategy that routes all traffic from one client to the same server, required because a WebSocket connection cannot be re-balanced after the handshake.
Pub/sub backbone: A shared message broker such as Redis or NATS that lets multiple WebSocket servers exchange messages so any client can be reached regardless of which server holds its connection.
Key Takeaways
- WebSockets provide a single persistent, full-duplex connection that begins with an HTTP upgrade handshake and then carries low-overhead framed messages in both directions.
- The browser API is event-driven and deliberately minimal, which means reconnection, heartbeats, and state recovery are your application's responsibility.
- Scaling WebSocket servers horizontally requires sticky sessions plus a shared pub/sub backbone, since each server holds live, stateful connections.
- Security in production means encrypted wss transport, Origin validation, handshake-time authentication with short-lived tokens, and strict rate and payload limits.
- Choose SSE when the flow is server-to-client only, and WebSockets when the client talks back frequently; WebTransport is the emerging option as browser support matures through 2026.
- If you would rather skip the infrastructure work entirely, managed real-time platforms like VideoSDK handle connection management, scaling, and reliability for you.
Conclusion
This WebSocket guide covered the full journey: how the protocol upgrades an HTTP connection into a persistent channel, how the browser and server sides fit together, and what it takes to run WebSockets securely at scale. The protocol itself is elegant and small, and the real work lives in the production patterns around it, from heartbeats and reconnection to pub/sub scaling and origin checks.
The best next step is hands-on: open your browser's developer tools, connect to a public WebSocket echo service, and watch the frames flow. When you are ready to build something real, whether that is chat, live streaming, or collaborative features, VideoSDK's real-time communication SDKs give you production-grade infrastructure out of the box, and you can start free at app.videosdk.live. What are you building with WebSockets? Drop a comment, I would love to hear what kind of real-time use case you are working on.
Security Considerations
While Websockets provide powerful real-time communication capabilities, they also come with security challenges. Common threats include Cross-Site WebSocket Hijacking, Denial of Service (DoS) attacks, and man-in-the-middle attacks. To mitigate these risks, consider implementing the following security measures:
- Authentication and Authorization: Ensure that only authenticated users can establish Websocket connections.
- TLS/SSL Encryption: Use secure Websockets (
wss://) to encrypt data in transit. - Rate Limiting: Implement rate limiting to prevent DoS attacks.
- Origin Checking: Validate the origin header to prevent Cross-Site WebSocket Hijacking.
By addressing these security considerations, you can create a more secure Websocket implementation.
Use Cases and Examples
Websockets are widely used in scenarios requiring real-time data exchange. Some common applications include:
- Chat Applications: Real-time messaging and notifications.
- Online Gaming: Instant game state updates and interactions.
- Live Sports Updates: Real-time scores and event notifications.
- Collaborative Tools: Real-time collaboration on documents and projects.
Example Case Study
A popular online game uses Websockets to provide real-time interactions between players. The game's server sends instant updates on player actions, ensuring a seamless and interactive gaming experience.
Troubleshooting and Optimization
To ensure optimal performance and reliability of your Websocket implementation, consider the following troubleshooting and optimization tips:
- Connection Issues: Verify the server and client URLs, and check network configurations.
- Message Handling: Implement proper error handling for message parsing and processing.
- Resource Management: Close unused Websocket connections to free up resources.
- Performance Monitoring: Use monitoring tools to track and analyze Websocket performance metrics.
By proactively addressing these issues, you can enhance the efficiency and robustness of your Websocket-based applications.
Conclusion
Websockets have revolutionized real-time communication in web applications, providing a powerful tool for creating responsive and interactive experiences. By understanding and implementing Websockets, developers can build applications that deliver instant updates and seamless communication, enhancing user engagement and satisfaction.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ