


The WebSocket protocol is a standardized, full-duplex communication channel that runs over a single persistent TCP connection, defined in RFC 6455. Unlike HTTP's request-response model, it lets a server push data to a client instantly with minimal overhead, making it the backbone of chat apps, live dashboards, multiplayer games, and AI streaming. Platforms like VideoSDK build their real-time video and audio SDKs on the same persistent-connection principles the WebSocket protocol popularized.
Real-time features are now table stakes for modern applications. A chat app that refreshes every five seconds feels broken. A live dashboard that lags behind reality erodes trust. A multiplayer game with 300 milliseconds of round-trip delay is unplayable. The websocket protocol exists precisely because HTTP, the workhorse of the web, was never designed for any of this.
This article walks through the websocket protocol end to end: why HTTP falls short, how the upgrade handshake works, how binary framing keeps the connection efficient, and what it takes to run WebSocket connections securely at scale. By the end, you'll understand exactly what happens on the wire when a client and server open a WebSocket connection, and when to choose it over alternatives like Server-Sent Events or long polling.
Why Traditional HTTP Falls Short for Real-Time
HTTP is a request-response protocol: the client asks, the server answers, and the connection's purpose ends. That model is perfect for fetching documents and API responses, but it creates a fundamental problem for real-time communication: the server cannot initiate a message. If the server knows something the client needs right now, it has to wait for the client to ask.
Developers have historically worked around this limitation in three ways. Long polling keeps a request artificially open until the server has something to send, then immediately reissues a new request, burning bandwidth and adding reconnect latency on every cycle. Short polling asks the server on a timer, which is simple but wastes requests and guarantees staleness between polls. Server-Sent Events (SSE) opens a one-way stream from server to client, which is elegant for notifications and live feeds but cannot carry messages from the client back up the same channel.
The websocket protocol solves the direction problem outright. After a single HTTP upgrade handshake, the connection stays open as a full-duplex pipe: both sides can send frames at any time, with roughly two bytes of framing overhead per message instead of a fresh set of HTTP headers on every exchange. The latency difference is structural, not incremental.
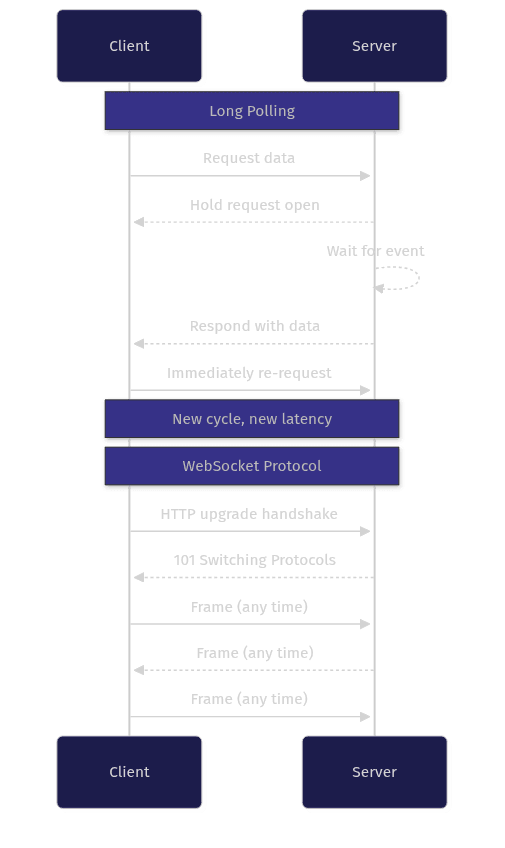
The diagram above shows why the websocket protocol wins for latency-critical features: after the handshake, there is no per-message request cycle at all. Data flows in both directions the instant it is produced.
The WebSocket Handshake: Upgrading from HTTP
Every WebSocket connection begins its life as an ordinary HTTP request. The client sends a specially crafted GET request containing an Upgrade header requesting the websocket protocol, a Connection header signaling an upgrade, a randomly generated Sec-WebSocket-Key, and a Sec-WebSocket-Version header, typically version 13 as defined in RFC 6455.
The server responds, if it agrees, with the status line 101 Switching Protocols. Crucially, it echoes back the upgrade and connection headers and returns a Sec-WebSocket-Accept value. That value is computed by concatenating the client's key with a fixed magic GUID defined in the RFC and hashing the result. This isn't encryption; it's proof that the server actually understands the websocket protocol rather than a generic HTTP intermediary blindly forwarding the request. A server that can't produce the correct accept value is not a real WebSocket endpoint.
From that moment, the TCP connection stops speaking HTTP and speaks only WebSocket frames. The same socket, the same port, a completely different protocol on top.
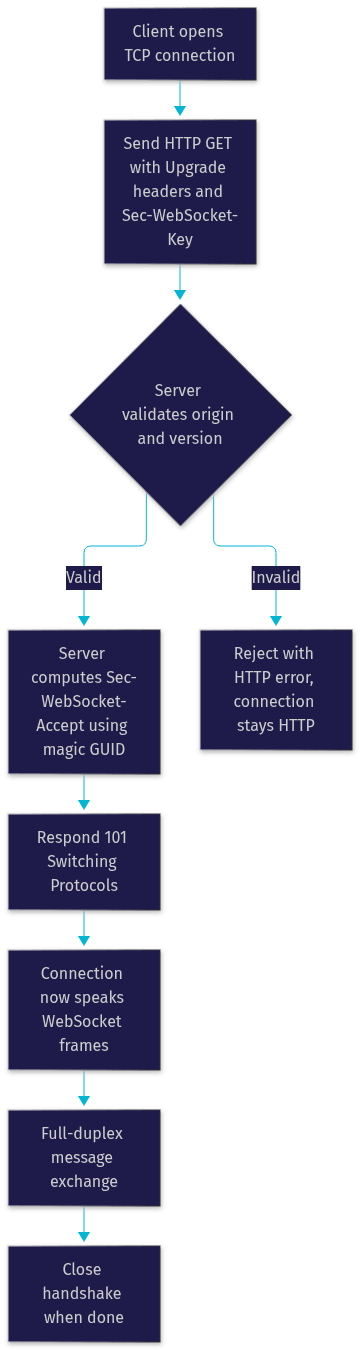
Security starts at the handshake. Servers should validate the Origin header to prevent cross-site WebSocket hijacking, where a malicious page opens a WebSocket to a victim service using the user's ambient credentials. In production, always use wss://, the WebSocket equivalent of HTTPS, so the handshake and every subsequent frame travel inside TLS encryption.
Handshake Headers Deep Dive
The required headers each serve a distinct purpose. The Upgrade header names the target protocol, and the Connection header signals that this request is a protocol upgrade rather than a normal fetch. Sec-WebSocket-Key provides the client-generated nonce for the accept computation, and Sec-WebSocket-Version declares the protocol revision, with 13 being the current standard.
Optional headers add capability negotiation. Sec-WebSocket-Protocol lets the client propose one or more subprotocols, such as a named messaging schema, and the server picks one, ensuring both sides agree on the message format. Sec-WebSocket-Extensions negotiates protocol extensions, most commonly permessage-deflate, which compresses message payloads across the connection. Because these are negotiated at handshake time, both sides know exactly what the connection supports before a single data frame flows.
WebSocket Frame Structure
Once the handshake completes, all communication happens in frames: small binary structures that carry a header, an optional masking key, and the payload. Understanding the frame layout is what separates developers who treat WebSocket as a black box from those who can debug it at the wire level.
The first bit, FIN, indicates whether this frame is a complete message or a fragment of one. Large messages can be split across multiple frames, with the final frame setting FIN to signal completion. Next comes the opcode, a four-bit field identifying the frame type: text, binary, or one of the control frames like ping, pong, and close. Text frames carry UTF-8 encoded strings, while binary frames carry arbitrary bytes, which is what makes the websocket protocol suitable for streaming structured data, media signaling, and machine-to-machine messaging.
The mask bit is where RFC 6455 makes a deliberate asymmetry. Every frame sent from client to server must be masked: the payload is XORed against a 32-bit masking key included in the frame, and the server unmaskes it on receipt. Frames from server to client must not be masked. The reason is historical and defensive: masking prevents malicious web pages from using a browser's WebSocket implementation to inject crafted byte sequences at intermediaries that might misinterpret them, a class of attack against older proxy infrastructure.
Payload length is encoded in a variable number of bits: seven bits for small payloads, an extended 16-bit form for medium messages, and a 64-bit form for very large ones. This variable-length scheme keeps small messages, which are the majority in real-time apps, down to just a few bytes of overhead.
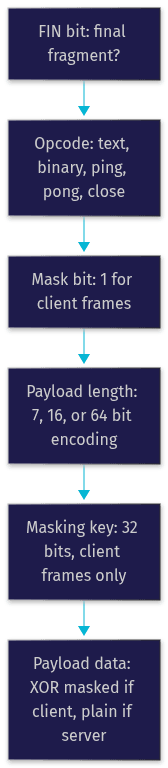
A typical text frame from a browser, for example a chat message, consists of a two-byte header, a four-byte masking key, and the masked payload. The server reads the header, detects the opcode as text, unmasks the payload, and delivers a UTF-8 string to the application layer in a single pass.
Control Frames: Ping, Pong, and Close
Three control frames keep the connection healthy. A ping frame can be sent by either side at any time, and the recipient must respond with a pong frame echoing the ping's payload. These heartbeats detect dead connections that TCP alone might not notice, such as a laptop that went to sleep behind a NAT gateway. The close frame initiates a graceful shutdown: one side signals intent to close, the other acknowledges, and both tear down cleanly rather than leaving half-open sockets. Well-behaved applications send pings on a regular interval, commonly every 30 seconds, and treat missed pongs as a signal to reconnect.
Managing Connections at Scale
A single server can hold tens of thousands of WebSocket connections, but production systems need infrastructure that respects the protocol's long-lived nature. The first hurdle is the proxy and load balancer layer. Because WebSocket connections stay open indefinitely, default HTTP timeouts on reverse proxies will silently kill them. Production configurations must raise or disable idle timeouts, enable upgrade handling, and ensure session affinity so that a reconnecting client lands on a server that holds its session state.
TLS termination is the standard pattern for wss:// traffic: the load balancer decrypts incoming connections, then forwards plain WebSocket frames to backend servers. This centralizes certificate management and offloads cryptographic work, but the internal hop should still run inside a private network.
The second challenge is back-pressure. If a client on a slow network cannot drain its send buffer fast enough, a naive server will buffer unboundedly and exhaust memory. Mature implementations use read and write pumps that pause reading from a fast producer when a slow consumer's buffer crosses a threshold, applying back-pressure end to end. Connection pooling and pub/sub fan-out backends, where each server instance subscribes to a shared message bus, let you horizontally scale to millions of concurrent connections without every server needing every message.
This is exactly the architecture class that real-time platforms industrialize. VideoSDK's real-time communication SDKs, for instance, handle the persistent-connection plumbing, adaptive bitrate, and reconnection logic for video and audio calling across React, Flutter, Android, iOS, and other platforms, so application teams don't have to build and operate this infrastructure themselves. The same scaling principles, heartbeats, affinity, and back-pressure, apply whether you're operating raw WebSocket servers or consuming a managed real-time layer.
Common Use Cases and When to Choose WebSocket Protocol
The websocket protocol shines wherever latency and bidirectionality both matter. Real-time chat is the canonical case: messages flow both ways continuously. Live dashboards for trading, monitoring, and IoT telemetry need server push with sub-second freshness. Multiplayer games depend on low-latency state synchronization in both directions. Collaborative editors like shared documents and whiteboards stream fine-grained edits from every participant simultaneously. And AI streaming has become a major new driver: token-by-token LLM output, voice agent pipelines, and live transcription all benefit from a persistent channel where the server streams and the client can interrupt or steer mid-stream.
But the websocket protocol is not always the right answer. If data only flows from server to client, SSE is simpler, works over plain HTTP infrastructure, and reconnects automatically. If updates are rare or tolerance for staleness is high, plain polling may be entirely adequate.
| Feature | WebSocket Protocol | Server-Sent Events | Long Polling |
|---|---|---|---|
| Direction | Full duplex, both ways | Server to client only | Server to client per request |
| Latency | Lowest, push on both sides | Low for server push | Moderate, reconnect per message |
| Overhead per message | A few bytes of framing | Small event framing | Full HTTP request each cycle |
| Reconnection | Manual or library-managed | Built into the browser | Built into the pattern |
| Infrastructure needs | Upgrade-aware proxies, sticky sessions | Standard HTTP | Standard HTTP |
| Best for | Chat, games, collaborative editing, AI streaming | Notifications, live feeds, dashboards | Legacy clients, rare updates |
The practical rule: choose the websocket protocol when the client also needs to talk back frequently or when message frequency is high in both directions. Choose SSE when the stream is one-way. Choose polling only when simplicity outweighs responsiveness.
Best Practices and Security Tips
Treat a WebSocket endpoint as an always-on, authenticated API surface. Validate the Origin header on every handshake and reject connections from unexpected origins, since browsers send ambient cookies that a hostile page can exploit. Prefer token-based authentication passed during or immediately after the handshake, because standard HTTP cookie semantics don't always map cleanly onto a long-lived socket.
Use subprotocol negotiation to pin your message schema, so both sides fail fast on version mismatches. Apply rate limiting per connection and per user to blunt abuse, and enforce maximum message sizes to prevent a single client from exhausting server memory with a giant frame. Heartbeats via ping/pong should run on a short interval both to detect dead peers and to give load balancers a reason to keep the connection alive. Finally, always serve over wss:// in production, and combine it with sensible timeouts so that abandoned connections are reaped rather than accumulating. For teams building latency-critical features on top of managed infrastructure, reviewing VideoSDK's real-time communication documentation is a fast way to see these patterns applied in production-grade systems.
Definitions Glossary
WebSocket Protocol: A standardized, full-duplex communication protocol defined in RFC 6455 that runs over a single persistent TCP connection after an HTTP upgrade handshake, enabling low-latency bidirectional messaging.
HTTP Upgrade Handshake: The opening exchange in which a client sends a GET request with upgrade headers and the server replies with 101 Switching Protocols, transitioning the connection from HTTP to the websocket protocol.
Sec-WebSocket-Accept: A value the server computes by hashing the client's key with a fixed magic GUID, proving the endpoint genuinely implements the websocket protocol.
Frame Masking: An RFC 6455 rule requiring every client-to-server frame to XOR its payload against a 32-bit masking key, protecting intermediary infrastructure from crafted byte injection.
Ping/Pong Heartbeats: Control frames exchanged at regular intervals to detect dead connections and keep intermediaries from timing out idle sockets.
wss://: The secure WebSocket URI scheme, equivalent to HTTPS, which carries the handshake and all frames inside TLS encryption.
Key Takeaways
- The websocket protocol provides full-duplex, low-latency messaging over a single persistent TCP connection, eliminating the per-message request cycle that makes HTTP slow for real-time features.
- The HTTP upgrade handshake, built around the Sec-WebSocket-Key and Sec-WebSocket-Accept computation, transitions a normal connection into WebSocket mode in one round trip.
- Client-to-server frames must be masked while server-to-client frames are not, a deliberate RFC 6455 design that protects proxy infrastructure from byte-injection attacks.
- Scaling WebSocket systems requires upgrade-aware load balancers, session affinity, TLS termination for wss://, and back-pressure handling to protect memory under slow consumers.
- Choose the websocket protocol when communication is bidirectional and frequent; choose SSE for one-way server push and polling only when responsiveness is optional.
Conclusion
The websocket protocol remains the foundation of real-time web communication in 2026: one handshake, one TCP connection, and a bidirectional channel with a few bytes of overhead per message. Understanding the handshake, framing, heartbeats, and scaling requirements lets you build chat, dashboards, games, and AI streaming features that feel instant rather than eventually consistent. If you're building latency-critical real-time features and want managed infrastructure that already solves connection scaling, adaptive streaming, and reconnection, explore the VideoSDK documentation or try the platform free at app.videosdk.live. What are you building with real-time communication? Drop a comment, I'd love to hear what kind of websocket-powered use case you're working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ