


A websocket proxy is an intermediary server that accepts WebSocket connections from clients (usually browsers) and forwards their messages to upstream services such as TCP servers, SSH daemons, or IoT gateways. It handles the HTTP upgrade handshake, enforces TLS (wss), authenticates clients, and manages long-lived connections that ordinary HTTP reverse proxies were never designed for. If you need browsers to talk to raw TCP services, or you need to scale and secure real-time traffic, a websocket proxy is the layer that makes it possible. VideoSDK's real-time communication platform builds on the same long-lived connection principles, so understanding proxies helps you debug and scale any real-time system.
Introduction
Browsers speak WebSocket. Your database, your SSH daemon, your game server, and your factory-floor IoT gateway speak raw TCP. Something has to translate between the two, and that something is a websocket proxy.
The pattern shows up everywhere once you start looking for it. A multiplayer game needs browser clients to reach a UDP-style game loop. A support engineer wants a web-based terminal into a remote machine. A logistics company wants to stream telemetry from thousands of vehicle modems into a dashboard. None of these work with a plain HTTP request-response cycle, because they all need persistent, bidirectional, low-latency channels.
A websocket proxy also solves problems beyond protocol bridging. It terminates TLS so your upstream services stay simple. It centralizes authentication so every real-time endpoint shares one policy. And it gives you a single place to apply rate limiting, logging, and load balancing for connections that can stay open for hours. This guide walks through what a websocket proxy is, when you need one, how to build and deploy it, and how to keep it fast and secure in production.
What Is a Websocket Proxy?
A websocket proxy is defined as a server that sits between WebSocket clients and backend services, accepting inbound WebSocket connections and relaying their frames to upstream targets over WebSocket, TCP, or another transport. It is not the same thing as a WebSocket server, which terminates the protocol and processes messages itself, and it is not a plain HTTP reverse proxy, which assumes short-lived request-response cycles.
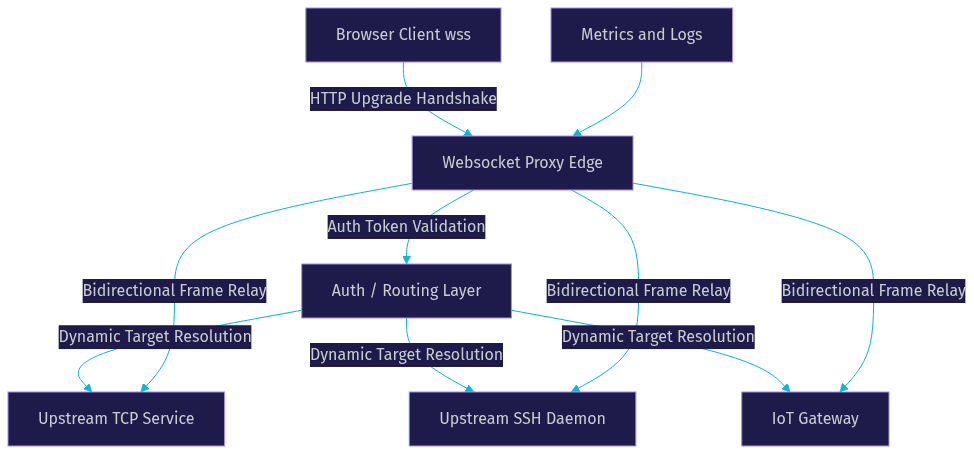
A websocket proxy works by first completing the HTTP upgrade handshake with the client, then establishing its own connection to the upstream target, and finally piping frames bidirectionally between the two for the life of the session. Because WebSocket connections are long-lived, the proxy must track session state, handle disconnects gracefully, and manage thousands of simultaneous open sockets rather than thousands of requests per second.
The websocket proxy architecture is therefore different from a classic reverse proxy in three ways. First, connection lifetime is measured in minutes or hours, not milliseconds. Second, the proxy often needs dynamic target resolution, deciding at handshake time which upstream a given client should reach. Third, back-pressure matters: if an upstream sends data faster than a client can consume it, the proxy must buffer or apply flow control rather than silently dropping frames.
This is the same architectural territory that real-time communication platforms like VideoSDK operate in, where rooms of participants exchange persistent media and data streams through managed infrastructure.
Core Use Cases
Every websocket proxy deployment traces back to one of a handful of recurring scenarios. Understanding which one you are in determines your architecture, your security model, and your scaling strategy.
Real-time gaming and multiplayer
Browser-based multiplayer games need a persistent channel for position updates, chat, and game state. A websocket proxy sits between the browser clients and the authoritative game server, bridging the WebSocket protocol to the game loop's native TCP or internal messaging. The proxy also gives you a natural place to shard players into sessions, authenticate match tokens at handshake time, and drop misbehaving clients without touching game logic.
Remote SSH or terminal access
Web-based terminals, such as cloud IDEs and infrastructure consoles, use a websocket proxy to bridge the browser to an SSH daemon or a shell process on a remote machine. The proxy authenticates the user, opens the upstream session, and pipes keystrokes and output as WebSocket frames. This is one of the most security-sensitive uses of the pattern, because the proxy effectively holds the keys to arbitrary remote execution, so token scoping and audit logging are non-negotiable.
IoT device gateways
IoT fleets often speak MQTT, raw TCP, or vendor-specific protocols that browsers cannot reach. A websocket proxy exposes those device streams to web dashboards, letting operators watch telemetry and send commands in real time. The proxy handles fan-out when many dashboards watch the same device stream, and it isolates the device network from the public internet so only the proxy's authenticated surface is exposed.
Legacy TCP services exposed to browsers
Plenty of valuable software predates the browser era: order-routing systems, industrial controllers, mainframe front-ends. Rewriting them to speak WebSocket is expensive and risky. A websocket proxy lets you wrap the legacy TCP service without touching it, translating between WebSocket frames on the client side and the legacy protocol on the upstream side. The proxy becomes the modernization boundary.
Key Components of a Websocket Proxy
Every production-grade websocket proxy, regardless of implementation language, is built from the same six components. Weakness in any one of them becomes the bottleneck or the vulnerability of the whole system.
Connection handling (handshake, upgrade)
The proxy begins every session by completing the HTTP upgrade handshake: it validates the client's upgrade request, checks the requested sub-protocol against its allow-list, and confirms the connection before any frames flow. Getting this stage right prevents a whole class of failures later, because a rejected or mis-negotiated handshake surfaces immediately as a client-side connection error rather than a mysterious mid-session drop.
Message forwarding (binary vs text)
WebSocket frames come in text and binary flavors, and a good proxy treats them differently. Text frames may pass through UTF-8 validation and can be inspected or rewritten; binary frames should be forwarded as opaque bytes for performance. A proxy that forces everything through text parsing will melt under binary-heavy workloads like game state or terminal streams.
Buffering and queuing
When upstream and client speeds diverge, the proxy needs bounded buffers with explicit overflow policy: block the fast side, drop frames, or close the connection. Unbounded buffering is the classic websocket proxy memory leak, where one slow client on a busy channel slowly consumes the proxy's entire heap.
TLS termination (wss)
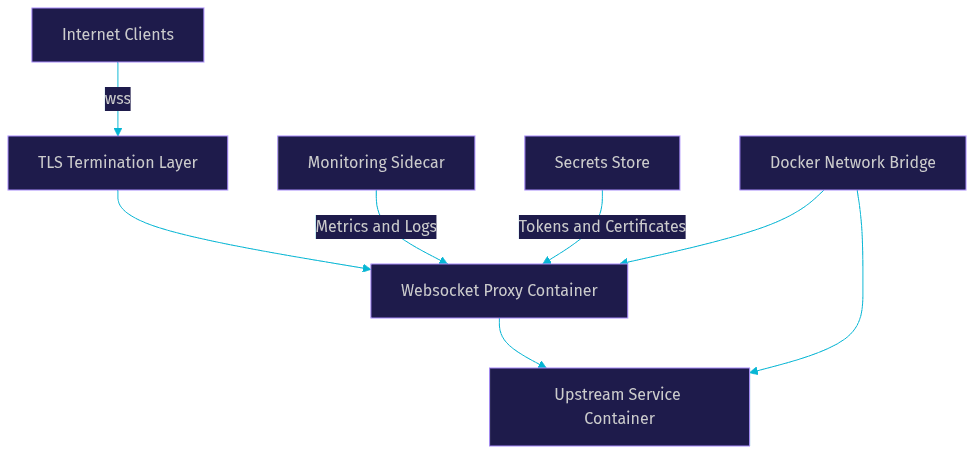
The proxy typically terminates TLS at its edge, presenting a wss endpoint to clients while speaking plain WebSocket or TCP to internal upstreams. This centralizes certificate management and lets internal services stay simple. Some architectures instead do TLS pass-through when upstreams must see client certificates, which trades operational simplicity for end-to-end certificate visibility.
Authentication and access control
The handshake is the natural enforcement point. The proxy validates a token presented by the client during or just after the upgrade, maps it to an identity and a set of permitted upstream targets, and rejects anything else before a single frame is forwarded. This is the same token-based model VideoSDK uses for room authentication, where short-lived credentials gate access to real-time sessions.
Dynamic target resolution
In multi-tenant systems, the proxy decides at handshake time which upstream a client should reach, based on the requested path, the authenticated identity, or a routing table. This turns the proxy into a real router, not just a forwarder, and it is where SSRF risks concentrate if target selection is influenced by client input.
The overall data flow looks like this:
Choosing the Right Implementation Language
The language you build your websocket proxy in shapes its performance ceiling and its operational character more than almost any other decision.
Go is the pragmatic default for most teams in 2026: goroutines map naturally onto long-lived connections, the standard library handles the upgrade handshake well, and single binaries deploy trivially into containers. Rust offers the highest throughput and lowest, most predictable memory footprint, which matters when you are holding tens of thousands of open sockets per instance, at the cost of a steeper development curve. Node.js is the fastest path to a working proxy for teams already living in JavaScript, and its event loop handles I/O-bound relay well, though CPU-heavy frame processing can stall all connections on a thread. Python is excellent for prototypes and for proxies that need rich per-message logic, but per-connection overhead limits raw scale. Java, with virtual threads now mature, remains a strong choice in enterprise environments where the surrounding infrastructure is already JVM-based.
In practice, teams consistently find that the bottleneck is rarely the language and almost always the buffering, back-pressure, and load-balancing design. Pick the ecosystem your team can operate confidently at 3 a.m., then invest the saved effort in the architecture.
Deployment Strategies
How you deploy a websocket proxy determines how it fails, how it scales, and how much of your evening it costs you.
Containerized deployment (Docker)
Containerizing the proxy isolates its dependencies and makes TLS configuration, buffer limits, and routing rules explicit and versioned. A typical Docker setup runs the proxy container behind a TLS-terminating front layer, with configuration injected through environment variables and secrets mounted separately. The key detail most teams learn the hard way: container-level health checks must verify an actual WebSocket handshake, not just an open TCP port, because a proxy can accept connections while failing every upgrade.
Orchestration with Kubernetes
Kubernetes suits websocket proxies well because long-lived connections benefit from stable pod identity and graceful drain. The critical configuration is load balancer session affinity and connection draining: when a pod is terminated, its open WebSocket sessions must either be drained or allowed to reconnect through another pod, and clients must implement reconnect logic with exponential backoff. Headless services and proper readiness probes prevent the classic failure where a not-yet-ready pod receives handshakes it cannot complete.
Serverless edge options
Edge runtimes such as Cloudflare Workers and Deno Deploy now support WebSocket forwarding, which lets you place the proxy's entry point geographically close to clients. This cuts handshake latency dramatically for global audiences, though edge functions have execution-time and state constraints that make them better as a smart front door than as a full buffering relay. A common hybrid routes and authenticates at the edge, then relays to a central proxy tier.
A containerized topology typically looks like this:
Security Best Practices
A websocket proxy is by design a hole in your network perimeter, so its security posture deserves the same rigor as your public API surface.
Enforcing TLS (wss)
Terminate TLS at the proxy edge and refuse plain ws connections in production, full stop. WebSocket connections carry session tokens and sensitive payloads for hours, and a single unencrypted hop exposes all of it. Automate certificate rotation so an expired cert does not silently break every real-time session at once.
Authentication hooks (tokens, JWT)
Validate a short-lived token at handshake time, ideally a JWT with an expiry and an audience claim that names the permitted upstream. Never accept a bare upstream address from the client. The token should encode what the client may reach, and the proxy should derive the target from the token, not from the request.
Rate limiting and DoS protection
Because connections are long-lived, rate limiting must operate at two levels: connection establishment (to stop handshake floods) and frame throughput (to stop a single authenticated client from saturating an upstream). Bounded buffers double as a DoS defense, since a flooding client hits the buffer ceiling and gets its connection closed rather than consuming unbounded memory.
Preventing SSRF in dynamic routing
If your proxy resolves targets dynamically, validate every resolved address against an allow-list of hosts and networks, and explicitly block link-local and metadata addresses. An SSRF bug in a websocket proxy is worse than in an HTTP proxy, because the resulting access is persistent and bidirectional.
Logging and monitoring
Log handshakes, authentications, and target resolutions with correlation IDs, and track open-connection count, frame throughput, and buffer occupancy as first-class metrics. When something goes wrong at 3 a.m., you want to know which upstream a given client was routed to and when, which is exactly the audit trail a well-instrumented proxy provides.
Performance Tuning Tips
A websocket proxy that works on localhost can still fall over in production. These four areas are where real capacity comes from.
Connection pooling and keep-alive
Reuse upstream connections where the protocol allows it, and enable TCP keep-alive on both legs so dead connections are detected in minutes rather than lingering for hours. Half-open connections are the silent capacity thief in long-lived systems.
Message size limits and compression
Set an explicit maximum frame size and reject anything larger. Compression (per-message deflate) helps text-heavy traffic like chat, but costs CPU on binary-heavy streams and can enable compression-based side channels if applied across authenticated boundaries. Enable it selectively, not globally.
Back-pressure handling
Propagate back-pressure rather than buffering infinitely: when a client's send buffer fills, pause reads from the upstream until it drains. This keeps memory flat under load and degrades gracefully instead of catastrophically.
Horizontal scaling with load balancers
Scale by adding proxy instances behind a load balancer that supports long-lived connections, and make sure the balancer's idle timeout exceeds your expected session duration. A load balancer that silently drops idle WebSocket connections at 60 seconds will generate a support ticket storm you will not forget. This is the same scaling discipline that real-time platforms like VideoSDK's interactive live streaming apply to audience-scale sessions.
Common Pitfalls and Troubleshooting
Most websocket proxy failures cluster into a short list, and each has a telltale signature.
Handshake failures usually mean a mismatch between what the client offers and what the proxy allows: a sub-protocol the proxy does not recognize, a missing authentication token, or an intermediate layer stripping the upgrade headers. Diagnose by comparing the exact headers the client sends with what the proxy logs as received, remembering that corporate proxies and some CDNs still mangle upgrade requests.
Mid-session drops point to idle timeouts on any hop in the chain: the load balancer, the container runtime, or the upstream itself. Implement heartbeat pings at the application level so every layer sees regular traffic. Reconnect storms after an outage point to missing jitter in client back-off logic, where every client retries simultaneously and knocks the recovering proxy back down.
Finally, slow memory growth across days is almost always an unbounded buffer or a leaked session entry for connections that were never cleaned up on disconnect. Instrument buffer occupancy per connection and you will find the culprit quickly.
Future Trends for Websocket Proxies
The WebSocket protocol is being joined by newer transports that change what a proxy must do. WebTransport, built on HTTP/3, offers datagram and unreliable-ordered streams alongside reliable ones, which suits game state and live media far better than a single ordered stream. HTTP/3 itself removes head-of-line blocking at the transport layer, so a lost packet no longer stalls every message behind it.
The proxy's role does not disappear in this future; it shifts. Instead of relaying frames, the next generation of proxies will negotiate between transports, falling back from WebTransport to WebSocket for older clients, and applying the same authentication, routing, and back-pressure logic across both. Teams building websocket proxies in 2026 should design their routing and auth layers to be transport-agnostic, so the relay layer can be swapped as client support matures. Real-time platforms are already moving this direction, and the VideoSDK docs are a good reference for how managed infrastructure abstracts these transport decisions away from application developers.
Definitions Glossary
Websocket proxy: A server that accepts WebSocket connections from clients and relays their frames to upstream services over WebSocket, TCP, or another transport, handling the upgrade handshake, authentication, and session lifecycle in between.
HTTP upgrade handshake: The initial HTTP request and response exchange that converts a plain HTTP connection into a WebSocket connection, negotiated once at the start of every session.
wss (WebSocket Secure): The WebSocket protocol running over TLS, the only acceptable mode for production traffic because it encrypts every frame for the life of the connection.
Back-pressure: The flow-control technique of slowing or pausing reads from a fast sender when a slow receiver cannot keep up, keeping memory usage flat instead of buffering without limit.
Dynamic target resolution: The proxy's decision, made at handshake time, of which upstream service a client should be connected to, based on identity, path, or routing rules rather than client-supplied addresses.
SSRF (Server-Side Request Forgery): An attack where client-controlled input makes a server initiate connections to internal addresses; in a websocket proxy, unvalidated dynamic routing turns this into persistent internal network access.
Key Takeaways
- A websocket proxy bridges browser WebSocket clients to TCP-based upstreams like SSH daemons, game servers, IoT gateways, and legacy services, which no plain HTTP reverse proxy can do well.
- The six core components are handshake handling, message forwarding, bounded buffering, TLS termination, authentication, and dynamic target resolution, and weakness in any one becomes the system's bottleneck.
- Security lives at the handshake: enforce wss, validate short-lived tokens, derive upstream targets from the token rather than the client, and allow-list every dynamically resolved address to prevent SSRF.
- Performance comes from back-pressure propagation, explicit frame size limits, keep-alive on both legs, and load balancers whose idle timeouts exceed real session durations.
- WebTransport and HTTP/3 are reshaping the transport layer, so design your routing and authentication layers to be transport-agnostic while the standards mature.
Conclusion
A websocket proxy is the connective tissue between the browser world and everything that already speaks TCP. Get the architecture right, with bounded buffers, handshake-time authentication, and honest back-pressure, and it will carry real-time traffic reliably at scale. Get it wrong, and you will meet every failure in the troubleshooting section personally.
Before picking a language or a deployment target, map your use case: gaming, terminal access, IoT, or legacy bridging each push on different parts of the design. And if your real-time ambitions extend toward embedded video, voice, or interactive streaming, evaluate a managed real-time platform first, because VideoSDK handles rooms, tokens, adaptive streaming, and scaling so you can focus on your product. You can start free at app.videosdk.live/login. What are you building that needs a websocket proxy? Drop a comment, I'd love to hear which of these use cases you are working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ