


A ping pong frame websocket mechanism is a heartbeat protocol where one endpoint sends a ping control frame (opcode 0x9) and the other responds with a pong frame (opcode 0xA) to confirm the connection is alive. Defined in RFC 6455, this exchange lets servers and clients detect dead connections, clean up resources, and trigger reconnection logic before users notice. VideoSDK applies similar keepalive principles in its real-time communication SDKs to maintain sub-300ms latency across network changes.
Real-time applications live or die by the quality of their persistent connections. When a user joins a multiplayer game, a chat room, or a live streaming session, the server opens a WebSocket and expects it to stay open for the session duration. But networks are unreliable. NAT timeouts, firewall state expirations, Wi-Fi drops, and mobile network switches silently kill connections without sending a TCP FIN packet. The server never learns the socket is dead. The user appears online but is unreachable.
The ping pong frame websocket mechanism solves this. By exchanging lightweight control frames at regular intervals, both endpoints confirm the connection is still viable. If a pong response does not arrive within a timeout window, the endpoint marks the connection as stale, closes the socket, and either cleans up or attempts reconnection. This article walks through how the mechanism works, how to implement it on both sides, and how to tune it for performance and security.
Understanding Ping Pong Frame WebSocket
The WebSocket protocol defines a frame-based message model where every piece of data sent over the connection is packaged into a structured frame with an opcode that identifies its type.
The ping pong frame websocket mechanism uses two specific control frame opcodes defined in RFC 6455: opcode 0x9 for ping frames and opcode 0xA for pong frames. These are control frames, not data frames, which means they are handled at the protocol layer rather than passed up to the application logic. This separation is important because it allows heartbeat processing to happen even when the application is busy handling other messages.
RFC 6455, published by the IETF, specifies that either the client or the server may send a ping frame at any time. The receiving endpoint must respond with a pong frame as soon as practical. The pong frame must carry back the same payload data that was included in the ping, which allows the sender to match responses to requests and measure round-trip time. A pong frame may also be sent unsolicited as a one-way heartbeat, though this is less common in practice.
The typical use cases for ping pong frames span any application that maintains long-lived WebSocket connections. Multiplayer game servers use them to detect disconnected players within seconds rather than waiting minutes for a TCP timeout. Chat applications rely on them to update presence status accurately. Live streaming platforms use them to keep viewer connections alive through proxy servers and CDNs that might otherwise drop idle sockets. VideoSDK's real-time communication SDKs, which build on WebRTC and related transport protocols, apply analogous heartbeat and keepalive strategies to maintain connection liveness across unpredictable network conditions. You can explore how VideoSDK manages participant connections in its VideoSDK React SDK quickstart guide.
Why Ping Pong Frames Are Essential
Without a heartbeat mechanism, WebSocket connections degrade into ghost connections that consume server resources without serving any user.
A ghost connection occurs when the network path between client and server breaks silently, leaving the TCP socket half-open on the server side. The server continues allocating memory, file descriptors, and event loop attention to a participant who is already gone. The operating system has no way to know the connection is dead until a TCP keepalive probe eventually fails, which can take minutes or even hours depending on kernel defaults.
The consequences compound quickly at scale. A chat server managing 10,000 concurrent connections might accumulate hundreds of ghost sockets per hour if users are on flaky mobile networks. Each ghost connection holds a buffer, a session object, and potentially a presence record that misleads other users into thinking someone is online. Memory leaks build up. Load balancers route traffic to instances that are secretly overloaded with dead sockets. User experience suffers when messages are sent to participants who will never receive them.
Ping pong frames solve this by giving the server a deterministic way to test connection liveness. If a client does not respond to a ping within a configured timeout, the server closes the socket and fires disconnection events. The application can then clean up session state, notify other participants, and free resources. This is the same principle VideoSDK uses in its REST API for room and participant management, where server-side orchestration detects inactive participants and deactivates rooms programmatically.
Implementing Ping Pong Frame WebSocket
The first implementation decision is determining which endpoint initiates the ping.
In most architectures, the server sends pings because it has the most to lose from ghost connections. Server-initiated pings let the server control the detection cadence and enforce timeout policies uniformly across all connected clients. However, client-initiated pings are useful when the client needs to keep NAT bindings alive or when the server is behind a load balancer that drops idle connections after a fixed period.
Configuring Ping Intervals and Timeouts
Configuring ping intervals requires balancing detection speed against overhead. A 30-second interval is a common default for general-purpose applications. Latency-sensitive applications like multiplayer games often use 5 to 10 seconds. The timeout threshold, which is how long the sender waits for a pong before declaring the connection dead, is typically set to one to three times the ping interval. A shorter timeout detects failures faster but increases false positives on congested networks.
Payload Handling and Echo Data
Payload handling is straightforward but worth noting. RFC 6455 allows ping frames to carry optional application data, and the pong frame must echo that data back. This payload can be used to carry a timestamp for round-trip time measurement, a sequence number for matching requests to responses, or a random nonce to prevent replay. The payload should be small, typically under 125 bytes, since control frames are limited to that size by the protocol specification.
Best-Practice Defaults for Latency-Sensitive Apps
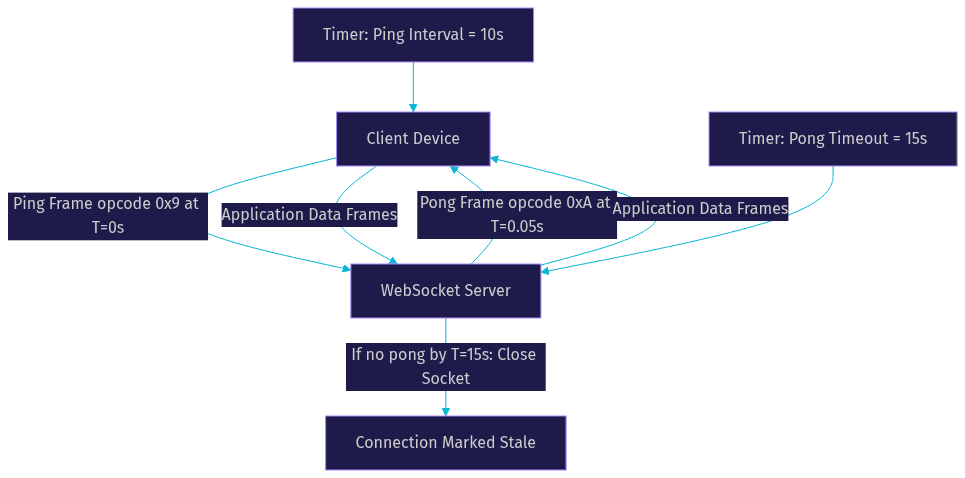
For latency-sensitive real-time applications, best practice defaults include a 10-second ping interval, a 15-second pong timeout, and a payload containing a monotonic timestamp. These values detect dead connections within 25 seconds worst case while adding negligible bandwidth overhead. VideoSDK's network-adaptive streaming applies similar monitoring principles, adjusting bitrate and resolution based on real-time network quality feedback rather than relying on a single heartbeat threshold.
Ping and Pong Frame Exchange Sequence
The following diagram illustrates the timing relationship between ping and pong frames in a typical WebSocket session:
Server-Side Strategies
A well-designed server-side ping strategy starts with a scheduled timer that iterates over all active WebSocket connections at the configured interval.
For each connection, the server sends a ping frame and records the timestamp. A separate monitoring loop checks whether each connection has received a pong within the timeout window. Connections that miss the deadline are closed gracefully with a normal close code, and the application layer receives a disconnection event to trigger cleanup. This two-loop design separates the sending concern from the validation concern, which keeps the code maintainable and allows independent tuning of each phase.
Scaling in Clustered Environments
In clustered environments, the strategy becomes more complex. When WebSocket connections are distributed across multiple server nodes behind a load balancer, each node must manage its own ping schedule for its local connections. Shared state, such as presence or session data, must be updated through a distributed store like Redis or a pub/sub mechanism so that all nodes agree on which participants are alive. Some architectures use a dedicated heartbeat service that runs independently from the application servers, sending pings through a reverse proxy layer and aggregating liveness results.
TLS and Firewall Implications
TLS-protected WebSocket connections (WSS) add encryption overhead to every frame, including ping and pong control frames. This overhead is minimal for small payloads but should be accounted for in capacity planning. Firewalls and NAT devices between the client and server may have their own idle timeout policies, typically ranging from 30 to 60 seconds. If the ping interval exceeds the firewall timeout, the firewall may drop the connection state before the next ping arrives. Setting the ping interval shorter than the shortest expected firewall timeout prevents this issue. The W3C WebRTC specification addresses similar keepalive requirements for peer connections, and VideoSDK's infrastructure handles these concerns automatically for developers using its SDKs.
Client-Side Strategies
Browser-based WebSocket clients handle incoming ping frames automatically at the browser level, which means application developers rarely need to write custom pong response logic.
When the server sends a ping, the browser's WebSocket implementation responds with a pong without any application code involvement. This is mandated by RFC 6455 and implemented consistently across modern browsers including Chrome, Firefox, Safari, and Edge. The application layer never sees the ping or pong frame directly. This means browser-based applications get heartbeat support for free as long as the server initiates the pings.
Custom Client Implementations
Native clients and custom WebSocket implementations have more flexibility. A native mobile client may choose to send its own pings to keep NAT bindings alive, especially on cellular networks where carrier-grade NAT devices aggressively reclaim idle port mappings. The client sends a ping at a regular interval and expects a pong from the server within a timeout. If the pong does not arrive, the client initiates reconnection logic rather than waiting indefinitely.
Handling Missed Pongs with Exponential Backoff
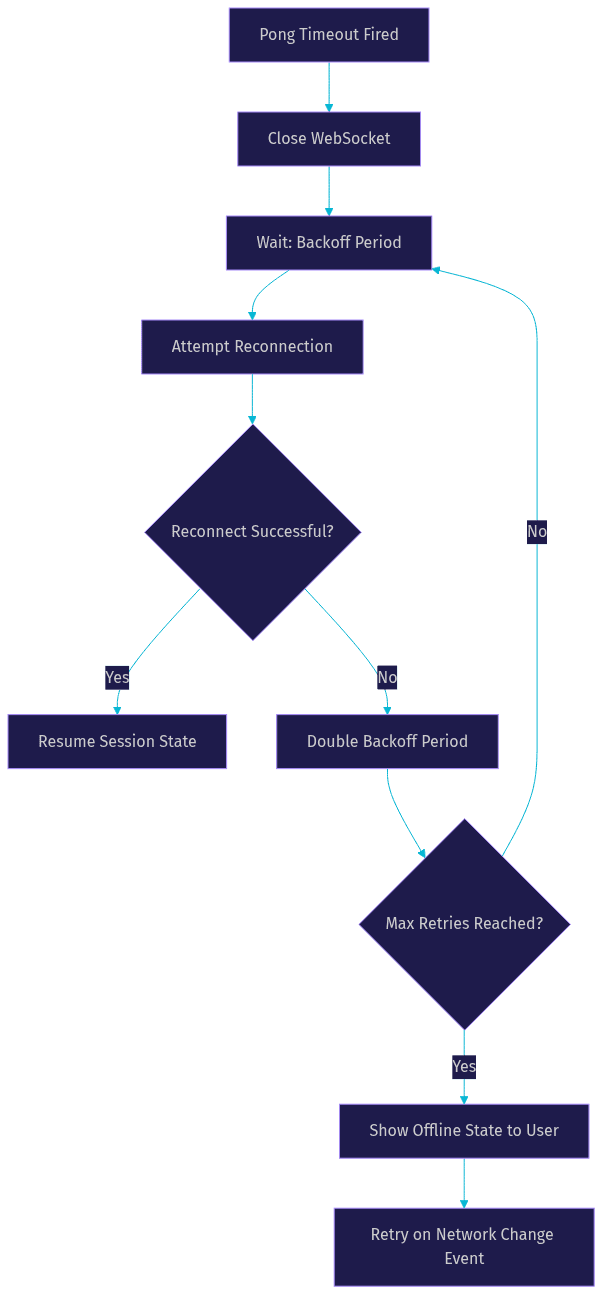
Handling missed pongs on the client side should follow an exponential backoff reconnection strategy. When a pong timeout fires, the client closes the current socket, waits for an initial backoff period (typically 1 second), and attempts to reconnect. Each subsequent failure doubles the wait time, capped at a maximum (typically 30 seconds). This prevents thundering herd problems when a server restarts and thousands of clients attempt reconnection simultaneously. The client should also preserve session state and resume the session after reconnection rather than starting fresh, which is the approach VideoSDK uses when participants experience network interruptions during a video calling session.
Reconnection Flow After Missed Pong
The following diagram shows the decision flow when a client detects a missed pong and enters reconnection logic:
Performance and Latency Impact
Ping frequency directly influences both detection speed and bandwidth consumption, and finding the right balance is a core performance tuning task.
A 1-second ping interval on a connection with 50ms round-trip time adds approximately 1 kilobyte per minute of overhead per connection, which is negligible for most applications. However, at 10,000 concurrent connections, even small per-connection overhead multiplies into meaningful aggregate traffic. The key is finding the interval that detects failures fast enough for your application's user experience requirements without generating excessive control traffic.
Round-trip time measurement using ping payloads provides a useful side benefit. By embedding a timestamp in the ping payload and comparing it to the pong arrival time, the server can track per-connection latency trends. Sudden latency spikes may indicate network degradation before the connection fully drops, allowing proactive measures like switching to a lower bitrate stream or alerting the client to prepare for reconnection. The RFC 6455 specification defines the frame format that makes this measurement possible.
Security Considerations
Ping flood attacks are a real threat where a malicious client sends ping frames at high frequency to exhaust server resources.
The server must respond to each ping with a pong, and processing thousands of pings per second from a single client can degrade performance for legitimate connections. Mitigation strategies include rate limiting ping frames per connection, enforcing a minimum interval between accepted pings, and limiting ping payload size to prevent memory exhaustion from large echo buffers. A well-configured server should reject pings that arrive faster than the negotiated heartbeat interval or that carry payloads exceeding a reasonable threshold.
Authentication of Control Frames
Authentication of control frames is inherent in the WebSocket protocol model. Because ping and pong frames are processed at the protocol layer, they do not pass through application-level authentication middleware. However, the WebSocket handshake itself should occur over WSS (TLS-protected WebSocket) to prevent man-in-the-middle attacks on the initial connection upgrade. Once the TLS tunnel is established, all frames including ping and pong are encrypted. Server-side validation of the origin header during the handshake prevents cross-site WebSocket hijacking, as documented by the Mozilla Developer Network WebSocket guide.
Real-World Example: Multiplayer Ping Pong Game
Consider a real-time multiplayer ping pong game where two players compete over WebSocket connections to a game server.
The server maintains authoritative game state, processing player inputs and broadcasting position updates at 60 frames per second. Each player connects via a WebSocket and sends input events as they move their paddle. The game server sends a ping frame to each player every 5 seconds. If a player's network drops, the server detects the missed pong within 10 seconds and marks the player as disconnected.
The game logic pauses the match, notifies the opponent, and starts a grace period during which the disconnected player can reconnect and resume. Without this mechanism, a disconnected player's paddle would freeze in place, the opponent would keep scoring against a ghost, and the match result would be unfair. The ping pong frame websocket heartbeat ensures that disconnections are detected and handled within a predictable window, preserving game integrity.
This architecture mirrors what VideoSDK enables for real-time applications. In a VideoSDK-powered multiplayer experience, the SDK handles connection monitoring, reconnection, and participant lifecycle events so developers can focus on game logic rather than transport reliability. The same heartbeat principles that keep a WebSocket alive in a game server keep VideoSDK participants connected through network switches, Wi-Fi drops, and cellular handoffs.
Common Pitfalls and Debugging Tips
The most frequent mistake is setting ping intervals too long, which delays failure detection and allows ghost connections to accumulate.
A 5-minute interval might seem efficient, but it means the server cannot detect a dead connection for up to 10 minutes (interval plus timeout). Users on mobile networks switch between Wi-Fi and cellular multiple times per session, and long intervals leave ghost connections accumulating for far too long. Stick to 10 to 30 seconds for most applications.
Another common error is ignoring pong errors. Some implementations log ping sends but never check whether pongs arrive. The ping is useless without the pong validation step. Always implement the timeout check and the close-on-miss logic together.
Firewall blocking is a subtle issue. Corporate firewalls and some cloud provider security groups may block WebSocket traffic entirely or drop connections that appear idle. If pings are not getting through, check firewall rules for the WebSocket port, verify that the WSS handshake completes, and use network tracing tools to confirm frame delivery.
For debugging, start with server-side metrics that track ping send counts, pong receive counts, and timeout-triggered closures per connection. A healthy server should see nearly equal ping and pong counts. A growing gap indicates network issues or client bugs. Library-level logs from your WebSocket library can reveal whether frames are being sent and received at the expected cadence. Network packet captures can confirm frame delivery at the transport layer.
Definitions Glossary
Ping Frame: A WebSocket control frame with opcode 0x9 that tests whether the remote endpoint is still responsive. The sender expects a pong frame in reply within a configured timeout period.
Pong Frame: A WebSocket control frame with opcode 0xA that acknowledges a received ping frame. The pong must echo back the payload data from the originating ping, enabling round-trip time measurement.
Control Frame: A WebSocket frame type used for protocol-level signaling rather than application data transfer. Ping, pong, and close frames are all control frames, limited to 125 bytes of payload.
Ghost Connection: A TCP connection that appears open on the server but where the client is no longer reachable. Ghost connections waste server resources and cause inaccurate presence status.
Heartbeat Interval: The time between successive ping frame transmissions. Shorter intervals detect failures faster but increase bandwidth and processing overhead.
Exponential Backoff: A reconnection strategy where the wait time between retry attempts doubles after each failure, preventing connection storms when a server restarts or a network partition resolves.
Key Takeaways
- Ping pong frame websocket mechanisms are defined in RFC 6455 as control frames with opcodes 0x9 and 0xA, enabling connection liveness detection without application-level overhead.
- Servers should typically initiate pings to control detection cadence and enforce uniform timeout policies across all connected clients.
- Ping intervals should be shorter than the shortest expected firewall or NAT idle timeout, typically 10 to 30 seconds for most applications.
- Client-side reconnection after a missed pong should use exponential backoff to prevent thundering herd problems during server restarts or network partitions.
- VideoSDK's real-time communication SDKs handle connection monitoring and reconnection automatically, applying the same heartbeat principles described here so developers can focus on application logic.
Conclusion
Ping pong frame websocket mechanisms are the foundation of reliable real-time communication over persistent connections. Without them, servers accumulate ghost connections, users see stale presence, and applications degrade silently. By implementing a well-tuned heartbeat strategy with appropriate intervals, timeouts, and reconnection logic, you can build WebSocket-based applications that survive network instability gracefully. Audit your heartbeat settings, monitor ping and pong counts, and treat connection health as a first-class metric. If you are building real-time video, audio, or interactive streaming features, explore how VideoSDK handles connection reliability and network adaptation out of the box. You can sign up for free at app.videosdk.live/login and start building in minutes. What are you building with real-time connections? Drop a comment below, I would love to hear what kind of WebSocket or RTC use case you are working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ