


A Google STUN server is a public STUN endpoint hosted by Google that helps WebRTC clients discover their public IP address and port after Network Address Translation (NAT). Developers use Google STUN servers (stun.l.google.com:19302 and variants) as default ICE candidates in peer-to-peer video and audio calling applications. VideoSDK handles STUN and TURN configuration automatically, but understanding how Google STUN works helps you debug connectivity issues and build more reliable real-time communication infrastructure.
Reliable NAT traversal is the single most common failure point for real-time communication apps. When two browsers try to establish a direct peer-to-peer video call, they first need to discover each other's routable network addresses. Without that discovery step, the call never connects. That is where a STUN server becomes essential, and Google's public STUN infrastructure has become the default choice for developers worldwide.
Google operates a globally distributed set of STUN servers that respond to discovery requests in milliseconds. Most WebRTC tutorials and SDKs ship with Google STUN addresses pre-configured because they are free, reliable, and require no signup. But relying on them without understanding how they work, when they fail, and when you need a TURN server instead leads to flaky calls and frustrated users. This guide covers everything from the STUN protocol itself to production-grade troubleshooting and security considerations.
What Is a STUN Server?
A STUN server is a network service that helps devices behind NAT routers discover their public IP address and port. STUN stands for Session Traversal Utilities for NAT, and it is defined by the IETF in RFC 5389. Without a STUN server, a device sitting behind a home or corporate router only knows its private IP address (something like 192.168.x.x), which is useless for direct peer-to-peer connections across the internet.
VideoSDK's real-time communication infrastructure uses STUN as part of its ICE (Interactive Connectivity Establishment) framework to ensure participants can reach each other. When you build a video calling app with VideoSDK, the platform manages STUN and TURN negotiation under the hood, but the underlying protocol mechanics remain the same.
STUN Protocol Basics
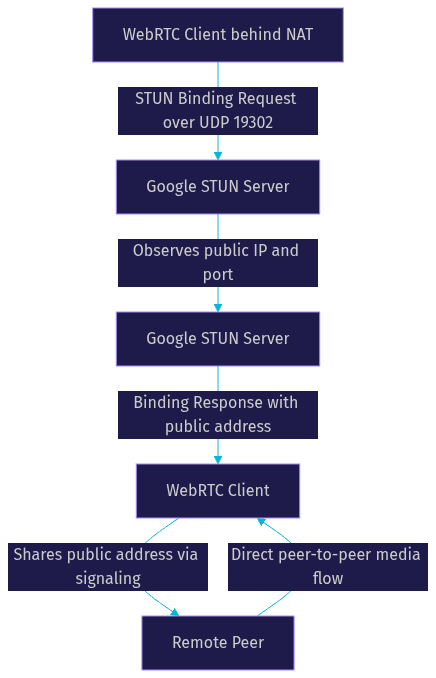
The STUN protocol operates over UDP and follows a simple request-response model. A client sends a STUN Binding Request to the server. The server observes the source IP address and port from which the request arrived, which is the public address after NAT translation. The server then sends a Binding Response back to the client containing that observed public address. RFC 5389 also defines attributes for message integrity, fingerprinting, and error handling, but the core flow is straightforward: ask the server what address it sees, and use that answer to establish direct connections.
NAT Traversal Explained
Network Address Translation allows multiple devices on a private network to share a single public IP address. While NAT solves IPv4 address exhaustion, it breaks direct inbound connections. STUN solves this by revealing the public mapping. When a WebRTC client learns its public IP and port from a STUN server, it shares that address with the remote peer through signaling. Both peers then attempt to connect directly using those public addresses. This works for many NAT types but fails for symmetric NAT, where the router assigns a different public port for each destination. In those cases, a TURN server becomes necessary to relay media traffic.
Google STUN Server Overview
Google maintains a fleet of public STUN servers that have become the de facto default for WebRTC development. These servers are free to use, require no authentication, and are backed by Google's global infrastructure. Most WebRTC examples, including those in the W3C WebRTC specification, reference Google STUN addresses as their starting configuration.
The servers run on UDP port 19302 and respond to standard STUN Binding Requests as defined in RFC 5389. Because Google operates these servers within its existing cloud infrastructure, they benefit from the same global anycast routing and redundancy that powers Google's other services. This means a developer in Mumbai and a developer in São Paulo both get low-latency responses from the nearest Google edge location.
Official Google STUN Addresses
Google exposes five public STUN server addresses, all listening on UDP port 19302. The primary address is stun.l.google.com:19302, and Google also operates stun1.l.google.com:19302, stun2.l.google.com:19302, stun3.l.google.com:19302, and stun4.l.google.com:19302. All five servers function identically and serve the same purpose: responding to STUN Binding Requests with the client's public IP and port. Developers typically include one or two of these addresses in their ICE server configuration. Including more than two rarely improves reliability because they all resolve to the same Google infrastructure.
Global Reach and Reliability
Google's STUN servers benefit from the company's extensive edge network, which spans dozens of data centers worldwide. This geographic distribution means STUN requests typically complete in under 50 milliseconds from most regions. In practice, developers report near-100% uptime for Google STUN, though Google does not publish an official SLA for these servers. Because they are free and unauthenticated, Google imposes rate limits to prevent abuse. For production applications with high call volumes, relying solely on Google STUN without a fallback plan is risky. VideoSDK's real-time communication infrastructure includes managed STUN and TURN servers with guaranteed uptime, making it a more dependable choice for production deployments.
Using Google STUN Server in WebRTC
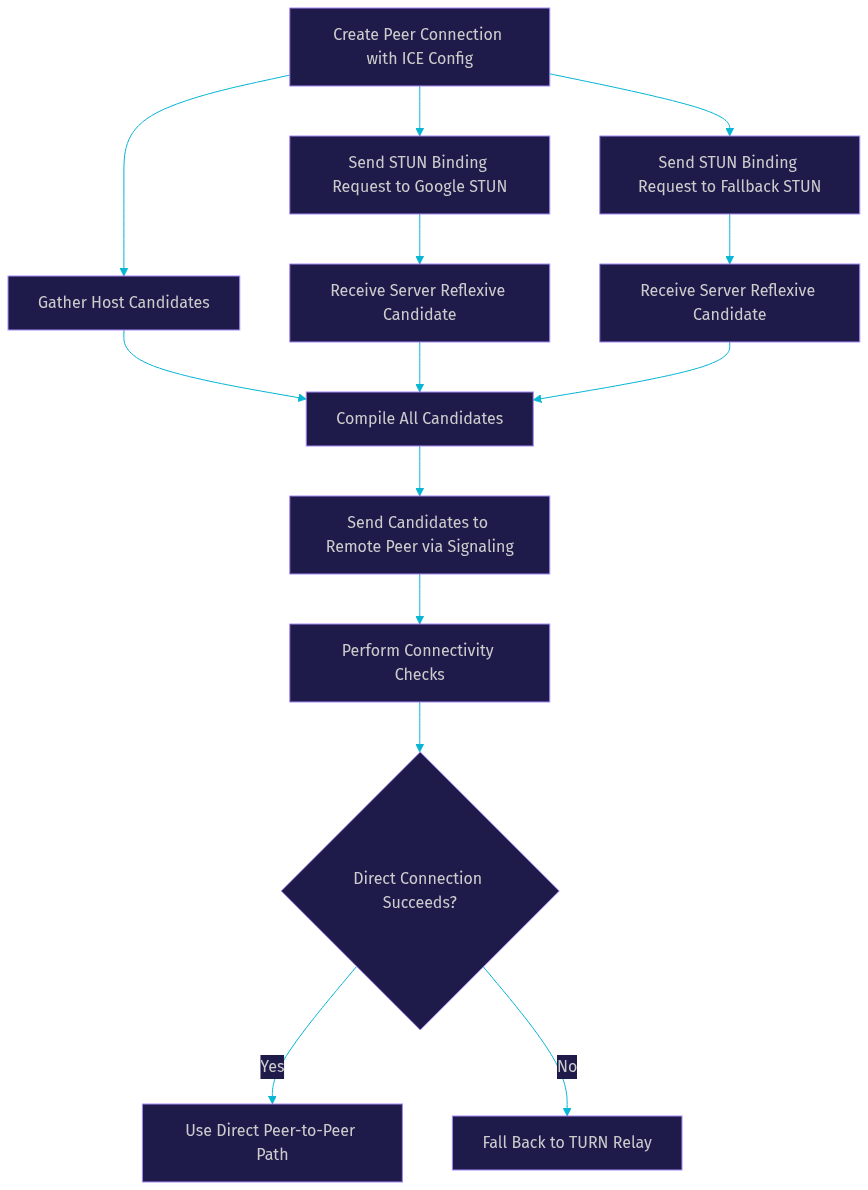
WebRTC uses the ICE framework to find the best possible network path between two peers. ICE gathers candidates from multiple sources: local network interfaces (host candidates), STUN servers (server reflexive candidates), and TURN servers (relayed candidates). Google STUN servers participate in the server reflexive candidate gathering phase, which is usually the most important phase for establishing direct peer-to-peer connections.
When you configure a WebRTC peer connection, you provide a list of ICE servers. Each entry specifies a URL (stun:stun.l.google.com:19302) and optional credentials. STUN servers do not require credentials, so Google STUN entries are simple URL-only configurations. The browser or native SDK then contacts each STUN server during ICE gathering and collects the public addresses returned.
ICE Candidate Gathering
ICE candidate gathering begins the moment a WebRTC peer connection is created with an ICE server configuration. The client sends STUN Binding Requests to each configured STUN server simultaneously. Each server responds with the public IP and port it observes. These become server reflexive candidates (type srflx). The client also gathers host candidates from local network interfaces and, if TURN servers are configured, relayed candidates (type relay). All gathered candidates are sent to the remote peer through the signaling channel. Both peers then perform connectivity checks by sending STUN Binding Requests to each other's candidates. The first pair that succeeds becomes the selected connection path.
Configuring Peer Connections
When building WebRTC applications with frameworks like React, React Native, Flutter, Android, or iOS, you configure ICE servers when creating the peer connection object. The configuration includes a list of STUN and TURN URLs. For Google STUN, you add the stun: protocol URL with the Google hostname and port 19302. Most SDKs accept this as a simple array of URL strings. VideoSDK's video calling SDK abstracts this configuration entirely, so developers do not need to manually specify ICE servers. The platform automatically selects optimal STUN and TURN servers based on the participant's network conditions and geographic location.
Best-Practice Settings
Always include at least two STUN servers from different providers to maximize candidate diversity. Use UDP as the primary transport since STUN over UDP has lower latency. Configure a TURN server as a fallback for symmetric NAT scenarios. Monitor ICE connection state changes in your application to detect when STUN-discovered paths fail and TURN relay kicks in.
Troubleshooting Common Issues
Even with Google STUN configured correctly, WebRTC connectivity problems are common. Most issues fall into three categories: no candidates gathered, high latency or timeouts, and NAT type incompatibility. Understanding each failure mode helps you diagnose and fix problems faster.
No Candidates or Empty ICE
If your WebRTC client gathers no server reflexive candidates, the most likely cause is a firewall or network policy blocking UDP traffic to port 19302. Corporate networks and some mobile carriers restrict outbound UDP traffic entirely. To diagnose this, check whether the browser's ICE gathering produces only host candidates and no srflx candidates. If so, UDP is being blocked. The solution is to configure a TURN server that supports TCP or TLS as a transport fallback. VideoSDK's infrastructure includes TURN server support with automatic fallback, so connectivity is maintained even when UDP is blocked.
High Latency or Timeouts
STUN requests should complete in under 100 milliseconds. If you observe timeouts or high latency, the issue is usually DNS resolution or network routing. Google STUN servers use anycast routing, so DNS resolution directs you to the nearest Google edge. If your DNS resolver is slow or returns a suboptimal Google edge location, latency increases. Switching to a faster DNS resolver like Google's own 8.8.8.8 or Cloudflare's 1.1.1.1 can help. Network congestion between the client and the Google edge can also cause timeouts. Running ICE gathering diagnostics tools available in browser developer tools helps pinpoint whether the delay is in DNS, connection, or response processing.
Mismatched NAT Types
The most insidious WebRTC connectivity problem is symmetric NAT. When one peer is behind a symmetric NAT, the public port discovered by Google STUN is only valid for communication with the STUN server, not with the remote peer. Direct connection attempts fail silently. The ICE framework detects this during connectivity checks and falls back to relayed candidates if a TURN server is configured. Without a TURN server, the call fails entirely. This is why every production WebRTC deployment needs a TURN server alongside Google STUN. According to WebRTC statistics gathered by webrtcstats.com, approximately 15-20% of peer-to-peer connections require TURN relay in real-world deployments.
Security and Privacy Considerations
Using Google STUN servers introduces security and privacy considerations that developers should understand before shipping to production.
Data Exposure Risks
When a WebRTC client contacts a STUN server, it reveals its public IP address to that server. With Google STUN, Google's infrastructure logs this interaction. While Google does not publicly document how long STUN request logs are retained, the exposure of a user's public IP is inherent to the STUN protocol. Additionally, WebRTC exposes local IP addresses through host candidates, which can reveal internal network topology. For applications where user privacy is critical, such as telehealth or legal consultations, consider using VPN-friendly STUN configurations or managed RTC platforms like VideoSDK that provide E2E encryption and controlled infrastructure.
Rate-Limiting and Abuse Prevention
Google imposes rate limits on its public STUN servers to prevent abuse. While Google does not publish exact limits, sending excessive STUN requests from a single IP address can result in throttled responses or temporary blocks. This is rarely an issue for normal WebRTC usage, where each client sends a handful of STUN requests during ICE gathering. However, applications that create many peer connections rapidly or run automated testing at scale may hit these limits. For production workloads, consider running your own STUN server or using a managed RTC provider. VideoSDK's REST APIs and SDK infrastructure handle STUN and TURN provisioning without rate-limit concerns.
Alternatives to Google STUN
Google STUN is not the only option. Depending on your use case, you may need alternatives that offer better guarantees, geographic coverage, or privacy controls.
When to Use TURN Instead
A TURN server relays media traffic between peers when direct peer-to-peer connection fails. This happens with symmetric NAT, restrictive corporate firewalls, or when UDP is blocked entirely. TURN servers require authentication and consume significant bandwidth since all media flows through the relay. You should always configure TURN alongside STUN, not instead of it. STUN handles the majority of connections efficiently, and TURN covers the remaining cases. VideoSDK includes managed TURN servers as part of its audio and video calling platform, so developers get both STUN and TURN without manual configuration.
Other Public STUN Providers
Several organizations offer public STUN servers as alternatives to Google. Cloudflare operates STUN servers through its Calls infrastructure. OpenRelay provides free STUN and TURN servers for development. Twilio offers STUN as part of its NAT traversal service. Some developers self-host STUN using open-source implementations like coturn, which gives full control over logging, rate limits, and geographic placement. For production applications, self-hosting or using a managed provider is preferable to relying on any single public STUN server. VideoSDK's code samples demonstrate how the platform handles ICE server configuration across React, Flutter, Android, iOS, and other SDKs without requiring manual STUN setup.
Performance and Reliability Checklist
Before shipping a WebRTC application that depends on Google STUN, verify the following:
- Confirm that UDP port 19302 is reachable from your target network environments, including corporate and mobile networks.
- Test STUN response latency from multiple geographic regions using browser ICE gathering diagnostics.
- Configure at least one TURN server as a fallback for symmetric NAT and UDP-blocked scenarios.
- Include two STUN servers from different providers to maximize candidate diversity and reduce single-provider dependency.
- Monitor ICE connection state transitions in production to detect when STUN-discovered paths fail and TURN relay activates.
- Set up alerting for ICE failure rates exceeding 5% of total connection attempts, which indicates network-level issues.
- Consider migrating to a managed RTC platform like VideoSDK if you find yourself spending significant time on STUN and TURN configuration and troubleshooting.
Definitions Glossary
STUN Server: A network service that helps devices behind NAT discover their public IP address and port by responding to Binding Requests as defined in RFC 5389.
ICE (Interactive Connectivity Establishment): A WebRTC framework that gathers connection candidates from multiple sources (host, STUN, TURN) and tests them to find the best working path between two peers.
Server Reflexive Candidate (srflx): A network address discovered by a STUN server that represents the client's public IP and port as seen from the internet.
TURN Server: A relay server that forwards media traffic between WebRTC peers when direct peer-to-peer connection fails due to restrictive NAT or firewall rules.
Symmetric NAT: A NAT type where the router assigns a different public port for each destination, making STUN-discovered addresses invalid for direct peer connections.
NAT Traversal: The process of establishing connections between devices behind NAT routers, typically using STUN, TURN, or ICE frameworks.
Key Takeaways
- Google STUN servers (stun.l.google.com:19302 through stun4.l.google.com:19302) are the most widely used public STUN endpoints for WebRTC development because they are free, globally distributed, and require no authentication.
- STUN servers discover public IP addresses but cannot solve symmetric NAT problems, which require a TURN server fallback for reliable connectivity.
- Always configure at least two STUN servers from different providers and one TURN server to maximize connection success rates across diverse network conditions.
- Corporate firewalls and mobile carriers frequently block UDP traffic, so testing STUN reachability across real-world networks is essential before production launch.
- VideoSDK's real-time communication platform handles STUN and TURN configuration automatically across React, Flutter, Android, iOS, and other SDKs, eliminating manual ICE server management for production deployments.
Conclusion
Google STUN servers remain the default starting point for WebRTC NAT traversal in 2026, and for good reason. They are free, fast, and backed by Google's global infrastructure. But they are not a complete solution. Production applications need TURN fallback for symmetric NAT scenarios, rate-limit awareness for high-volume deployments, and privacy considerations for sensitive use cases. If you are tired of manually configuring ICE servers and debugging connectivity issues, VideoSDK handles all of this for you with managed STUN and TURN infrastructure, network-adaptive streaming, and SDKs for every major platform. You can start building for free with a VideoSDK account and ship a working video calling app without touching a single STUN URL. What are you building with WebRTC? Drop a comment below and let me know what kind of real-time communication use case you are working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ