


A server websocket is the endpoint of a persistent, bi-directional communication channel that begins as an HTTP request and is then upgraded to a long-lived TCP connection. It lets servers push data to clients instantly instead of waiting for polling requests. VideoSDK's real-time communication SDKs handle this entire layer for you, but understanding how a server websocket works helps you debug, secure, and scale any real-time system you build. This guide walks through the handshake, library selection, security, and production scaling step by step.
Real-time features have shifted from a nice-to-have to an expectation. Live dashboards, collaborative editors, multiplayer games, chat, and trading interfaces all depend on the server being able to reach the client the moment something changes. HTTP polling burns bandwidth and adds latency; a server websocket solves both by keeping a single open connection alive for the session's lifetime.
The catch is that a websocket server behaves very differently from a typical request-response backend. Connections stay open for hours, state lives in memory, and a single slow client can back up your buffers. This guide covers what a server websocket actually is, how to choose a library, how to secure and scale it, and where the protocol is heading in 2026.
What Is a Server WebSocket?
A server websocket is defined as the server-side endpoint of the WebSocket protocol, a standardized communication channel that starts as an ordinary HTTP request and is then upgraded to a persistent, full-duplex TCP connection. Once the upgrade completes, both the client and the server can send messages to each other at any time, without the overhead of repeated HTTP headers or new connections.
The WebSocket protocol works by keeping a single TCP connection open between client and server, framing messages with a lightweight header, and supporting both text and binary payloads. Unlike HTTP, where the client must initiate every exchange, the server can push data the instant it becomes available. That inversion is what makes websockets the backbone of real-time communication.
Core Concepts of the WebSocket Server Role
The server's job in a websocket exchange goes beyond receiving messages. It owns the connection lifecycle: accepting or rejecting upgrades, tracking which sockets belong to which users, routing messages between participants, and detecting dead connections. Because every open socket consumes a file descriptor and memory, a websocket server is fundamentally a stateful, long-running process, which changes how you deploy, monitor, and scale it compared to a stateless HTTP API.
How the Handshake Works
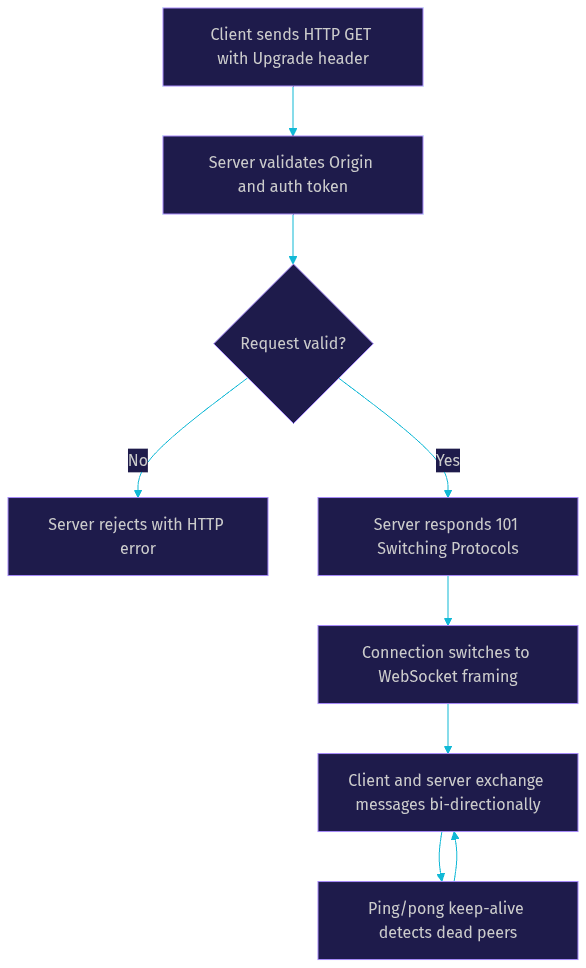
The WebSocket handshake works by piggybacking on HTTP. The client sends an HTTP GET request containing an Upgrade header requesting a protocol switch to WebSocket, along with a randomly generated security key. The server validates the request, computes a response token from that key, and replies with a 101 Switching Protocols status. From that point on, the connection is no longer HTTP; it speaks the WebSocket framing protocol.
During the handshake, the client can also propose one or more sub-protocols, such as a messaging schema or a versioned protocol name. The server picks the one it supports and echoes it back, or rejects the connection if none match. This negotiation matters in production because it lets you version your real-time API without breaking older clients.
Choosing the Right WebSocket Server Library
The library you pick shapes your concurrency model, memory footprint, and debugging experience more than almost any other decision. In practice, teams building real-time features consistently choose libraries with mature async support, because a websocket server is I/O-bound by nature: thousands of sockets are idle at any moment, and blocking any thread waiting on one of them wastes resources.
Language-Specific Options
For Node.js, the Socket.IO ecosystem and the lower-level ws library dominate. Socket.IO adds reconnection handling, rooms, and fallback transports on top of the raw protocol, which makes it a strong default for chat and collaboration apps. The ws library is leaner and faster when you want protocol-level control without extras.
For Python, the websockets library is the standard asyncio-native choice, with aiohttp offering websocket support as part of a broader async web framework. For Rust, Tokio-tungstenite delivers excellent throughput and predictable memory use, which matters at high connection counts. For Go, the gorilla/websocket package has long been the community standard, and the nhooyr/websocket library offers a more modern, context-aware API. Each of these handles the handshake, framing, and ping/pong mechanics so you can focus on your application's message routing.
Performance and Scalability Considerations
When comparing libraries, evaluate three factors against your workload. First, latency under load: how quickly a message sent by one client reaches another when thousands of connections are active. Second, throughput: how many messages per second the event loop can process before queues grow. Third, resource usage: memory per connection and CPU spent on framing and compression. A library that shines at 10,000 mostly idle connections may struggle with 500 connections streaming high-frequency binary data, so benchmark with a traffic pattern that matches yours.
Setting Up a Basic Server WebSocket
Setting up a server websocket involves four layers of decisions: where it runs, how it is secured, how connections are managed, and how it shuts down cleanly. Getting each layer right early prevents painful rework when you move from a laptop demo to production traffic.
Planning the Deployment Environment
Before writing any connection logic, decide where the websocket process lives. A dedicated process, separate from your HTTP API, is the common pattern because websocket servers have different scaling and memory profiles than request-response services. Choose a port, decide whether the process runs behind a reverse proxy or accepts traffic directly, and set up a process manager that restarts it on failure. Also plan for connection limits at the OS level, since each open socket consumes a file descriptor, and default operating system limits are often too low for real-time workloads.
Configuring TLS and Security
Every production websocket should run over TLS, which means the websocket secure scheme, wss, instead of plain ws. Obtain a certificate from a certificate authority such as Let's Encrypt, terminate TLS either at your reverse proxy or at the application process, and redirect any plain ws attempts to the secure endpoint. Browsers restrict mixed content, so a page served over HTTPS cannot open an insecure ws connection anyway, which makes TLS a hard requirement for any web-facing deployment.
Beyond encryption, validate the Origin header on every upgrade request. A websocket connection initiated from a malicious page can carry the victim's cookies, so rejecting upgrades whose origin is not on your allowlist is a first line of defense. Authentication tokens should be validated during the handshake, typically via a signed token in the query string or a header, so that no unauthenticated socket ever reaches your message handlers.
Managing Connections and Heartbeats
TCP connections can die silently when a network path drops, a laptop sleeps, or a mobile device switches networks. Without active detection, your server holds ghost connections that consume memory and skew your presence data. The standard fix is a heartbeat: the server periodically sends a ping frame, expects a pong frame back within a timeout window, and closes the connection if none arrives. Most libraries expose this as a configuration option rather than something you implement yourself.
Graceful shutdown is the other half of connection management. When deploying a new version, your process should stop accepting new upgrades, notify connected clients to reconnect, close sockets cleanly, and then exit. Pair that with client-side reconnection logic using exponential back-off, and deploys become invisible to your users.
Scaling Server WebSocket for Production
Scaling a websocket server is fundamentally different from scaling an HTTP API because connections are stateful. You cannot simply add replicas behind a round-robin load balancer and expect messages to reach the right clients, because a user's socket lives on exactly one server instance. Production scaling therefore has two parts: distributing connections across instances, and sharing message state between them.
Load Balancing Strategies
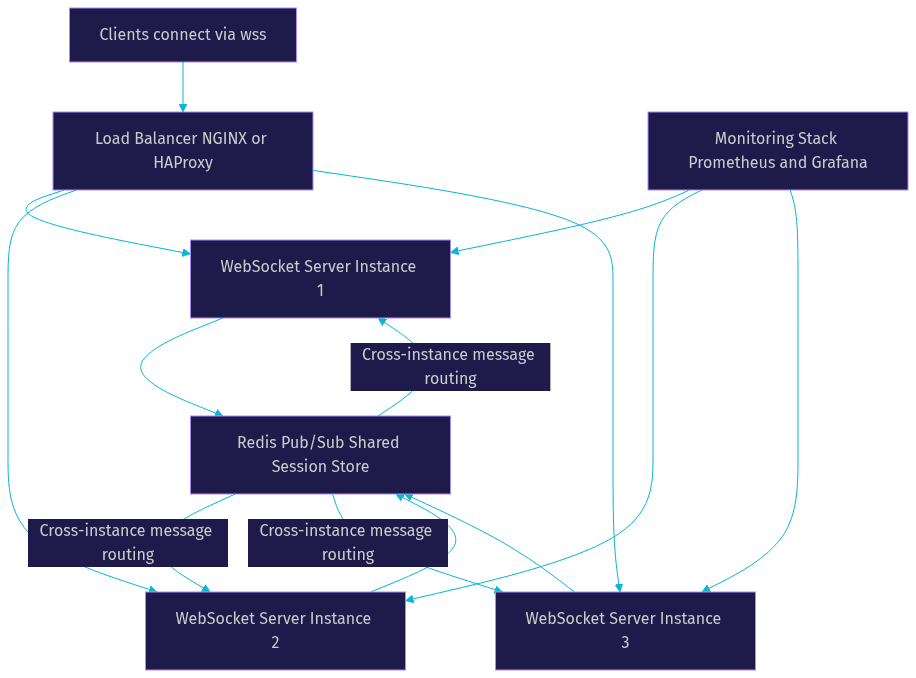
A reverse proxy such as NGINX or HAProxy sits in front of your websocket servers and distributes new connections. The critical configuration detail is the upgrade handling: the proxy must forward the HTTP Upgrade request correctly and, importantly, disable aggressive timeouts, because a proxy that closes idle connections after 60 seconds will silently kill your websockets. Set long read and send timeouts, or rely on your heartbeat traffic to keep the connection looking active.
Sticky sessions matter when your servers hold in-memory session state. With sticky routing, a reconnecting client lands back on the same instance that holds its context. If your architecture is fully stateless, stickiness becomes optional, but most teams start with it because it simplifies presence and in-flight message buffering.
Horizontal Scaling with Stateless Servers
The cleaner long-term architecture moves shared state out of the server process. Each websocket instance keeps only its local sockets, while a shared store such as Redis holds which users are connected where. When instance A needs to send a message to a user connected on instance B, it publishes to a Redis channel that B subscribes to, and B delivers it over the local socket. This pub-sub pattern decouples your application logic from the physical topology, letting you add or remove instances freely.
The trade-off is added latency for cross-instance messages and one more infrastructure component to operate. For most teams, that trade is worth it once they exceed a single instance's connection capacity, which typically lands in the tens of thousands of concurrent sockets per process depending on message frequency and payload size.
Monitoring and Metrics
A websocket server in production needs its own metric set, because generic HTTP dashboards will not reveal its failure modes. Track concurrent connection count and its growth trend, message rate in and out, handshake success and failure rates, ping/pong timeout counts, and send buffer sizes. Rising buffer sizes are your earliest warning that a client is not reading fast enough and back-pressure is building. Standard tooling works well here: expose metrics in Prometheus format and visualize them in Grafana, and alert on connection drops that exceed your reconnect rate, since that pattern usually indicates a network or proxy timeout rather than client churn.
Security Best Practices for Server WebSocket
WebSocket security deserves its own checklist because the protocol inherits some HTTP semantics during the handshake and then leaves them behind. The most common vulnerabilities are unauthorized upgrades, cross-site websocket hijacking, and resource exhaustion attacks.
Origin Checking and CSRF Protection
Cross-site websocket hijacking works like CSRF, but for websockets: a malicious page opens a websocket to your server using the victim's browser credentials, and your server, seeing a valid authenticated connection, happily exchanges data with the attacker's page. The defense is strict Origin validation on every upgrade request. Reject any request whose Origin header is not on your explicit allowlist, and combine that with token-based authentication validated at handshake time. Never rely on cookies alone to authorize a websocket, since the browser attaches them automatically regardless of which page initiated the connection.
Rate Limiting and DoS Mitigation
Because each connection costs memory and file descriptors, a websocket endpoint is a natural target for resource exhaustion. Apply per-IP connection caps at the load balancer or application layer, throttle message rates per connection, and cap maximum message size so a single client cannot send a frame that forces your server to allocate a huge buffer. Handle bursts by queuing and dropping rather than by allocating unbounded memory, and consider a challenge on handshake, such as requiring a short-lived signed token, to make scripted connection floods expensive for attackers.
Using permessage-deflate Compression Wisely
The WebSocket protocol supports per-message compression through the permessage-deflate extension, which shrinks text payloads substantially. The trade-off is CPU: compressing every message on a high-throughput server can consume more resources than it saves in bandwidth. Enable it for large, compressible text payloads such as JSON updates, and disable it for small or binary messages where the overhead outweighs the savings.
Common Pitfalls and How to Avoid Them
Even with a solid library, a few failure patterns account for most production websocket incidents. They all trace back to the same root cause: treating a stateful, long-lived connection like a stateless request.
Connection Drops and Reconnection Logic
Connections will drop, whether from mobile network switches, proxy timeouts, or deploys. The mistake is assuming the client will notice. A dead socket can sit in your server's connection table indefinitely without a heartbeat. On the server, enforce ping/pong timeouts and clean up all associated state when a socket closes. On the client, detect the drop, then reconnect with exponential back-off and jitter so that thousands of reconnecting clients do not synchronize into a thundering herd against your server. Design your protocol so a reconnecting client can resubscribe and catch up on missed messages, typically via a sequence number or last-event identifier.
Memory Leaks and Back-Pressure
Two memory problems plague websocket servers. The first is leaked per-connection state: user maps, subscription lists, and cached context that are added when a socket opens but never removed when it closes. Audit every data structure that grows with connections and confirm it shrinks on disconnect. The second is back-pressure: when a client on a slow network stops reading, the server's outbound buffer for that socket grows without limit. Use your library's built-in buffered-amount checks, pause sending to slow clients, and drop or disconnect clients whose buffers exceed a threshold. A server that respects back-pressure stays responsive for everyone; one that ignores it degrades globally.
Future Trends in Server WebSocket Technology
The WebSocket protocol is stable and deeply embedded, but the transport layer beneath it is evolving, and two developments are worth tracking as you plan your real-time architecture.
HTTP/3 and QUIC Impact
HTTP/3 runs over QUIC, a UDP-based transport with built-in encryption and faster connection establishment. WebSocket-over-QUIC, sometimes called WebSocket/3, reduces handshake latency and, more significantly, enables connection migration: when a device switches from Wi-Fi to cellular, the QUIC connection identifier can survive the network change, potentially eliminating the reconnect storms that plague mobile websocket clients today. Browser and server support is still maturing in 2026, but the direction is clear.
Real-Time Alternatives: WebTransport
WebTransport is an emerging API built directly on HTTP/3 that offers datagrams and multiple independent streams over a single connection, without the strict ordering constraints of a single websocket. For games, streaming media, and high-frequency data feeds, unordered datagrams can outperform a websocket that head-of-line blocks on one slow message. WebTransport will complement rather than replace WebSocket for years, since the latter remains simpler and universally supported, but teams building latency-critical systems should evaluate both.
If you would rather not own this entire stack, handshakes, heartbeats, scaling, and reconnection, a managed real-time communication platform such as VideoSDK handles the transport layer for you, with SDKs for React, Flutter, Android, iOS, and more, so you can focus on your application logic instead of connection plumbing.
Definitions Glossary
Server websocket: The server-side endpoint of the WebSocket protocol, responsible for accepting upgrades, tracking connections, routing messages, and detecting dead peers over a persistent, bi-directional channel.
WebSocket handshake: The HTTP exchange that begins a websocket session, in which the client requests a protocol upgrade and the server responds with a 101 Switching Protocols status before the connection switches to WebSocket framing.
Heartbeat (ping/pong): A keep-alive mechanism where the server sends ping control frames at intervals and closes connections that fail to answer with pong frames, used to detect silently dead sockets.
Back-pressure: The condition where a slow client cannot read data as fast as the server sends it, causing outbound buffers to grow, which must be managed through flow control or disconnection.
Sticky sessions: A load balancing configuration where a reconnecting client is routed back to the same server instance that holds its in-memory session state.
permessage-deflate: A WebSocket extension that compresses each message, trading CPU overhead for reduced bandwidth, best suited to large compressible text payloads.
Key Takeaways
- A server websocket is a stateful, long-lived endpoint that upgrades an HTTP connection into a persistent bi-directional channel, which changes how you deploy, monitor, and scale it compared to a stateless API.
- Secure every production websocket with TLS, strict Origin validation, handshake-time authentication, per-IP connection caps, and message size limits.
- Scale horizontally by moving shared session state into a pub/sub store such as Redis, so any instance can route messages to any connected user.
- Heartbeats, graceful shutdown, client-side exponential back-off reconnection, and back-pressure handling are the difference between a demo and a production-grade websocket server.
- Emerging transports such as QUIC-based WebSocket and WebTransport will reduce latency and improve mobile resilience, but WebSocket remains the universal standard for real-time communication in 2026.
Conclusion
A well-run server websocket is the difference between an app that feels instant and one that feels broken under real network conditions. The protocol itself is simple; the engineering effort lives in the operational layer: TLS and origin checks at the handshake, heartbeats and reconnection logic at the connection layer, and Redis-backed pub/sub with load balancing at the scale layer. Audit your current setup against the checklist here, from buffer limits to proxy timeouts, and fix the gaps before your users find them. If you would rather skip the plumbing entirely, explore VideoSDK's real-time communication SDKs or browse the code samples to ship real-time features in minutes. What are you building with websockets? Drop a comment, I'd love to hear what kind of real-time use case you're working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ