


A STUN server for VoIP is a lightweight discovery service that lets a phone or browser behind a NAT firewall learn its own public IP address and port so that voice media can flow directly between callers. STUN alone works for most network types, but symmetric NATs require a TURN relay fallback. VideoSDK handles this entire layer automatically, provisioning STUN and TURN infrastructure so your WebRTC or SIP-based calling app connects on any network.
Every VoIP developer hits the same wall eventually: the call signs up perfectly, then the audio never arrives. The culprit is almost always NAT traversal, and the first tool in the fix is a STUN server. If you are building SIP softphones, WebRTC calling apps, or hybrid VoIP platforms in 2026, understanding how a STUN server for VoIP works is non-negotiable.
NAT traversal is the process of getting two-way media through routers that hide private IP addresses behind a single public one. ICE, the Interactive Connectivity Establishment framework, is the negotiation strategy that tries every possible connection path and picks the one that works. STUN is the discovery mechanism inside that strategy. This article walks through the protocol, the best free and enterprise STUN options, how to wire STUN into SIP clients and WebRTC apps, and how to self-host your own server with coturn.
How STUN Works in VoIP
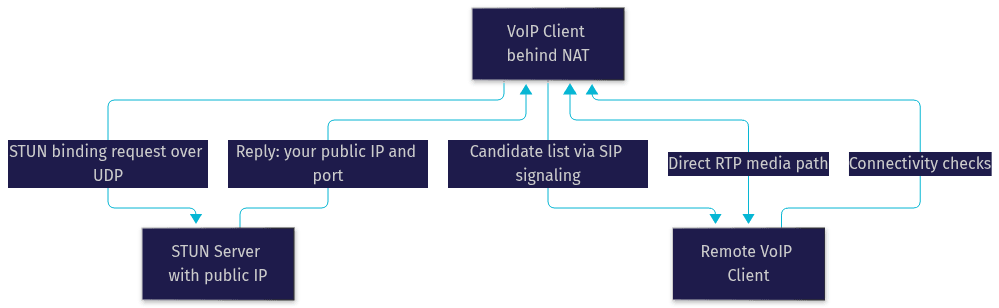
STUN, which stands for Session Traversal Utilities for NAT, is a simple request-response protocol that answers one question: what does my device look like from the outside? A VoIP client sends a STUN binding request to a public server, and the server replies with the public IP address and port it observed. That reply is the client's external network identity.
That discovery matters because SIP and WebRTC signaling carries IP addresses inside the call setup messages. A softphone sitting on a private network like 192.168.x.x cannot just advertise that address to the outside world, because remote parties cannot route to it. By learning its public reflexive address through STUN, the client can include a reachable candidate in its session description.
In a full ICE negotiation, the client gathers multiple candidates: the local private address, the STUN-discovered public address, and optionally a TURN-relayed address. Both sides of the call then exchange candidates through signaling and test connectivity pairwise. The best working pair, usually the direct STUN-assisted path, becomes the media route. STUN never carries voice traffic itself; it only enables discovery, which keeps it extremely cheap to run.
One limitation deserves emphasis: STUN fails on symmetric NATs, where the router assigns a different external port for every destination. The STUN-discovered address works only toward the STUN server itself, not toward the remote caller. That is why production VoIP stacks always pair STUN with a TURN relay as a fallback.
Choosing the Right STUN Server for VoIP
Picking a STUN server for VoIP comes down to four criteria: latency, reliability, geographic proximity, and protocol support. STUN responses are tiny, but the round trip still adds to call setup time, so a server within 50 to 100 milliseconds of your users keeps ICE gathering fast. Reliability matters more than speed, because a dead STUN server silently degrades call setup into longer fallback paths.
Public STUN servers are fine for development and small deployments. For production, most teams either self-host coturn or use a managed infrastructure provider, because public servers carry no uptime guarantees and some throttle heavy use. Protocol support is the other dividing line: most public servers answer over UDP only, while enterprise or self-hosted deployments can also listen on TCP and TLS, which matters for users behind corporate firewalls that block UDP.
Popular Free STUN Servers
The most widely used free options in 2026 include Google's public STUN endpoints such as stun.l.google.com on port 19302 and its numbered regional variants, plus community servers like stun.voipbuster.com and others maintained by VoIP providers. Google's servers are fast, globally distributed, and battle-tested by millions of Chrome WebRTC sessions, which makes them the default choice for prototyping.
The trade-offs are real. Public servers offer no service-level agreement, no visibility into outages, and no guarantee against rate limiting. Community-run servers can disappear without notice. Use them to validate your ICE configuration, then move to something you control before shipping to customers.
Enterprise-Grade STUN Options
When you need guarantees, three paths dominate. Managed WebRTC infrastructure providers such as Twilio and Xirsys sell STUN and TURN as a service with global coverage, monitoring, and TLS support. Self-hosting coturn on your own cloud VM gives you full control at the cost of operational effort. And platforms like VideoSDK bundle STUN, TURN, and the entire media routing layer into their video and audio calling SDKs, so the traversal problem disappears entirely from your application code.
Paid or managed options earn their keep when you support enterprise users behind strict firewalls, need TCP and TLS traversal, or require logging and analytics on connection failures. For a consumer app with mostly residential users, a well-placed self-hosted STUN server plus a TURN fallback is often enough.
Integrating STUN with SIP Clients
SIP softphones use STUN during registration and during each call's media negotiation. When a SIP client registers with a proxy, it embeds contact and media addresses in the REGISTER and INVITE messages. With STUN enabled, the client first discovers its public address and writes that into the messages instead of its private LAN address, so the proxy and remote endpoints can actually reach it.
In popular clients like Zoiper, Linphone, and MicroSIP, the setup intent is the same even though the menus differ. You open the network or NAT traversal settings, enable STUN, and enter the hostname and port of your chosen server. Linphone exposes this under its network configuration with a NAT traversal section; Zoiper places it in the advanced network settings with a STUN server field; MicroSIP keeps it in the network tab of its preferences. After saving, restart the client so it re-runs discovery, then verify that registration succeeds and that the reported external address matches your router's public IP.
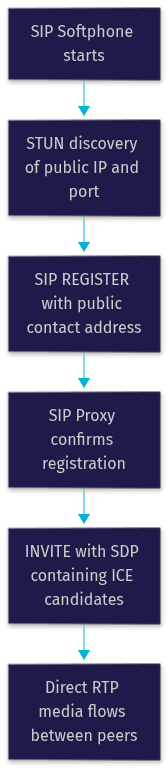
A common failure pattern: the phone registers fine but audio is one-way or silent. That usually means the SDP carried a private address, either because STUN was disabled or because the client ignored the discovery result. Re-check that STUN is enabled before registration, not just before calls, since some clients only gather candidates at startup.
Using STUN in WebRTC-Based VoIP Applications
WebRTC applications configure STUN through the ICE servers list that the browser runtime consumes when a peer connection is created. Conceptually, you provide a list of server entries, each with a type, a hostname, and a port, and the browser gathers a STUN candidate from every entry before signaling begins. Libraries like SIP.js over WebRTC, JsSIP, and the raw peer connection API all follow this same model.
The most common pitfall is default override. Many tutorials and SDKs ship with Google's public STUN server preconfigured, and developers who add their own server entry sometimes end up with both, or worse, the SDK silently keeps the default. If your production traffic should hit your own infrastructure, verify that the final ICE configuration contains only your intended servers. Another pitfall is omitting TURN entirely: roughly 10 to 20 percent of real-world users sit behind symmetric NATs or strict corporate firewalls where STUN alone cannot complete the connection, and without a TURN relay those users get dead air.
If you would rather not manage any of this, VideoSDK's video and audio calling SDKs abstract the entire ICE layer. The SDK's cloud handles STUN discovery, TURN fallback, and network-adaptive streaming automatically, so your application code never touches server lists at all.
Deploying Your Own STUN Server with Coturn
Coturn is the open-source reference implementation for STUN and TURN, and it is what most production VoIP teams self-host. The deployment narrative is straightforward whether you install it from a Linux package or run it as a Docker container on a cloud VM with a public IP address.
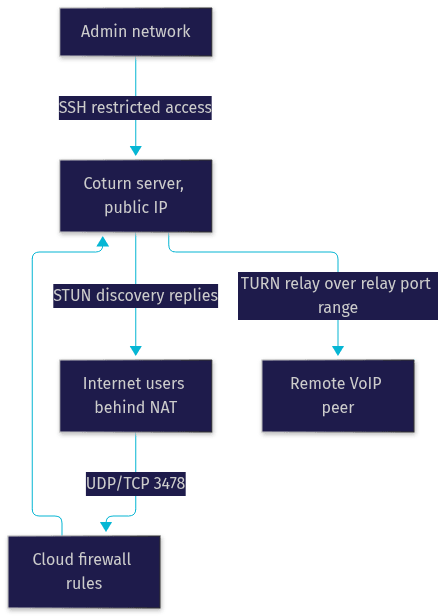
The setup intent breaks into four decisions. First, choose the listening ports: the standard STUN and TURN port is 3478 for both UDP and TCP, with TLS typically on 5349. Second, define the realm, which is essentially your authentication domain label. Third, configure authentication: for STUN-only usage you can run open, but for TURN you set a static shared secret so that time-limited credentials can be generated and validated. Fourth, open the relay port range on the firewall, typically a few thousand UDP ports that TURN allocates dynamically for relayed media.
Security hardening follows. Restrict the relay address range to your server's public IP, disable the legacy long-term credential mechanism in favor of the shared-secret model, run the daemon under an unprivileged user, and put monitoring on the listening ports. On the firewall side, allow UDP and TCP on 3478, TLS on 5349, and the relay range, while blocking administrative interfaces from the public internet.
Self-hosting earns its cost when you need predictable latency, full logs, and no dependency on third-party uptime. The price is that you now own monitoring, capacity planning, and failover, which is exactly why many teams instead choose a managed SDK like VideoSDK where traversal infrastructure is part of the platform.
Testing and Monitoring STUN Performance
Verification starts with confirming what your network actually looks like from outside. Command-line STUN clients can query a server and report your discovered public address and NAT type, which tells you immediately whether direct media is feasible or whether TURN will be required. In browser-based apps, the chrome://webrtc-internals page exposes every ICE candidate gathered, the selected candidate pair, and the round-trip times of connectivity checks.
Interpreting results for VoIP call quality means watching two numbers. STUN response latency under 100 milliseconds keeps call setup snappy; anything consistently higher suggests a geographically poor server choice. The selected candidate pair tells you the media path: a direct host or server-reflexive pair means good quality with minimal latency, while a relayed pair means TURN is in use and you should expect slightly higher latency and bandwidth costs.
Best Practices and Troubleshooting
A short checklist solves most STUN-related VoIP failures. Confirm the STUN port, usually 3478 or 19302, is reachable from your network. Verify that firewall rules allow UDP outbound and, for self-hosted coturn, that the relay port range is open. Ensure TURN and STUN credentials match what your credential generator produces, since a mismatch fails silently during gathering. Check that your client is not still using a default Google STUN entry alongside your custom server. And confirm IPv6 compatibility if your users are on dual-stack networks, because a server reachable only over IPv4 will fail for IPv6-only clients.
Quick fixes for common symptoms: one-way audio usually means the SDP carried a private address, so re-enable STUN before registration. Calls failing only for office users points to symmetric NAT, so add TURN. Registration succeeding but calls dropping points to a STUN server outage, so monitor your server and keep a backup entry in the ICE list.
Definitions Glossary
STUN: Session Traversal Utilities for NAT, a protocol that lets a client discover its public IP address and port as seen by an external server, enabling direct VoIP media paths.
TURN: Traversal Using Relays around NAT, a protocol that relays media through a server when direct connection fails, essential for symmetric NATs and strict firewalls.
ICE: Interactive Connectivity Establishment, the framework that gathers STUN and TURN candidates and tests each pair to select the best working media route.
NAT traversal: The process of establishing two-way communication between devices behind NAT routers that hide private IP addresses behind a shared public one.
Coturn: The open-source STUN and TURN server implementation most teams self-host for production VoIP and WebRTC deployments.
Key Takeaways
- A STUN server for VoIP enables NAT traversal by telling clients their public address, allowing direct media flow without relaying every packet.
- STUN alone fails on symmetric NATs, so production systems always pair it with a TURN relay fallback.
- Free public servers like Google's are excellent for development but carry no uptime guarantees for production traffic.
- Self-hosting coturn gives full control over ports, authentication, and latency, at the cost of ongoing operations.
- VideoSDK's video and audio calling SDKs handle STUN, TURN, and network-adaptive streaming automatically, removing the traversal layer from your application entirely.
Conclusion
Choosing the right STUN server for VoIP is a small decision with outsized impact on call setup speed and audio reliability. Start with public servers to validate your ICE configuration, test multiple servers for latency from your users' regions, and move to self-hosted coturn or managed infrastructure before production. If you would rather skip NAT traversal engineering altogether, VideoSDK's calling SDKs handle the entire traversal and media layer for you, with a free tier to get started at app.videosdk.live. What are you building with VoIP or WebRTC? Drop a comment, I'd love to hear what kind of calling use case you're working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ