


TCP is a transport-layer protocol that reliably moves bytes between two endpoints, while HTTP is an application-layer protocol that adds request-response structure, headers, and semantics on top of TCP. Use raw TCP when you need minimal overhead and full control over persistent, stateful streams; use HTTP when you need interoperability, caching, security tooling, and firewall friendliness. Most modern systems combine both, and real-time platforms like VideoSDK layer their media and signaling on top of these fundamentals.
A raw TCP socket can deliver a message between two servers in well under a millisecond, yet the same message sent over HTTP can take several times longer, simply because of connection setup and header overhead. That gap surprises many developers who assume HTTP is just "TCP with a label." It is not. HTTP adds an entire framing, routing, and semantics layer, and that layer costs latency, bytes, and complexity in both directions.
The "TCP vs HTTP" question comes up whenever you are designing an API, a data pipeline, a game server, an IoT fleet, or a real-time communication system. The honest answer is that neither protocol wins universally. TCP wins on overhead and control; HTTP wins on interoperability and ecosystem. This article breaks down how each protocol works, where each one performs better, how security and firewalls differ, and gives you a decision framework you can apply to your own architecture today.
What Is TCP?
TCP, or Transmission Control Protocol, is defined as a connection-oriented transport-layer protocol that guarantees ordered, reliable delivery of a byte stream between two endpoints. It works by establishing a connection through a three-way handshake, then sequencing every byte, acknowledging receipt, retransmitting losses, and dynamically adjusting send rates through flow control and congestion control algorithms.
TCP gives you three core guarantees: reliability (nothing is silently lost), ordering (bytes arrive in the sequence they were sent), and congestion awareness (the sender backs off when the network is saturated). What TCP does not give you is meaning. A TCP connection is just a pipe of bytes. Any structure, framing, or message boundaries are entirely your responsibility as the developer.
What Is HTTP?
HTTP, or Hypertext Transfer Protocol, is defined as an application-layer request-response protocol that runs on top of TCP and adds structured semantics to the byte stream. It works by framing each exchange into a request (method, path, headers, optional body) and a response (status code, headers, body), which lets both sides interpret the conversation without custom parsing rules.
HTTP brings capabilities TCP lacks: standardized headers for content negotiation, status codes for error handling, caching directives, authentication schemes, and compression. With HTTP/2 and HTTP/3, the protocol has also gained multiplexing and, in HTTP/3's case, a shift to QUIC over UDP underneath. Every browser, CDN, API gateway, and load balancer on the internet speaks HTTP fluently, which is precisely why it dominates public-facing services.
TCP vs HTTP: Performance Perspective
Performance is where the TCP vs HTTP comparison gets concrete, because HTTP's flexibility is paid for in bytes and round trips. Every HTTP request carries a request line plus a set of text headers, and every response carries status and header metadata before the actual payload. On a small API call, headers can easily exceed the payload itself. A raw TCP exchange carries only a 20-byte header per segment (plus IP), with no application framing unless you add your own.
Connection setup compounds the difference. TCP requires one round trip for the three-way handshake before any data flows. HTTP historically added more: each request needed its own connection, meaning a fresh handshake plus a slow-start ramp-up per exchange. Persistent connections and HTTP/2 multiplexing have narrowed this gap dramatically, but the handshake and header costs never disappear entirely. For short, bursty, high-frequency messages, such as telemetry pings or order-book updates, HTTP overhead vs raw TCP can be the difference between meeting a latency budget and missing it.
The diagram below shows how the two exchanges differ in structure:
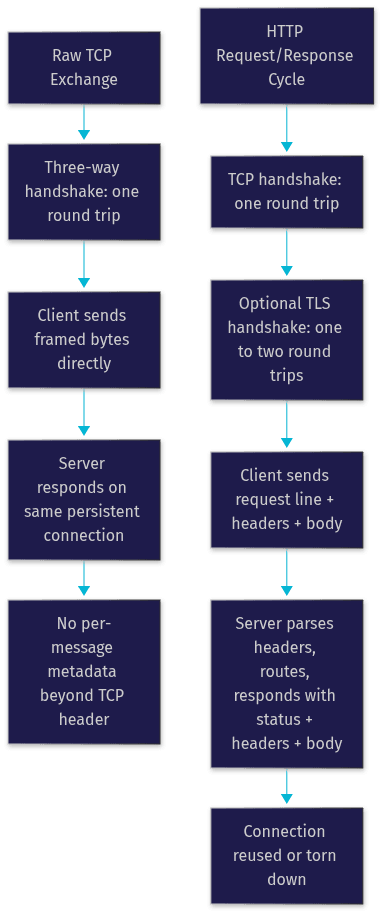
Raw TCP Exchange
In a raw TCP exchange, the client opens a connection once and then pushes bytes continuously. There is no request line, no headers, no status code. The developer defines the framing: a length prefix, a delimiter, or a fixed record size. Because the connection stays open, there is no per-message handshake cost, and congestion control state (the window size) stays warm, so throughput ramps quickly. The trade-off is that both ends must agree on the framing scheme and handle partial reads, reassembly, and malformed input themselves.
HTTP Request/Response Cycle
An HTTP exchange begins with the same TCP handshake, optionally followed by a TLS handshake. Then the client sends a request line, a block of headers, and possibly a body. The server parses all of that, applies routing and middleware, and returns a status line, response headers, and the payload. Each of those steps adds parsing cost and bytes on the wire. Persistent connections and multiplexing amortize the handshake across many requests, but the per-request header and framing overhead remains, which is why HTTP latency vs TCP latency still favors raw sockets for tiny, frequent messages.
When to Choose TCP Over HTTP
Raw TCP wins when overhead and control matter more than interoperability. The clearest cases are high-frequency binary streams: market data feeds, multiplayer game state, sensor telemetry from IoT fleets, and internal microservice data pipelines. These workloads send small messages thousands of times per second, where HTTP header overhead would multiply bandwidth and parsing costs for zero benefit.
TCP is also the right call when you control both endpoints and can define a custom binary protocol. A compact binary protocol over TCP routinely beats an equivalent REST interface by an order of magnitude in message size, and it eliminates JSON serialization cost entirely. Low-latency trading systems, for example, keep connections open for days and exchange fixed-size binary records with no framing negotiation.
Persistent, stateful streams are the third category. Live audio and video, large file transfer, and remote desktop sessions all want a long-lived, ordered byte channel rather than a request-response loop. Notably, real-time communication platforms build on exactly this insight: VideoSDK's real-time communication architecture maintains persistent connections for media transport and signaling, because per-request HTTP semantics would make sub-second interactive latency impossible.
Finally, choose TCP when your deployment environment permits it: internal networks, cloud VPCs, or data centers where firewall rules allow custom ports and you own both ends of the wire.
When HTTP Is the Better Choice
HTTP wins whenever the outside world is involved. Browsers only speak HTTP. Third-party SaaS APIs, webhooks, payment gateways, and OAuth providers all expose HTTP interfaces. If your service must be consumed by anything you do not control, HTTP is not just the better choice, it is often the only choice.
HTTP also ships with features you would otherwise rebuild yourself: caching directives that CDNs honor natively, content-type negotiation, standardized authentication headers, compression, and TLS termination at any load balancer. A public API over HTTPS gets encryption, rate limiting, and observability tooling almost for free, whereas a custom TCP protocol needs each of those engineered from scratch.
Firewall friendliness is a decisive practical factor. Ports 80 and 443 are open essentially everywhere: corporate networks, hotel Wi-Fi, mobile carriers, and restrictive national networks. A custom TCP protocol on port 9000 will be blocked by the first firewall it meets. This is why even systems that need persistent connections often tunnel over HTTPS, and why VideoSDK's cloud infrastructure includes fallback paths designed for restrictive networks.
Debugging and tooling tip the scales further. Every language has mature HTTP client libraries, every proxy can inspect HTTP traffic, and every observability platform understands status codes and request tracing. Raw sockets require custom logging, custom protocol analyzers, and custom versioning strategies.
Security Considerations
TCP provides no built-in encryption or authentication. If you run a raw TCP protocol, you must layer TLS on manually, manage certificates on both ends, and handle renegotiation and key rotation yourself. Many teams skip this step on internal networks, which works until an attacker lands inside the perimeter.
HTTP, by contrast, has the most battle-tested security stack on the internet. HTTPS wraps the entire exchange in TLS, and every framework, load balancer, and CDN handles certificate management for you. The trade-off is a different attack surface: HTTP exposes header injection, request smuggling, and cross-site risks that raw sockets do not have, but these are well-documented with mature mitigations.
In the TCP vs HTTP security comparison, the practical verdict is that HTTPS gives you strong security with near-zero engineering effort, while raw TCP gives you the same theoretical strength only if you invest the work to add and maintain TLS yourself.
Development and Maintenance Overhead
Raw TCP shifts the burden onto you. You must design message framing, handle partial reads and reassembly, implement heartbeats and dead-connection detection, version your protocol, and write custom tooling to debug it. Every new client language means reimplementing the parser. This is manageable for a small internal protocol, and it becomes a real tax as the team and the client surface grow.
HTTP hands you a standardized contract. Status codes communicate outcomes, content types describe payloads, and client libraries exist for every platform on earth. Versioning, pagination, and error semantics all have established conventions. For most teams, the development speed of HTTP outweighs the runtime efficiency of TCP, which is exactly why REST dominates public APIs even where a binary protocol vs REST comparison would favor the binary side on raw performance.
Real-World Case Studies
A high-frequency trading platform illustrates the TCP extreme. Matching engines and market data feeds use long-lived TCP connections carrying fixed-format binary records, with kernel-level tuning to shave microseconds. HTTP would be disqualified on handshake cost and header size alone; the latency budget is measured in microseconds.
A large-scale public web service illustrates the HTTP extreme. A SaaS company exposing a REST API to thousands of external developers needs caching, rate limiting, OAuth, documentation, and CDN compatibility. Nobody consuming that API wants to integrate a custom socket protocol, and the per-request overhead of HTTP is irrelevant at human-scale interaction frequency.
The most common real-world pattern is the hybrid. A video conferencing platform, for instance, uses persistent connections for real-time media and signaling, while exposing billing, room management, and analytics through ordinary HTTPS REST APIs. VideoSDK's own architecture follows this model: REST APIs for room management and recording handle control-plane operations, while the data plane runs over persistent real-time channels. The lesson is that TCP vs HTTP is rarely an either-or decision at the system level; it is a per-workload decision.
Decision Framework
Use this quick-reference table to map your workload to the right protocol:
| Criterion | TCP-Favored | HTTP-Favored | Hybrid |
|---|---|---|---|
| Latency sensitivity | Sub-millisecond, high frequency | Human-scale requests | Control plane HTTP, data plane TCP |
| Data format | Compact binary records | JSON, HTML, files | Binary streams + JSON metadata |
| Consumers | You own both ends | Browsers, third parties, public APIs | Internal TCP, external HTTP |
| Firewall environment | Internal network or VPC | Any public network | HTTPS tunneling for restricted paths |
| Security effort | Manual TLS, custom auth | HTTPS, OAuth, mature libraries | TLS everywhere, HTTP auth externally |
| Development speed | Slow: custom framing and tooling | Fast: standard libraries and tooling | Moderate |
| Statefulness | Long-lived, stateful sessions | Stateless request-response | Both, per workload |
The most important row is firewall environment. A technically superior TCP protocol that cannot traverse your users' networks is a failed design, which is why hybrid architectures that lead with HTTPS and reserve raw TCP for controlled internal paths have become the default for distributed systems in 2026.
Definitions Glossary
TCP (Transmission Control Protocol): A connection-oriented transport-layer protocol that guarantees ordered, reliable byte delivery between two endpoints using handshakes, acknowledgments, and congestion control.
HTTP (Hypertext Transfer Protocol): An application-layer request-response protocol built on top of TCP that adds structured semantics such as headers, status codes, and content negotiation.
Three-way handshake: The TCP connection setup process in which client and server exchange synchronization and acknowledgment messages, costing one round trip before any payload data flows.
TLS (Transport Layer Security): The cryptographic protocol that encrypts data in transit; required manually on raw TCP but standard and automated in HTTPS.
Protocol framing: The scheme a developer defines for a raw TCP stream to mark message boundaries, such as length prefixes or delimiters, since TCP itself treats the connection as an unstructured byte pipe.
QUIC: The UDP-based transport protocol that underpins HTTP/3, reducing connection setup latency compared to TCP plus TLS.
Key Takeaways
- TCP is a transport-layer byte stream; HTTP is an application-layer protocol that adds structure, semantics, and overhead on top of TCP.
- Choose raw TCP for high-frequency binary streams, persistent stateful sessions, and environments where you control both endpoints and the network path.
- Choose HTTP for anything consumed by browsers, third parties, or public networks, where interoperability, caching, HTTPS, and firewall traversal matter more than raw efficiency.
- HTTPS delivers strong security with minimal engineering effort, while raw TCP requires you to add and maintain TLS yourself.
- The most robust modern architectures are hybrid: persistent real-time channels for the data plane and HTTP REST APIs for the control plane, the same pattern VideoSDK uses for its real-time communication platform.
Conclusion
The TCP vs HTTP question has no blanket answer, and any article claiming one protocol universally wins is misleading. TCP wins on overhead, latency, and control for workloads you fully own. HTTP wins on interoperability, security tooling, and network traversal for everything that touches the outside world. The strongest systems use both deliberately, matching each workload to the protocol that fits its constraints. Evaluate your own use case against the decision framework above, and if you are building real-time communication features, explore how VideoSDK handles persistent connections and signaling so you get TCP-class latency without building the protocol layer yourself. What are you building? Drop a comment, I'd love to hear which side of the TCP vs HTTP divide your workload lands on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ