


The Sec-WebSocket-Key is a required HTTP header in the opening WebSocket handshake that carries a base64-encoded 16-byte random nonce generated by the client. The server uses this nonce, concatenates it with a fixed GUID defined in RFC 6455, computes a SHA-1 hash, and returns the base64-encoded result as the Sec-WebSocket-Accept header. This round-trip proves the server understands the WebSocket protocol and prevents accidental upgrades from misconfigured HTTP endpoints. VideoSDK leverages this same handshake foundation when establishing real-time communication sessions over WebRTC and WebSocket transport layers.
Most developers never think about the Sec-WebSocket-Key header until something breaks. You fire up a WebSocket connection, the browser throws a generic error, and the network tab shows a failed upgrade request with no obvious explanation. The culprit is often a missing or malformed header in the handshake that bridges HTTP and WebSocket protocols.
Understanding this header matters because it sits at the boundary between two fundamentally different communication models. If you are building real-time applications with VideoSDK's JavaScript SDK or any WebSocket-based infrastructure, knowing how the handshake works under the hood helps you debug faster and design more secure connections. By the end of this article, you will understand exactly how the Sec-WebSocket-Key is generated, how the server validates it, and what common pitfalls to watch for in production.
What Is the Sec-WebSocket-Key Header?
The Sec-WebSocket-Key header is a mandatory field in the client's opening HTTP Upgrade request that initiates a WebSocket connection. It exists to prove to the server that the client intends to establish a WebSocket session rather than making an ordinary HTTP request.
Defined in RFC 6455, the header carries a base64-encoded representation of 16 random bytes generated by the client. The server does not use this value for authentication or authorization. Instead, it performs a deterministic calculation on the key and returns the result in the Sec-WebSocket-Accept response header. If the client receives the correct accept value, it knows the server speaks the WebSocket protocol.
This header differs from a security token in a critical way. A token proves identity and grants access. The Sec-WebSocket-Key proves protocol awareness. Think of it as a handshake challenge rather than a password. The client says, "I want to upgrade to WebSocket, and here is a value you must transform correctly if you understand the protocol." The server responds with the transformed value, confirming it is a real WebSocket endpoint and not a generic HTTP server that happens to receive upgrade requests.
The header name follows the Sec- prefix convention established by RFC 6455, which reserves these headers for protocol-level use. Browsers forbid setting Sec-WebSocket-Key manually in JavaScript, ensuring the value remains unpredictable and controlled by the browser's networking stack.
How the Sec-WebSocket-Key Is Generated
The client generates the Sec-WebSocket-Key by creating 16 cryptographically random bytes and encoding them as a base64 string. This produces a 24-character string that the browser places in the Upgrade request automatically.
Randomness is the core requirement. The 16-byte nonce must come from a cryptographically secure random number generator, not a predictable seed or a sequential counter. If the value were predictable, a malicious intermediary could precompute the correct Sec-WebSocket-Accept response and impersonate a WebSocket server. The randomness ensures each handshake is unique and resistant to replay attacks.
After generation, the raw bytes undergo base64 encoding. Base64 transforms binary data into a safe ASCII string that can travel in an HTTP header without corruption. The encoding produces exactly 24 characters because 16 bytes maps cleanly to four-character base64 groups with padding.
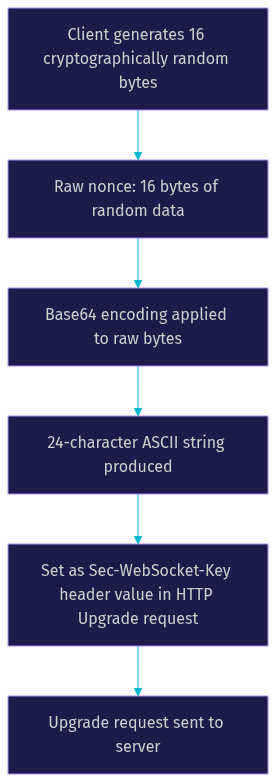
The browser handles this entire process transparently. When you create a WebSocket connection in JavaScript, the browser generates the nonce, encodes it, and attaches it to the request without any developer involvement. This is why you cannot set or override the Sec-WebSocket-Key header manually. The browser enforces this restriction to maintain the integrity of the handshake challenge.
Server-side WebSocket libraries perform the reverse operation. They decode the base64 string back to raw bytes, verify the length is 16 bytes, and then proceed with the accept calculation. If the decoded length does not match 16 bytes, the server must reject the handshake according to the RFC specification.
The Magic GUID and the Accept Calculation
When the server receives the Sec-WebSocket-Key, it performs a fixed series of transformations to produce the Sec-WebSocket-Accept header. This calculation is the heart of the WebSocket handshake validation.
The server takes the client's key and appends a specific GUID string: 258EAFA5-E914-47DA-95CA-C5AB0DC85B11. This GUID is defined in RFC 6455 and is the same for every WebSocket handshake worldwide. It is not a secret. Its purpose is to ensure the concatenated string could not reasonably appear in normal HTTP traffic, making accidental protocol confusion extremely unlikely.
After concatenation, the server computes a SHA-1 hash of the combined string. SHA-1 produces a 20-byte digest regardless of input length. The server then base64-encodes those 20 bytes, producing a 28-character string that becomes the Sec-WebSocket-Accept header value in the HTTP 101 Switching Protocols response.
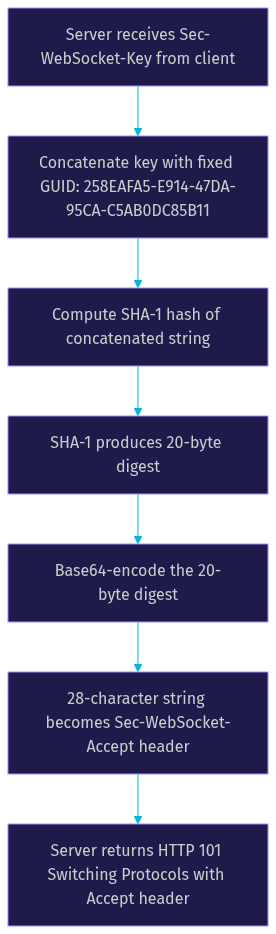
The client performs the same calculation locally and compares its computed value against the Sec-WebSocket-Accept header the server returned. If they match, the handshake succeeds and the connection upgrades from HTTP to WebSocket. If they do not match, the client aborts the connection.
This design is elegant in its simplicity. The calculation requires no shared secrets, no cryptographic keys, and no state on the server. The GUID acts as a domain separator, ensuring the hash input is unique to the WebSocket protocol. The SHA-1 algorithm, while no longer recommended for digital signatures, is perfectly adequate here because the accept calculation is not a security mechanism. It is a protocol awareness check.
One important detail: the GUID must be appended exactly as specified, including hyphens and uppercase letters. A single character difference produces a completely different SHA-1 hash and causes the handshake to fail. This is a common source of bugs in custom WebSocket server implementations.
Full Handshake Flow Overview
The WebSocket handshake is an HTTP Upgrade request that transitions the connection from HTTP semantics to WebSocket frame-based communication. Understanding the full flow helps you identify where failures occur.
The client initiates the handshake by sending an HTTP GET request with several required headers. The Upgrade header is set to websocket, signaling the desire to switch protocols. The Connection header is set to Upgrade, telling intermediaries that this request intends to change the transport protocol. The Sec-WebSocket-Key carries the base64-encoded nonce. The Sec-WebSocket-Version header is set to 13, indicating RFC 6455 compliance.
Optional headers may also appear. The Origin header identifies the page that initiated the connection, which servers can use for cross-origin validation. The Sec-WebSocket-Protocol header allows the client to propose one or more subprotocols, letting the server select one based on application requirements. The Sec-WebSocket-Extensions header enables negotiation of extensions like per-message deflate compression.
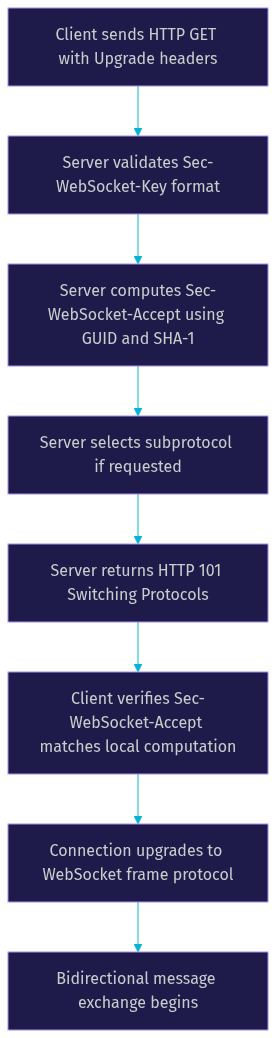
The server responds with HTTP status 101 Switching Protocols. This response includes the Upgrade and Connection headers echoed back, the Sec-WebSocket-Accept header with the computed value, and optionally the Sec-WebSocket-Protocol header if a subprotocol was negotiated. Once the client receives and validates this response, the HTTP connection transforms into a WebSocket connection capable of bidirectional, full-duplex communication.
This handshake flow is foundational to every WebSocket-based real-time system, including platforms like VideoSDK that build interactive live streaming and video calling experiences on top of WebSocket and WebRTC transport layers. The handshake ensures both parties agree on the protocol before any media or data frames flow.
Common Pitfalls and Debugging Tips
WebSocket handshake failures produce notoriously unhelpful error messages, especially in browser environments where the networking stack hides protocol-level details. Knowing the common failure modes helps you diagnose problems quickly.
Invalid key length is the first pitfall. If the Sec-WebSocket-Key decodes to anything other than 16 bytes, the server must reject the handshake. This typically happens when a custom client implementation generates the nonce incorrectly or when a proxy modifies the header in transit. Check the raw header value in the network tab and verify it is exactly 24 characters of valid base64.
Missing or incorrect GUID concatenation is another frequent issue in custom server implementations. If the server appends the GUID with different casing, omits the hyphens, or uses a different GUID entirely, the SHA-1 hash will not match what the client expects. The fix is straightforward: use the exact GUID from RFC 6455 without modification.
Proxy and load balancer interference causes some of the most frustrating handshake failures. Many reverse proxies and corporate firewalls strip or modify the Upgrade and Connection headers, treating them as hop-by-hop headers that should not be forwarded. When this happens, the backend server never sees the upgrade request and responds with a normal HTTP 200 instead of 101. The client interprets this as a handshake failure. To fix this, configure your proxy to forward Upgrade and Connection headers explicitly. In nginx, this means setting the Upgrade and Connection headers in the proxy configuration. In Apache, the modproxywstunnel module handles this automatically.
Mismatched Sec-WebSocket-Accept values occur when the server computes the accept incorrectly or when the client receives a response from a different server due to load balancer routing. Compare the server's computed value against a manually calculated value using the same key and GUID to identify the discrepancy.
Browsers surface WebSocket errors as generic "WebSocket connection failed" messages with no detail about which header caused the problem. Use browser developer tools to inspect the request and response headers directly. Look for the 101 status code, the presence of all required headers, and the correctness of the Sec-WebSocket-Accept value. For server-side debugging, log the incoming key, the concatenated string, and the computed accept value to trace exactly where the calculation diverges.
Security Perspective: What the Header Does Not Do
A critical misconception about the Sec-WebSocket-Key is that it provides authentication or security. It does not. The header is a protocol awareness mechanism, not a security control.
The Sec-WebSocket-Key cannot authenticate users, authorize access, or protect against malicious actors. The GUID used in the accept calculation is publicly documented in RFC 6455. Anyone can compute the correct Sec-WebSocket-Accept value for any given key. The handshake prevents accidental protocol confusion, not intentional attacks.
For actual security, you need additional layers. Origin validation is the first line of defense. The server should check the Origin header against an allowlist of trusted domains and reject connections from untrusted origins. This prevents cross-site WebSocket hijacking attacks where a malicious page opens a WebSocket connection to a victim server using the user's credentials.
Token-based authentication should be layered on top of the handshake. Pass an authentication token as a query parameter or in the Sec-WebSocket-Protocol header during the initial connection. The server validates this token before completing the upgrade. VideoSDK uses token-based authentication for exactly this reason, generating JWT tokens server-side and passing them to the SDK to authorize room access.
Always use TLS-secured WebSocket connections (wss) in production. The ws scheme sends all data, including the handshake headers, in plaintext over the network. With wss, the entire connection is encrypted using TLS, protecting the handshake and all subsequent frames from eavesdropping and tampering. The Sec-WebSocket-Key provides no confidentiality, so TLS is essential for any production deployment.
Implementing the Header in Popular Server Frameworks
Most production WebSocket implementations never require manual handling of the Sec-WebSocket-Key. Popular server libraries process the handshake automatically, computing the Sec-WebSocket-Accept and completing the protocol upgrade without developer intervention.
In Node.js, the ws library handles the entire handshake internally. When a client connects, the library validates the incoming Sec-WebSocket-Key, computes the accept value using the RFC 6455 GUID, and emits a connection event once the upgrade completes. Developers interact with the resulting WebSocket object for message exchange and never touch the raw headers. The same applies to the Socket.IO library, which builds on top of ws and adds additional protocol features.
In .NET Core, the WebSocket middleware processes the handshake as part of the HTTP request pipeline. The framework validates the upgrade request, computes the accept header, and exposes a WebSocket object through the context. Developers can add custom validation logic in middleware before the upgrade completes, such as checking the Origin header or validating authentication tokens.
In Java, the Spring Framework's WebSocket support handles the handshake through its WebSocketHandler infrastructure. The container validates the Sec-WebSocket-Key and completes the upgrade automatically. Developers register handlers for specific paths and focus on message processing rather than handshake mechanics.
Customization typically happens at the validation layer, not the handshake computation layer. Developers add interceptors or middleware to inspect the Origin header, validate authentication tokens, or negotiate subprotocols. The actual SHA-1 computation and GUID concatenation remain handled by the library. If you find yourself manually computing the Sec-WebSocket-Accept, you are likely building a custom WebSocket implementation from scratch, which is rarely necessary given the maturity of available libraries.
When building real-time applications with VideoSDK's Prebuilt UI Kit, the WebSocket and WebRTC handshake layers are managed entirely by the SDK. Developers focus on room creation, participant management, and feature configuration while the SDK handles protocol negotiation, connection establishment, and reconnection logic.
Testing the Handshake Manually
You can verify the Sec-WebSocket-Key and Sec-WebSocket-Accept exchange without writing any application code. Browser developer tools, command-line utilities, and online testers all provide visibility into the handshake process.
In Chrome or Firefox, open the Network tab in developer tools and filter by WS (WebSocket). Initiate a WebSocket connection from your application. Click the request that appears and inspect the Request Headers section. You will see the Sec-WebSocket-Key with its 24-character base64 value, along with the Upgrade, Connection, and Sec-WebSocket-Version headers. The Response Headers section shows the Sec-WebSocket-Accept value returned by the server.
To manually verify the accept calculation, copy the Sec-WebSocket-Key from the request, append the RFC 6455 GUID, and compute the SHA-1 hash using any online SHA-1 calculator. Base64-encode the resulting 20-byte hash and compare it to the Sec-WebSocket-Accept value in the response. If they match, the server is computing the accept correctly.
Online WebSocket testing tools like Postman, Piehost, or the browser-based WebSocket echo testers at websocket.org provide interactive interfaces for connecting to WebSocket endpoints and inspecting the handshake. These tools display the full request and response headers, making it easy to identify missing or malformed values without setting up a debugging proxy.
For server-side testing, tools like websockets.org's echo test or browser extensions that monitor WebSocket traffic can confirm that your server returns the correct 101 status code with all required headers. If the server returns 200 instead of 101, the upgrade is not being processed, which usually points to a proxy configuration issue or a server library that is not configured to handle WebSocket upgrades.
Definitions Glossary
Sec-WebSocket-Key: A required HTTP header in the WebSocket opening handshake that carries a base64-encoded 16-byte random nonce generated by the client to prove protocol awareness.
Sec-WebSocket-Accept: The response header computed by the server that confirms it understands the WebSocket protocol, produced by concatenating the client key with a fixed GUID, hashing with SHA-1, and base64-encoding the result.
RFC 6455: The Internet Engineering Task Force standard that defines the WebSocket protocol, including the handshake mechanism, framing format, and security considerations.
Magic GUID: The fixed string 258EAFA5-E914-47DA-95CA-C5AB0DC85B11 defined in RFC 6455 that servers append to the client key before hashing, ensuring the input is unique to the WebSocket protocol.
HTTP Upgrade Request: An HTTP request that asks the server to switch the current connection to a different protocol, such as from HTTP to WebSocket, using the Upgrade and Connection headers.
WebSocket Subprotocol Negotiation: The process where a client proposes one or more application-level subprotocols via the Sec-WebSocket-Protocol header and the server selects one, enabling protocol-specific communication over the WebSocket connection.
Key Takeaways
The Sec-WebSocket-Key is a protocol awareness mechanism, not an authentication or security control, and understanding this distinction prevents dangerous assumptions about WebSocket connection security.
The server computes the Sec-WebSocket-Accept by concatenating the client key with the RFC 6455 GUID, applying SHA-1, and base64-encoding the result, and any deviation in this process causes the handshake to fail.
Proxy configurations that strip the Upgrade and Connection headers are the most common cause of WebSocket handshake failures in production environments, and fixing this requires explicit header forwarding rules.
Popular server libraries like Node.js ws, .NET Core, and Java Spring handle the Sec-WebSocket-Key validation automatically, so developers rarely need to compute the accept value manually.
For production WebSocket security, always combine TLS-secured connections (wss), origin validation, and token-based authentication, as the handshake alone provides no protection against intentional attacks.
Conclusion
The Sec-WebSocket-Key header is a small but essential piece of the WebSocket protocol that ensures clients and servers agree on the communication protocol before exchanging data. By understanding how the 16-byte nonce is generated, how the magic GUID and SHA-1 hash produce the accept value, and where common failures occur, you can debug WebSocket connection issues with confidence and build more reliable real-time applications. For developers building production-grade video calling, live streaming, or audio room experiences, VideoSDK handles the underlying transport handshake and protocol negotiation automatically, letting you focus on application logic rather than protocol mechanics. You can start building for free at app.videosdk.live/login. What are you building with WebSockets or real-time communication? Drop a comment below, I would love to hear what kind of real-time use case you are working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ