


WebRTC P2P is a browser-native technology that lets two peers exchange audio, video, and arbitrary data directly, without routing media through an application server. Every WebRTC P2P connection is encrypted end-to-end with DTLS/SRTP by default, and the browser handles NAT traversal through ICE, STUN, and TURN automatically. For multi-party calls beyond roughly 4 to 6 participants, most teams switch from full-mesh P2P to a server-based SFU, which is exactly what VideoSDK provides out of the box with its video calling SDK.
Real-time communication used to mean plugins, Flash, or heavyweight server infrastructure. WebRTC changed that in 2011, and by 2026 it is a mature W3C standard supported in every major browser, on mobile, and even in embedded devices. The core idea is simple: two peers discover each other, negotiate a direct connection, and then exchange encrypted media and data with no server in the media path.
Developers choose WebRTC P2P over client-server architectures for three practical reasons. First, latency: a direct connection between two peers in the same region can deliver sub-100ms round trips, because there is no intermediary hop. Second, cost: media never touches your servers, so bandwidth bills stay flat no matter how long the call runs. Third, privacy: DTLS/SRTP encryption happens between the peers themselves, so even the signaling operator cannot decrypt the media.
That said, WebRTC P2P is not a silver bullet. The connection setup is genuinely complex, NAT traversal fails in a meaningful percentage of networks, and mesh topologies collapse under bandwidth pressure. This guide walks through the full picture: architecture, setup, media, security, scaling, and debugging.
What Is WebRTC P2P and How Does It Work?
WebRTC P2P is defined as the peer-to-peer operating mode of the WebRTC API suite, in which two browsers or runtimes establish a direct, encrypted transport for media streams and data channels. WebRTC P2P works by having each peer gather network candidates, exchange connection descriptions through an out-of-band signaling channel, and then let the ICE framework select the best working route between them.
The W3C WebRTC specification, maintained jointly with the WHATWG, defines the browser surface: the peer connection object, media capture, and the data channel. The IETF defines the wire protocols: SRTP for media, DTLS for key negotiation, and ICE for connectivity establishment. Together they form a complete, interoperable stack.
The trade-off is control versus convenience. You get encryption, congestion control, jitter buffering, and codec negotiation for free, but you also inherit the hard parts: signaling design, NAT traversal, reconnection handling, and multi-party scaling. Many teams eventually hand those hard parts to a managed platform like VideoSDK, which wraps the same WebRTC foundation in a room-based API with built-in recording, transcription, and adaptive streaming.
Core Architecture of a WebRTC P2P Connection
Every WebRTC P2P connection is built from three cooperating pieces: the peer connection object, the ICE/STUN/TURN connectivity machinery, and a signaling channel you supply yourself.
RTCPeerConnection Overview
The RTCPeerConnection is the central object in any WebRTC P2P setup. It represents one connection to one remote peer and manages everything attached to it: media tracks sent and received, data channels, ICE gathering, and statistics reporting. You create one per remote peer, attach your local media, and then drive it through a negotiation cycle of offers and answers. In a two-party call you have exactly one peer connection per side; in a full-mesh call of five people, each participant holds four of them, which is precisely why mesh scales poorly.
ICE, STUN, and TURN Explained
Before two peers can talk directly, each must figure out what its own reachable network addresses look like from the outside. That is the job of ICE, the Interactive Connectivity Establishment framework. ICE gathers candidates from several sources: the local interface address (host candidates), a public address discovered by asking a STUN server (server-reflexive candidates), and a relayed address provisioned on a TURN server (relayed candidates).
STUN is lightweight and cheap: the peer sends a request, the server replies with the observed public IP and port, and that becomes a candidate. TURN is the fallback for hostile networks, symmetric NATs, and strict corporate firewalls: media is relayed through the TURN server, which costs bandwidth and adds a hop but guarantees connectivity. Industry experience consistently shows that a small but stubborn fraction of users, often quoted around 10 percent depending on network population, cannot connect without TURN. Plan for TURN from day one.
Signaling: The Glue for WebRTC P2P
Signaling is the piece WebRTC deliberately does not standardize. The specification requires peers to exchange session descriptions (the offer and answer) and ICE candidates, but it leaves the transport entirely to you. Common choices are WebSockets, HTTP polling, or even QR codes and copy-paste for fully serverless setups. The signaling server only ever sees metadata, never media.
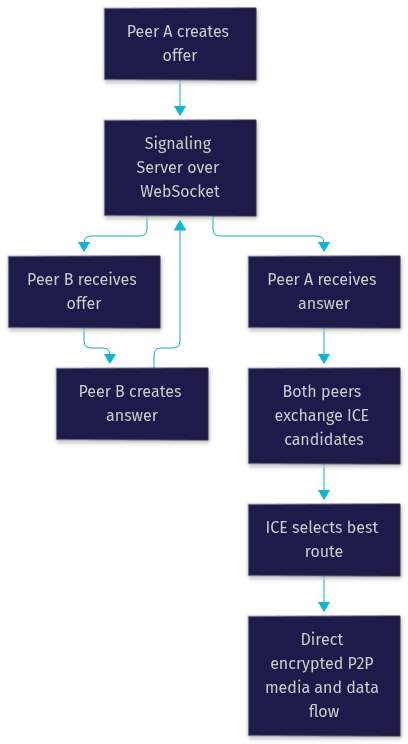
The flow is always the same: one peer creates an offer describing its media and capabilities, the other responds with an answer, both sides trickle ICE candidates as they discover them, and once ICE finds a working pair of addresses, the direct connection opens and signaling drops out of the loop.
Setting Up a Basic WebRTC P2P DataChannel
A data channel is a bi-directional, ordered or unordered pipe for arbitrary bytes, built on the same SCTP-over-DTLS transport as the media. It is the mechanism behind browser-based file transfer, P2P gaming, collaborative editors, and remote control interfaces.
Choosing a Signaling Transport
Your first decision is how the two peers will find each other. A WebSocket server is the default choice: it is simple, works through firewalls, and supports rooms for multi-peer discovery. HTTP polling works but adds latency and complexity. For truly serverless scenarios, developers have experimented with QR codes, Bluetooth, and manual copy-paste of connection codes, where the offer and answer are exchanged out of band entirely. Each approach trades convenience against infrastructure: WebSocket needs a small always-on server, while copy-paste needs none but only suits patient, technical users.
Creating Offers and Answers
The negotiation cycle follows a strict narrative. The initiating peer creates a peer connection, optionally creates a data channel before offering so it is included in the session description, and then generates an offer. The offer is a blob of session metadata describing what the peer wants to send and which codecs it supports. The receiving peer loads that offer into its own peer connection, generates an answer describing what it can accept, and sends it back. Both sides then begin ICE gathering, exchanging candidates through the same signaling channel until connectivity is established. The critical discipline is ordering: an answer must never be applied before the offer it responds to, and remote candidates should be queued if they arrive before the remote description is set.
Opening the DataChannel
Once negotiation completes, the data channel opens and both sides can send messages. You choose between two delivery modes at creation time. Reliable and ordered mode behaves like TCP: messages arrive in sequence, with retransmission of losses, which suits file transfer and state synchronization. Unreliable or unordered mode behaves like UDP: low latency, no retransmission, ideal for game state, cursor positions, and live telemetry where a stale message is worse than a lost one. Throughput on a healthy connection can reach tens of megabits per second, but it degrades under packet loss because SCTP congestion control backs off aggressively, so treat the data channel as a control-and-moderate-data plane, not a bulk transport replacement.
Adding Media Streams to a WebRTC P2P Call
Media is where WebRTC earns its reputation. The same peer connection that carries your data channel can carry synchronized audio and video, with the browser handling codec negotiation, jitter buffering, and bandwidth adaptation.
getUserMedia and MediaStream Handling
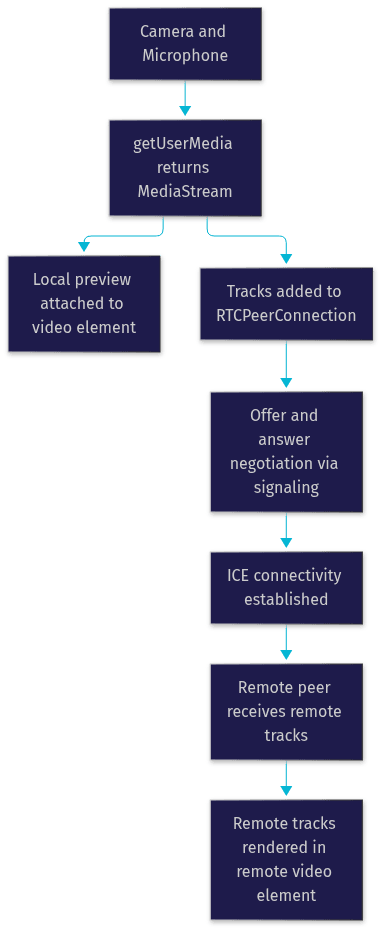
Everything starts with media capture. The browser's media capture API requests permission for camera and microphone and returns a media stream object containing live audio and video tracks. A parallel screen-capture API returns a stream for a shared window or display, with its own permission prompt. Each stream is a container of tracks, and tracks are the unit you actually send: you can enable, disable, or replace them at runtime, which is how mute buttons and camera switching are implemented without renegotiating the connection.
Attaching Media to RTCPeerConnection
Tracks are attached to the peer connection individually, and the modern API expects you to add tracks rather than whole legacy streams. When you attach tracks, the negotiation includes them in the offer, and the remote peer fires events as remote tracks arrive. Multiple tracks are fully supported: camera plus microphone plus screen share is a standard three-track setup. One practical detail that bites many first-time implementers: if you add media after the initial negotiation, you either need to renegotiate with a fresh offer-answer cycle or have pre-negotiated unused media descriptions, a technique the spec supports but which requires deliberate setup.
Managing Local Previews
Local preview is straightforward: attach your own captured stream to a muted video element so you never hear yourself. Remote rendering is where care is needed. Remote tracks arrive as separate events, and you should attach them to dedicated elements as they arrive rather than assuming a fixed order. For multi-party mesh calls, each remote peer's tracks need their own rendering slot, and you will want an active-speaker layout strategy, which is one of the reasons teams move to a managed SDK: VideoSDK's participant hooks expose each remote participant's audio and video tracks directly, along with active speaker detection, so you focus on layout instead of track plumbing.
Security and Privacy in WebRTC P2P
WebRTC P2P media is encrypted by default, and this is worth stating precisely: every media packet is protected with SRTP, whose keys are negotiated by DTLS during connection setup. There is no plaintext mode. The data channel uses DTLS directly. This means the signaling server, even if malicious, cannot decrypt your media, because it never sees the keys.
The real privacy considerations sit elsewhere. ICE candidates expose your local and public IP addresses to the remote peer by design, which enabled the historical problem of IP leakage through RTCPeerConnection even behind VPNs; modern browsers mitigate this with mDNS-anonymized host candidates, but you should still treat candidate exchange as sensitive metadata. Best practices: always run signaling over HTTPS and WSS, scope authentication tokens narrowly, never expose API secrets in frontend code, and validate every incoming session description against expected constraints to prevent malicious-forced media injection. If you build on a platform like VideoSDK, token-based room authentication and end-to-end encryption options handle most of this for you, as described in the authentication and token guide.
Scaling WebRTC P2P: Mesh vs. SFU
Pure P2P is a two-party technology at heart. Scaling it means understanding exactly where the mesh breaks.
Full-Mesh Limitations
In a full-mesh call, every participant maintains a peer connection to every other participant. The math is unforgiving: in a call of N participants, each uploader sends N minus 1 separate streams, and each client decodes N minus 1 incoming streams. For five people, each client uploads four video streams simultaneously. A typical home uplink saturates quickly, CPU spikes from encoding multiple streams and decoding many others, and the weakest participant degrades the experience for everyone. In practice, full-mesh video works acceptably up to roughly four participants, and becomes painful beyond six.
Introducing an SFU for Larger Rooms
The standard answer is a Selective Forwarding Unit. An SFU receives each participant's single upstream stream and forwards copies to everyone else, so each client uploads exactly one stream regardless of room size. Nobody decodes more than they display, and the server can apply simulcast layers, forwarding lower resolutions to bandwidth-constrained viewers. Hybrid architectures are common: keep P2P for one-to-one calls and route through an SFU the moment a third participant joins. This is precisely the architecture VideoSDK uses, with rooms, adaptive streaming, and automatic quality adjustment built in, so the mesh-to-SFU transition is a configuration decision rather than an engineering project. For larger broadcasts, interactive live streaming extends the same model to thousands of viewers with sub-second latency.
Debugging and Performance Tips for WebRTC P2P
WebRTC's hardest bugs are invisible without the right tools. Chrome ships a detailed internal diagnostics page listing every peer connection, its ICE state, candidate pairs, and per-stream statistics; Firefox offers an equivalent native tool. Both are the first stop when a connection fails silently.
Watch three metrics above all. ICE gathering time: if candidate gathering takes seconds, your STUN configuration or network is slow, and users will perceive it as the app being broken. Round-trip time and packet loss, available from the statistics API, tell you whether degradation is network-side or client-side. Freeze patterns that correlate with a single remote peer usually indicate that peer's uplink, not your server.
Two practical tips from production experience: always implement reconnection logic, because mobile networks drop peer connections constantly and the default behavior is a dead call until reload; and log the ICE candidate type that ultimately won, because a high relay percentage means your TURN costs are quietly scaling with usage. The WebRTC statistics specification defines the full metrics surface.
Real-World Examples and Libraries
You rarely build WebRTC P2P from raw APIs. PeerJS wraps the peer connection and signaling into a minimal abstraction with a free public signaling broker, ideal for prototypes and small projects. Simple-Peer, from the WebRTC community tooling ecosystem, is the standard choice for Node and browser bundlers, giving you a clean event-driven wrapper while leaving signaling entirely in your hands. For Python-based backends and AI pipelines, aiortc implements the WebRTC stack natively, which is the foundation for the VideoSDK Python SDK and its AI agent integrations.
Choosing between them is straightforward: PeerJS when you want zero signaling infrastructure for a demo, Simple-Peer when you control signaling and want a thin layer, and a full platform like VideoSDK when you need production concerns handled, including recording, transcription, roles, and multi-platform SDKs across React, Flutter, React Native, Android, iOS, and Unity.
Definitions Glossary
RTCPeerConnection: The browser API object representing one encrypted connection to one remote peer, managing media tracks, data channels, and ICE connectivity for that link.
ICE (Interactive Connectivity Establishment): The framework that gathers and tests candidate address pairs from both peers to find a working route, prioritizing direct connections over relays.
STUN server: A lightweight server that tells a peer its public IP and port as observed from the internet, enabling direct NAT traversal in most home and office networks.
TURN server: A relay server that forwards media when direct connection fails, guaranteeing connectivity at the cost of bandwidth and an extra network hop.
Data Channel: An SCTP-over-DTLS pipe inside a WebRTC P2P connection for sending arbitrary bytes, configurable as reliable-ordered or unreliable-unordered delivery.
SFU (Selective Forwarding Unit): A media server that receives each participant's single stream and forwards it to others, enabling large rooms where full-mesh P2P would saturate every uplink.
Key Takeaways
- WebRTC P2P connects two peers directly with mandatory DTLS/SRTP encryption, keeping media off your servers and latency low.
- ICE, STUN, and TURN solve NAT traversal automatically, but you must provision TURN because a significant minority of networks cannot connect without it.
- Signaling is deliberately unspecified by the standard, so you own the transport for offers, answers, and candidate exchange, typically over WebSockets.
- Full-mesh P2P video scales poorly past roughly four to six participants; an SFU architecture, which VideoSDK provides as managed rooms with adaptive streaming, is the production answer.
- Libraries like PeerJS and Simple-Peer accelerate prototypes, while VideoSDK's multi-platform SDKs handle the production concerns, from reconnection to recording, that raw WebRTC leaves to you.
Conclusion
WebRTC P2P remains one of the most elegant pieces of browser engineering: direct, encrypted, low-latency exchange of media and data with no server in the media path. Master the fundamentals here, ICE and signaling, data channels, media attachment, and the mesh-to-SFU transition, and you will understand every layer that platforms build on top of it. When you are ready to ship rather than scaffold, VideoSDK's quickstart gets a working video call running in minutes, with a free tier to start, and the code samples cover everything from screen share to live streaming. What are you building with WebRTC P2P? Drop a comment, I'd love to hear what kind of real-time use case you're working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ