


VoIP security and encryption protect both signaling data (SIP) and media streams (RTP) from interception, tampering, and eavesdropping. TLS secures SIP signaling by encrypting call setup metadata, while SRTP encrypts the actual voice and video media payload. VideoSDK provides built-in end-to-end encryption for real-time communication, handling both signaling and media layers so developers can ship secure voice and video applications without managing cryptographic infrastructure manually.
Voice over IP carries some of the most sensitive data in any organization: private conversations, DTMF tones representing credit card numbers, and metadata revealing who communicates with whom. In 2026, with regulatory frameworks like HIPAA, PCI-DSS, and GDPR enforcing strict data protection standards, unencrypted VoIP traffic is not just a security risk. It is a compliance violation waiting to happen.
This guide breaks down VoIP security and encryption across both attack surfaces: SIP signaling and RTP media. You will learn how TLS protects call setup, how SRTP secures voice payloads, how key exchange protocols like SDES and DTLS-SRTP work, and how platforms like VideoSDK handle encryption end to end so you can focus on building features instead of managing certificates.
What Is VoIP Security and Encryption?
VoIP security and encryption is defined as the set of protocols, practices, and cryptographic techniques used to protect voice and video communication transmitted over IP networks. It works by encrypting both the signaling layer (SIP) that handles call setup, routing, and teardown, and the media layer (RTP) that carries the actual audio and video payloads between participants.
Every VoIP call has two distinct data flows that need protection. The first is signaling: SIP messages that negotiate codecs, exchange IP addresses, manage call states, and carry metadata like caller IDs and dialing codes. The second is media: RTP packets that carry the actual voice or video content between participants. An attacker who intercepts only signaling learns who called whom and when. An attacker who intercepts only media hears the conversation. An attacker who intercepts both gets the complete picture.
Regulatory drivers have made VoIP encryption a legal requirement in many industries. HIPAA mandates encryption for protected health information transmitted over electronic channels, which includes telehealth voice calls. PCI-DSS requires encryption for any system that handles payment card data, including IVR systems that capture DTMF tones. GDPR Article 32 calls for "appropriate technical measures" to protect personal data, which European regulators have interpreted to include voice communication containing personal information.
VideoSDK addresses these requirements by providing end-to-end encryption as a built-in feature of its video calling SDK and audio calling capabilities. Rather than building cryptographic layers from scratch, developers can enable encryption at the room level, and VideoSDK handles key management, media encryption, and signaling protection across all supported platforms including React, Flutter, iOS, Android, and Python.
SIP Signaling Protection: TLS and Beyond
SIP signaling is the control plane of every VoIP call, and protecting it with TLS is the first line of defense against metadata exposure and call manipulation.
The Session Initiation Protocol (SIP) is a text-based signaling protocol used to establish, modify, and terminate real-time communication sessions. SIP messages carry caller identity, callee identity, codec preferences, IP addresses for media exchange, and call state information. Without encryption, every hop between the client and the SIP server exposes this metadata in plaintext to anyone with packet capture access.
Transport Layer Security (TLS) protects SIP signaling by establishing an encrypted tunnel between the VoIP client and the SIP server before any SIP messages are exchanged. The TLS handshake authenticates the server using X.509 certificates, negotiates a cipher suite, and derives session keys that encrypt all subsequent SIP traffic. SIP over TLS typically operates on port 5061, compared to port 5060 for unencrypted SIP over UDP or TCP.
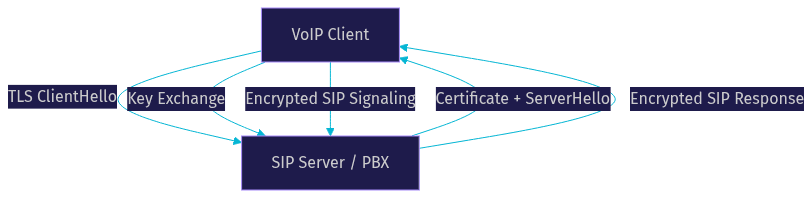
Certificate selection matters for SIP TLS. Domain-validated certificates from a trusted Certificate Authority provide basic identity verification. Extended Validation certificates offer stronger identity guarantees but are rarely necessary for internal SIP infrastructure. For internal deployments, self-signed certificates work if clients are configured to trust them, but this creates a management burden as certificate counts grow. For production systems handling external traffic, CA-signed certificates with automated renewal are the standard practice.
SIP over TLS has limitations that developers should understand. TLS protects the signaling path between the client and the first SIP proxy, but if that proxy forwards SIP to another server over unencrypted transport, the signaling is exposed on that hop. This is particularly common in SIP trunking scenarios where traffic crosses provider boundaries. End-to-end SIP encryption requires every hop in the signaling path to use TLS, which is not always under the developer's control.
Best practice configurations include enforcing TLS 1.2 or higher, disabling weak cipher suites, enabling certificate pinning on mobile clients to prevent man-in-the-middle attacks on SIP, and using mutual TLS for server-to-server SIP communication where both endpoints authenticate each other. The W3C WebRTC Security Architecture provides additional guidance on signaling security for browser-based communication.
Media Encryption with SRTP
RTP media carries the actual voice and video content, and without SRTP encryption, anyone on the network path can listen to conversations or inject audio.
Real-time Transport Protocol (RTP) is the standard protocol for delivering audio and video over IP networks. RTP packets contain the encoded media payload, sequence numbers for ordering, and timestamps for synchronization. Plain RTP has no encryption, meaning the media payload is transmitted in plaintext. On any network segment where an attacker can capture packets, the conversation can be reconstructed using freely available tools.
Secure Real-time Transport Protocol (SRTP) encrypts the RTP payload while preserving the RTP header structure needed for packet routing and sequencing. SRTP uses the Advanced Encryption Standard (AES) in Counter mode or AES in Galois/Counter Mode for confidentiality, and HMAC-SHA1 for integrity protection. The RTP headers remain visible to network devices, but the media payload is fully encrypted. The SRTP specification is defined in IETF RFC 3711.
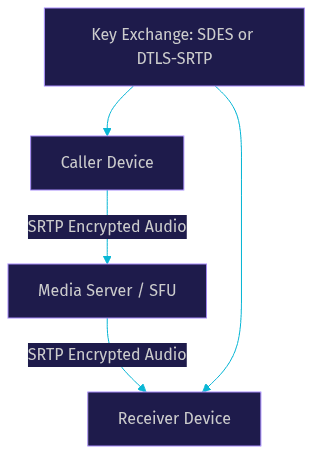
Key exchange is the critical decision point for SRTP. Two methods dominate: SDES (Session Description Protocol Security Descriptions) and DTLS-SRTP.
SDES exchanges SRTP keys through the SIP signaling channel. When the call is set up, the SDP body of the SIP message carries the SRTP cryptographic parameters. This means the security of the media keys depends entirely on the security of the signaling channel. If SIP signaling uses TLS, SDES keys are protected in transit. If signaling is unencrypted, the SDES keys are exposed and an attacker can decrypt the media.
DTLS-SRTP exchanges keys through a DTLS handshake on the media path itself, separate from the signaling channel. This approach is used by WebRTC and provides end-to-end key agreement even if the signaling channel is compromised. DTLS-SRTP is the stronger choice for browser-based VoIP and any scenario where signaling security cannot be guaranteed end to end.
The difference between SRTP and plain RTP is straightforward. Plain RTP provides zero confidentiality and zero integrity. An attacker can listen to the call, record it, and inject audio packets. SRTP provides confidentiality through AES encryption and integrity through HMAC authentication, preventing both eavesdropping and packet injection.
Combining TLS and SRTP: How VideoSDK Handles End-to-End Security
Securing only one layer of a VoIP call leaves the other layer completely exposed, which is why production deployments must encrypt both signaling and media.
A common mistake is securing SIP signaling with TLS while leaving media on plain RTP. The signaling is protected, so caller IDs and call metadata are safe. But the actual conversation travels in plaintext, and anyone capturing RTP packets can reconstruct the audio. The reverse is equally dangerous: encrypting media with SRTP while using SDES key exchange over unencrypted SIP means the SRTP keys travel in plaintext, making the media encryption trivially breakable.
The correct deployment pattern uses TLS for the entire signaling path and DTLS-SRTP (or SDES over TLS) for media encryption. This ensures that both the control plane and the data plane are protected independently. Even if one layer is compromised, the other remains secure.
VideoSDK's architecture follows this principle. When end-to-end encryption is enabled, VideoSDK encrypts both the signaling channel and the media streams. The WebRTC-based media path uses DTLS-SRTP for key exchange and SRTP for media encryption, while the signaling layer uses TLS. Developers do not need to configure cipher suites, manage key exchange, or rotate certificates manually. This is handled across video calling, audio calling, and telephony integration surfaces.
A checklist for verifying full-stack encryption includes: confirming TLS on every SIP signaling hop, verifying SRTP on every media path, checking that key exchange uses DTLS-SRTP or SDES over TLS (not SDES over plaintext SIP), validating that certificate chains are complete and trusted, and testing with packet capture tools to confirm no plaintext media or signaling is visible on the wire.
Key Management and Certificate Practices
Key management is where most VoIP encryption deployments fail, because certificates expire, key rotation is manual, and exchange protocols are misconfigured.
TLS certificates for SIP infrastructure should be generated using a trusted Certificate Authority for any externally reachable endpoint. For internal-only deployments, a private CA can issue certificates, but the CA's root certificate must be distributed to all clients. Self-signed certificates work for testing but create operational debt: every client needs manual trust configuration, and there is no revocation path if a private key is compromised.
Certificate rotation is the most common failure point. TLS certificates typically expire after 90 to 398 days, depending on the CA. Expired certificates cause silent call failures because SIP clients reject the TLS handshake. Automated certificate renewal using protocols like ACME (Automated Certificate Management Environment) eliminates this problem for CA-signed certificates. For private CA deployments, a certificate lifecycle management tool should track expiration dates and trigger renewal before expiry.
For SRTP key exchange, the choice between SDES and DTLS-SRTP has key management implications. SDES requires the signaling server to generate and distribute SRTP keys for every call, creating a centralized key management responsibility. DTLS-SRTP generates keys peer to peer during the DTLS handshake, distributing the key management burden across endpoints. For large-scale deployments, DTLS-SRTP is generally easier to operate because there is no central key store to protect.
OCSP (Online Certificate Status Protocol) stapling should be enabled on SIP servers to allow clients to verify certificate revocation status without making a separate OCSP request. This reduces handshake latency and prevents a compromised CA from being used to issue fraudulent certificates for SIP infrastructure.
Real-World Threats and Mitigation Strategies
VoIP systems face specific attack vectors that encryption directly addresses, along with threats that require additional hardening beyond cryptographic protection.
Eavesdropping is the most straightforward VoIP threat. An attacker with access to any network segment between the caller and callee can capture RTP packets and reconstruct the conversation using freely available tools like Wireshark combined with codec decoders. SRTP encryption makes the captured packets unreadable without the session key, rendering packet capture useless for audio reconstruction.
Credential theft targets SIP registration credentials. When a VoIP client registers with a SIP server, the registration message carries authentication credentials. Without TLS, these credentials can be captured and reused to register rogue devices, make fraudulent calls, or impersonate legitimate users. SIP digest authentication provides a hash-based challenge response mechanism, but without TLS protecting the signaling channel, the digest exchange is vulnerable to replay and offline dictionary attacks.
DTMF interception is a specialized form of eavesdropping that targets the dual-tone multi-frequency signals used for IVR menu navigation and payment entry. DTMF tones can be carried in-band within the RTP stream or out-of-band via SIP INFO or RFC 2833 telephony events. In all cases, unencrypted transport exposes DTMF to capture, which can reveal credit card numbers, PINs, and account codes. SRTP encryption protects in-band DTMF, and TLS protects out-of-band DTMF carried in SIP messages.
Toll fraud is the financial impact of credential theft. Attackers who capture SIP credentials can make international or premium-rate calls at the victim's expense. Toll fraud remains one of the most costly telecom crimes, with global losses estimated in the billions of dollars annually according to the Communications Fraud Control Association. Encryption prevents the credential theft that enables toll fraud, but additional hardening is needed.
Additional hardening measures include IP-based access control lists that restrict SIP access to known endpoints, SIP firewalls that detect and block anomalous signaling patterns, rate limiting on registration attempts to prevent brute force attacks, and proper NAT traversal configuration using STUN and TURN servers to avoid exposing SIP ports unnecessarily. VideoSDK's telephony and SIP integration includes IP whitelisting, geo-fencing, and secure SIP configuration to address these hardening requirements.
Performance Impact and Monitoring
Encryption adds computational overhead to VoIP systems, but modern hardware makes the impact negligible for most deployments.
The performance cost of VoIP encryption comes from two sources. TLS adds handshake latency when a call is established, typically adding 50 to 150 milliseconds to call setup time. SRTP adds per-packet encryption and authentication overhead, which increases CPU usage on both endpoints. On modern hardware with AES-NI instruction support, SRTP encryption overhead is under 1% of CPU per concurrent call. Without hardware acceleration, the overhead rises to 5 to 10% per call, which matters for high-density media servers handling hundreds of concurrent sessions.
Monitoring encrypted VoIP systems requires tracking both security metrics and quality of service metrics. Security metrics include TLS handshake success rates, certificate expiration warnings, SRTP key exchange failures, and cipher suite negotiation outcomes. Quality metrics include RTP jitter, packet loss, round-trip time, and Mean Opinion Score estimates. If encryption is causing quality degradation, it typically appears as increased jitter or higher packet loss on the media path.
VideoSDK's REST APIs provide session analytics that include both connection quality metrics and encryption status, allowing developers to monitor whether encryption is active and performing without degradation.
Deployment Checklist for VoIP Security and Encryption
A systematic approach to VoIP security ensures no layer is left unprotected. Use this checklist to verify your deployment covers every critical area.
Signaling security:
- Enable TLS 1.2 or higher on all SIP endpoints
- Use CA-signed certificates for externally reachable servers
- Configure mutual TLS for server-to-server SIP communication
- Disable weak cipher suites including RC4, DES, and MD5
- Enable certificate pinning on mobile VoIP clients
Media security:
- Enable SRTP on all RTP media paths
- Use DTLS-SRTP for key exchange in browser-based and WebRTC deployments
- Use SDES over TLS for traditional SIP endpoint deployments
- Verify no plain RTP packets are visible in packet capture tests
Key management:
- Automate TLS certificate renewal using ACME or equivalent protocols
- Monitor certificate expiration dates with proactive alerting
- Enable OCSP stapling on SIP servers
- Rotate SRTP keys per call session, never reuse across sessions
Access control:
- Implement IP-based ACLs on SIP endpoints
- Deploy a SIP firewall or session border controller for anomaly detection
- Rate-limit SIP registration attempts to block brute force attacks
- Use SIP digest authentication with strong, unique passwords
Compliance verification:
- Document encryption configurations for audit purposes
- Test with packet capture to verify no plaintext exposure on any network segment
- Map encryption controls to HIPAA, PCI-DSS, or GDPR requirements as applicable
- Review VideoSDK code samples for secure implementation patterns
Definitions Glossary
SIP (Session Initiation Protocol): A signaling protocol used to establish, modify, and terminate real-time communication sessions over IP networks. SIP carries call metadata, codec negotiations, and routing information, making it a primary attack surface in VoIP systems.
RTP (Real-time Transport Protocol): The protocol that delivers audio and video media packets between VoIP participants. Plain RTP has no encryption, leaving media payloads exposed to anyone with network capture access.
SRTP (Secure Real-time Transport Protocol): An extension of RTP that encrypts media payloads using AES and provides integrity protection through HMAC-SHA1. SRTP preserves RTP header structure for network routing while protecting the conversation content.
TLS (Transport Layer Security): A cryptographic protocol that encrypts communication between two endpoints. In VoIP, TLS protects SIP signaling by establishing an encrypted tunnel before SIP messages are exchanged.
DTLS-SRTP: A key exchange protocol that uses Datagram TLS to negotiate SRTP keys directly on the media path, independent of the signaling channel. DTLS-SRTP is the standard key exchange method for WebRTC-based VoIP systems and is used by VideoSDK for media encryption.
SDES (Session Description Protocol Security Descriptions): A method of exchanging SRTP keys through the SIP signaling channel. SDES security depends entirely on the signaling channel being encrypted with TLS.
E2EE (End-to-End Encryption): A cryptographic approach where media is encrypted on the sender's device and only decrypted on the receiver's device, with no intermediate server holding decryption keys. VideoSDK provides E2EE as a built-in feature for video and audio calling across all supported SDK platforms.
Key Takeaways
- VoIP security requires encrypting both layers: TLS for SIP signaling and SRTP for RTP media, because protecting only one layer leaves the other fully exposed to network level attackers.
- DTLS-SRTP is the preferred key exchange method for modern VoIP deployments because it negotiates keys on the media path independently of signaling security, while SDES is acceptable only when SIP signaling is fully encrypted with TLS.
- Regulatory frameworks including HIPAA, PCI-DSS, and GDPR make VoIP encryption a legal requirement for healthcare, payment processing, and any system handling personal data of EU residents.
- Certificate management is the most common failure point in VoIP encryption deployments, and automated renewal with expiration monitoring is essential for production systems.
- VideoSDK handles both signaling and media encryption end to end, including DTLS-SRTP key exchange, E2EE for media, and TLS for signaling, across all supported platforms including React, Flutter, iOS, Android, and Python.
Conclusion
VoIP security and encryption is not a single switch you flip. It is a layered defense that protects SIP signaling with TLS, secures RTP media with SRTP, manages keys through DTLS-SRTP or SDES over TLS, and hardens infrastructure with access controls and monitoring. Skipping any layer leaves conversations, credentials, or metadata exposed to network level attackers.
If you are building a voice or video application, the fastest path to production grade encryption is a platform that handles both layers for you. VideoSDK provides end-to-end encryption, secure signaling, and DTLS-SRTP media protection as built-in features across its video calling, audio calling, and telephony products. You can start building for free with a VideoSDK account and enable encryption at the room level without managing certificates or cipher suites. The open-source VideoSDK agents SDK on GitHub provides additional reference implementations for secure AI voice integrations.
What are you building with VideoSDK? Drop a comment below. I would love to hear what kind of secure communication use case you are working on, whether it is telehealth, customer support, or an internal voice platform.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ