


Packet loss is the failure of one or more transmitted data packets to arrive at their destination, typically caused by network congestion, faulty hardware, or wireless interference. Even 1% loss can degrade VoIP calls, video streams, and real-time applications, because protocols like TCP must retransmit while UDP simply drops the data. This guide covers the causes, detection methods, and mitigation strategies you can apply today, including how real-time communication platforms like VideoSDK handle loss with network-adaptive streaming.
Every network engineer, game developer, and SRE has seen the same symptom: video calls freeze, voice audio breaks up, and file transfers crawl. The culprit is often packet loss, one of the most common and most misunderstood network performance problems. Unlike latency, which delays data, packet loss destroys it in transit, forcing recovery mechanisms that add delay, jitter, and frustration.
For applications built on real-time communication, the stakes are high. A telemedicine consultation, a live shopping stream, or an online classroom cannot tolerate sustained loss without visible quality collapse. By the end of this article, you will understand what packet loss is, what causes it, how to detect and measure it, and, most importantly, how to mitigate it across Wi-Fi, WAN, and cloud environments.
What Is Packet Loss and How Does It Work?
Packet loss is defined as the disappearance of data packets between their source and destination on a network. All digital communication, from a web page load to a video call, is broken into small units called packets. Each packet carries a portion of the payload plus headers that tell routers where to send it. Under normal conditions, every packet arrives. When one or more packets fail to arrive, that is packet loss.
Packet loss works differently depending on the transport protocol. TCP detects missing packets through sequence numbers and retransmits them, which preserves data integrity but adds latency and reduces throughput. UDP, used by VoIP, video streaming, and online gaming, has no built-in retransmission. A lost UDP packet is simply gone, which is why a single percent of loss can make a voice call sound robotic or a game feel unresponsive.
There is an important distinction between transient and persistent loss. Transient loss happens in short bursts, often during momentary congestion or a Wi-Fi channel spike, and most applications absorb it gracefully. Persistent loss is continuous or recurring, usually pointing to a hardware fault, a misconfigured link, or chronic oversubscription. Persistent loss is the kind that requires structured troubleshooting, and it is the focus of most of this guide.
Common Causes of Packet Loss
Packet loss almost always traces back to one of a handful of root causes, and identifying which one you are facing is half the battle. The two dominant categories are physical layer problems and congestion-related drops.
Physical Layer Issues
Physical layer issues are the most overlooked cause of packet loss because they are invisible to software monitoring. Damaged or degraded cabling, such as a kinked Ethernet cable or one exposed to interference, corrupts packets at the frame level. When a receiving interface computes a frame check sequence (FCS) and the result does not match, the frame is discarded, registering as an input error and packet drop on the switch port.
Connector corrosion, loose RJ45 terminations, and dirty fiber connectors produce the same effect intermittently. Failing hardware, including aging network interface cards, overheating switches, and failing power supplies in routers, also generates errors that manifest as loss. If your loss counters climb on a specific switch port while other ports stay clean, the problem is almost certainly physical, and replacing the cable or transceiver usually resolves it.
Congestion and Buffer Overflow
Congestion is the most common cause of packet loss on shared and WAN links. Every router and switch interface has a finite buffer that holds packets waiting to be transmitted. When incoming traffic exceeds the interface's capacity, a state called bandwidth saturation, the buffer fills. Once the buffer is full, the device has no choice but to drop newly arriving packets.
This is not a malfunction; it is how networks behave under oversubscription. Internet service providers routinely oversubscribe access links, betting that not all customers use full bandwidth simultaneously. During peak evening hours, that bet fails, buffers overflow, and customers see packet loss on ISP links. On local networks, congestion loss often appears when backup jobs, large file transfers, or multicast traffic compete with latency-sensitive applications on the same uplink without any quality of service (QoS) prioritization in place.
How to Detect Packet Loss
Detecting packet loss is a systematic process that moves from broad measurement to precise localization. The goal is to answer two questions: how much loss is occurring, and where in the path is it happening.
Using Ping and Traceroute
The simplest detection method is the ICMP echo request, commonly known as ping. By sending a series of echo requests to a destination and counting the responses, you get a direct packet loss percentage. A continuous ping to your default gateway tests the local LAN, while a ping to a public address tests the full path including your ISP. If loss appears only on the external target, the problem is beyond your local network.
Traceroute extends this by sending probes with increasing time-to-live values, forcing each router along the path to respond. When a specific hop shows consistent loss while later hops are clean, that router or the link into it is the likely drop point. A hop showing loss only for packets addressed to itself, while forwarding traffic cleanly, is often an artifact of rate-limited control traffic rather than real loss, so always compare hop behavior against end-to-end results before drawing conclusions.
Advanced Monitoring Tools
For deeper analysis, packet capture and dedicated monitoring tools reveal what ping cannot. Wireshark captures live traffic and flags TCP retransmissions, duplicate acknowledgments, and out-of-order segments, all signatures of loss on TCP flows. On Windows, the built-in packet monitor tool provides similar capture capability without third-party software. Network performance monitors that use SNMP and flow data, such as those feeding on interface error counters and queue drop statistics, expose loss at the device level across your entire infrastructure.
For real-time applications, monitoring RTP stream statistics is essential. Video conferencing platforms report packet loss, jitter, and round-trip time per stream, letting you correlate user complaints with objective network data. VideoSDK's real-time communication platform exposes these per-participant network quality metrics, so developers can detect degradation and trigger adaptive behavior before users notice.
Interpreting Loss Metrics
Acceptable packet loss thresholds depend on the application. For general web browsing and file transfer, up to 2% is tolerable because TCP retransmission hides it. For VoIP and video conferencing, anything above 1% becomes audible and visible, and 5% makes calls unusable. Online gaming is the most sensitive, with even 0.5% loss introducing noticeable input lag and desync. Cloud application SLAs typically target under 0.1% on internal links.
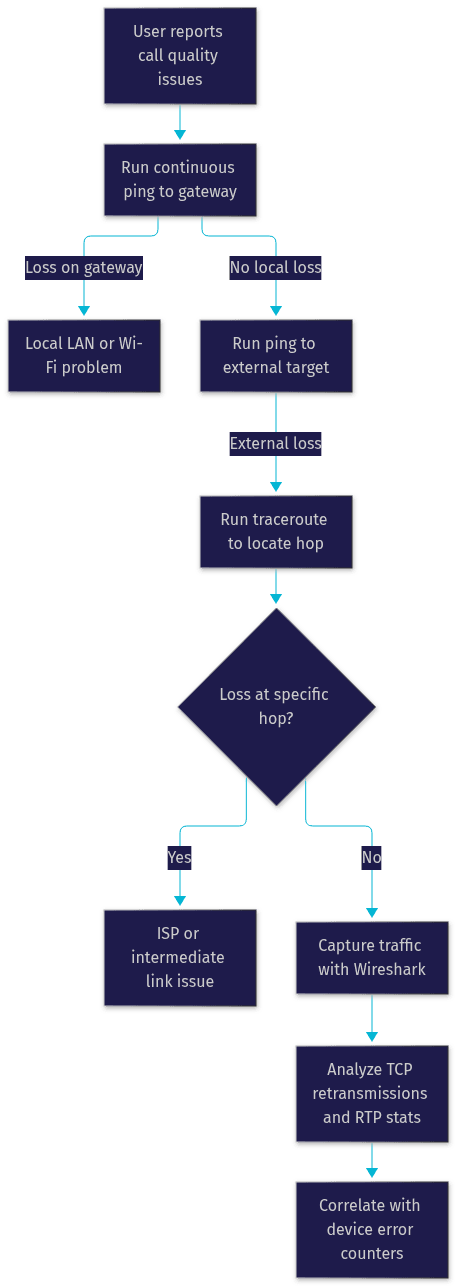
The following workflow shows how detection typically proceeds from symptom to diagnosis:
Measuring the Impact of Packet Loss
Packet loss does not affect all applications equally, and understanding the impact profile helps you prioritize fixes. The relationship between loss and TCP throughput is particularly brutal. Because TCP interprets loss as a congestion signal, its congestion control algorithm cuts the sending rate dramatically on every drop, then ramps back up slowly. The well-known Mathis equation models this: even small loss percentages cap TCP throughput far below link capacity, which is why a 1% loss on a gigabit link can reduce a large file transfer to a fraction of its potential speed.
For VoIP, the impact is immediate and audible. Lost RTP packets mean missing audio segments, producing the characteristic choppy, robotic voice quality. Modern codecs with packet loss concealment can mask brief losses, but sustained loss above 2% defeats concealment entirely.
Video streaming splits into two behaviors. Adaptive bitrate streaming over TCP buffers aggressively and retransmits, so loss manifests as quality reduction and rebuffering rather than visible corruption. Real-time interactive video over UDP, like a video call, has no such safety net. A lost packet means a frozen frame tile or a visual glitch.
Online gaming suffers in a distinctive way. Because game state updates travel over UDP, lost packets mean missed position and action updates, producing rubber-banding, teleporting characters, and hit registration failures. A real-world example: a competitive player on a congested home Wi-Fi network experiencing 3% loss will see opponents stutter and warp, even with a fast connection otherwise, because the loss, not raw bandwidth, is the binding constraint.
How to Mitigate Packet Loss
Mitigation strategy depends entirely on the loss source, so the first rule is: diagnose before you change anything. The strategies below are grouped by layer, matching the causes identified earlier.
Network Design Best Practices
Good design prevents most congestion-related loss before it happens. Segment latency-sensitive traffic, such as voice and video, onto separate virtual LANs or traffic classes so bulk transfers cannot starve them. Apply QoS policies that prioritize real-time traffic, letting routers mark and queue voice and video packets ahead of file transfers during congestion. Provision adequate headroom on critical links; a link that runs above 70% utilization during peak hours is a buffer overflow waiting to happen.
For real-time applications specifically, choose infrastructure that handles loss gracefully at the application layer. VideoSDK's network-adaptive streaming automatically adjusts bitrate and resolution based on real-time bandwidth conditions, so when loss and congestion appear, the stream degrades smoothly instead of collapsing. This is a meaningful advantage over hand-rolled WebRTC deployments, where adaptive behavior must be engineered from scratch.
Hardware and Configuration Tweaks
When loss traces to the physical layer, hardware fixes are the answer. Replace suspect cables, especially anything bent, pinched, or running alongside power lines. Verify that Ethernet runs stay within the 100-meter standard, and re-terminate connectors showing FCS or input errors on switch port counters. Upgrade aging interfaces from older standards to gigabit or multi-gig where congestion and errors coexist.
Configuration tweaks also help. Enabling flow control on congested links lets a receiving device signal the sender to pause briefly rather than drop packets, though use it carefully since it can propagate pauses across unrelated traffic. Reviewing MTU settings to avoid fragmentation on tunnel and VPN paths prevents fragmentation-related drops. Keeping switch and router firmware current resolves known buffer management bugs that vendors patch over time.
Software-Level Strategies
At the protocol and application layer, several techniques reduce the effective impact of loss. TCP window scaling and modern congestion control algorithms, such as BBR, improve throughput on lossy paths by responding to loss more intelligently than legacy algorithms. Tuning retransmission timers reduces recovery delay after drops. For UDP-based real-time media, forward error correction sends redundant data so the receiver can reconstruct small losses without retransmission, and jitter buffers smooth out the arrival timing of packets that do get through.
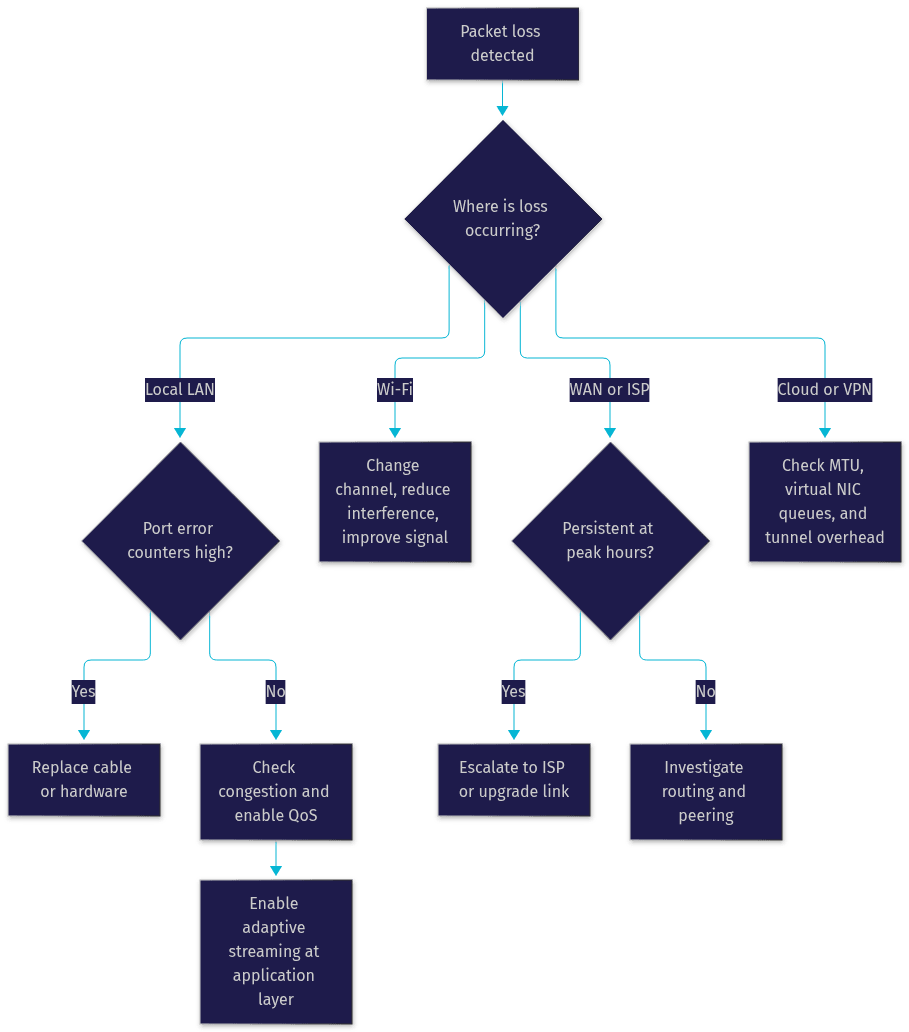
The decision tree below maps loss sources to the right mitigation path:
Packet Loss in Specific Environments
Wi-Fi and Wireless Networks
Wireless networks lose packets for reasons that wired networks never encounter. Radio interference from neighboring networks, microwave ovens, and Bluetooth devices corrupts frames in the air. Channel overlap between your access point and nearby ones forces retransmissions and eventual drops. Weak signal strength at the network edge increases error rates as modulation drops to slower, more fragile schemes. Mitigation means selecting clean channels, using the 5 GHz or 6 GHz bands where available, positioning access points to minimize dead zones, and reducing the number of devices sharing each channel.
WAN and ISP Links
Loss on WAN and ISP links usually originates outside your control. Congested peering points between providers, fiber cuts, and routine ISP oversubscription during evening peaks all generate loss that no local configuration can fix. Detecting it requires comparing loss at your gateway against loss at multiple external targets. If loss appears only toward one destination network, the fault sits at a peering or routing point. Persistent peak-hour loss justifies an ISP escalation, and for business-critical traffic, a second provider or an SD-WAN path that steers around lossy links provides resilience.
Cloud and Virtual Networks
In cloud environments, packet loss hides in places physical networks do not have. Virtual NICs share physical host bandwidth, and hypervisor overhead under heavy multi-tenant load can drop packets in virtual switches before traffic ever reaches the physical network. Noisy neighbors on shared infrastructure create bursty congestion. VPN tunnels add encapsulation overhead that can force fragmentation and drops when MTU is mismatched. Monitoring inside the cloud tenant, checking virtual interface drop counters, and validating tunnel MTU end to end are the standard diagnostic moves.
Proactive Monitoring and Alerting
Reactive troubleshooting finds loss after users complain. Proactive monitoring finds it first. Set explicit loss thresholds per environment: alert when loss exceeds 0.5% on internal links for more than five minutes, and alert immediately when real-time application streams report loss above 1%. Configure SNMP traps from switches and routers so buffer drops and interface errors notify your monitoring platform the moment they occur rather than waiting for a polling cycle.
Integrate these signals into a central monitoring platform so loss data correlates with device health, traffic graphs, and application metrics. A spike in loss that coincides with a backup job starting tells a different story than the same spike at 9 PM on an ISP link. For teams building real-time applications, surface per-stream network quality to operators through your platform's analytics. VideoSDK's REST APIs for session analytics let engineering teams pull post-call quality data, including loss and jitter per participant, turning user complaints into measurable, trendable evidence.
Definitions Glossary
Packet loss: The failure of one or more data packets to reach their destination, caused by congestion, hardware faults, or transmission errors, and measured as a percentage of total packets sent.
Jitter: The variation in packet arrival times over a network. Jitter often accompanies packet loss and degrades real-time audio and video even when average latency is low.
FCS error: A frame check sequence error, detected when a received frame's checksum does not match its contents, indicating corruption that causes the frame to be discarded.
Buffer overflow: The condition where a network device's packet queue fills completely because incoming traffic exceeds interface capacity, forcing the device to drop newly arriving packets.
TCP retransmission: The mechanism by which TCP resends packets that were not acknowledged, preserving data integrity at the cost of added latency and reduced throughput.
Network-adaptive streaming: The automatic adjustment of bitrate and resolution based on real-time network conditions, used by VideoSDK to keep video calls stable when bandwidth fluctuates.
Key Takeaways
- Packet loss is the disappearance of data packets in transit, and its impact ranges from slow TCP transfers to unusable VoIP and video calls, with real-time applications degrading noticeably above 1% loss.
- Congestion and buffer overflow cause most packet loss on shared and WAN links, while physical layer faults like damaged cables and FCS errors dominate on local networks.
- Detection follows a workflow: continuous ping to the gateway, ping to external targets, then traceroute to localize the failing hop, supported by packet capture and device error counters.
- Mitigation must match the source: QoS and bandwidth provisioning for congestion, cable and hardware replacement for physical faults, and channel optimization for Wi-Fi.
- Application-layer resilience matters as much as network fixes; platforms like VideoSDK provide network-adaptive streaming that adjusts bitrate and resolution in real time, keeping calls usable even on lossy connections.
Conclusion
Packet loss is a solvable problem, but only when you diagnose it systematically instead of guessing. Measure loss with ping and traceroute, localize it against device error counters, and apply the mitigation that matches the source: QoS for congestion, hardware replacement for physical faults, and channel management for wireless. For teams shipping real-time video and voice applications, pair good network practice with infrastructure that adapts to loss rather than breaking under it. VideoSDK's real-time communication SDKs handle network-adaptive streaming, jitter buffering, and per-participant quality monitoring out of the box, so your users get stable calls even when the network misbehaves. Explore the VideoSDK quickstart or grab a free tier at app.videosdk.live to see it in action. What kind of real-time application are you building, and how is packet loss affecting it? Drop a comment, I'd love to hear your use case.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ