


The RTMP protocol is a TCP-based streaming protocol originally developed by Macromedia (later Adobe) that carries audio, video, and data messages over a persistent connection. It remains the dominant standard for live ingest, where an encoder pushes a stream to a media server or streaming CDN, even though browser playback has largely moved to HLS and DASH. Developers building live pipelines with VideoSDK can push RTMP output to YouTube, Twitch, and other platforms directly from an interactive live streaming session.
Every time you watch a live stream on Twitch or YouTube, there is a good chance the video reached the platform through the RTMP protocol. Despite being more than two decades old, RTMP still powers the first mile of live streaming: the connection between a broadcaster's encoder and the platform's ingest servers.
That persistence is not nostalgia. RTMP delivers low, predictable latency over a single persistent TCP connection, which is exactly what live contribution needs. The playback side of the stack has moved on to HTTP-based protocols, but the ingest side keeps coming back to RTMP because it is simple, universally supported by encoders, and well understood.
If you build streaming infrastructure, you will encounter RTMP whether you chose it or not. This guide covers how the protocol works at the wire level, how to secure it, how to set up a production ingest pipeline, and how it compares with modern alternatives like HLS, DASH, and SRT.
What Is the RTMP Protocol?
The RTMP protocol is defined as a TCP-based message protocol for transporting audio, video, and control data between a client and a server in real time. Macromedia introduced it in the late 1990s as the transport layer for Flash Player communication with Flash Media Server, and Adobe later published the specification, which is why most modern implementations trace back to the Adobe RTMP specification.
RTMP works by maintaining a single persistent TCP connection over which the client and server exchange structured messages. Each message carries a type (audio, video, command, data, or control), a timestamp, and a payload. Because the connection stays open for the entire session, there is no per-segment HTTP negotiation, which keeps end-to-end latency low, typically in the range of two to five seconds for a well-tuned pipeline.
The protocol's core purpose today is live ingest: an encoder such as OBS or FFmpeg pushes a compressed stream to an RTMP endpoint on a media server or streaming CDN, which then transcodes and repackages it into HLS or DASH for viewer playback. VideoSDK's interactive live streaming follows this same pattern, allowing a host's stream to be forwarded to external platforms through RTMP output while viewers watch with sub-second latency inside the app.
Core Characteristics of the RTMP Protocol
Four characteristics define RTMP's behavior. First, it runs over TCP, usually on port 1935, which guarantees ordered, reliable delivery at the cost of head-of-line blocking on lossy networks. Second, it is chunked: large messages are split into smaller chunks so that audio and video can be interleaved on one connection. Third, it is low latency by design, since the persistent connection avoids the buffering windows that segmented HTTP protocols require. Fourth, it supports encryption and tunneling variants, RTMPS over TLS and RTMPT over HTTP, which keep it viable in security-conscious and firewall-restricted environments.
How the RTMP Handshake Works
Every RTMP session begins with a three-phase handshake in which client and server exchange fixed-size packets to establish a working connection. The handshake is the first thing that fails when something is misconfigured, so understanding it pays off immediately during RTMP troubleshooting.
The client initiates by sending the C0 and C1 packets. C0 is a single byte declaring the protocol version. C1 is a larger packet containing a timestamp, a timestamp copy used as a random value, and a block of random data. At this point the client has announced its presence and its clock, but nothing is confirmed yet.
The server responds with S0, S1, and S2. S0 is the version byte, S1 mirrors the structure of C1 with the server's own timestamp and random data, and S2 echoes back the client's timestamp and random data from C1. The echo is the proof: by returning the exact random bytes the client sent, the server demonstrates that it actually received C1 and is a live, responsive peer rather than a stale or replayed connection.
The client completes the cycle by sending C2, which echoes the server's timestamp and random data from S1. Once both sides have confirmed receipt of each other's initial packets, the handshake is complete and the connection transitions to message exchange. The whole sequence takes a few round trips, which is a negligible fraction of a second on a healthy network.
This design matters for reliability. Because both sides verify each other's random payloads, the handshake detects dead peers, half-open connections, and some classes of misconfigured middleboxes before any media flows. When you see a handshake failure in practice, the usual causes are a blocked port 1935, a TLS mismatch on RTMPS endpoints, or an ingest server that expects a different protocol version.
RTMP Chunk Stream Architecture
After the handshake, all communication happens through chunk streams, the protocol's mechanism for multiplexing multiple logical message streams over the single TCP connection. Understanding the chunk stream layer is the key to understanding RTMP's packet structure.
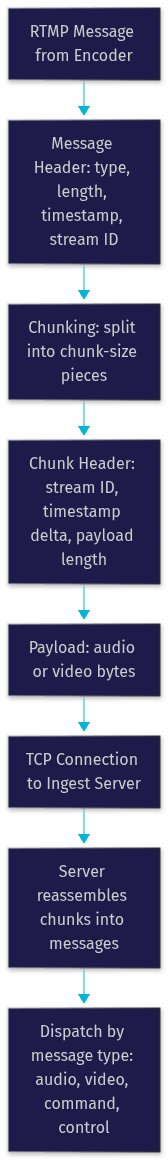
Every message, whether it is a video frame, an audio packet, or a command, is broken into chunks. Each chunk is prefixed by a chunk header that identifies which stream it belongs to, how large the original message is, and what timestamp it carries. The receiver reassembles chunks into complete messages using this metadata and then dispatches them based on message type.
The protocol defines a default chunk size, and either side can change it mid-session by sending a control message. Larger chunk sizes reduce per-chunk header overhead, which improves throughput for video, while smaller chunk sizes allow audio to be interleaved more frequently, which improves latency and smoothness. Tuning this value is one of the most practical RTMP optimizations.
Timestamps can be absolute or relative. When a chunk carries a delta timestamp, the receiver adds it to the previous timestamp for that stream to reconstruct the true delivery time. This delta encoding keeps headers small, which matters when you are sending thousands of chunks per second.
Chunk Types and Their Use Cases
RTMP defines four chunk header types, numbered 0 through 3, which trade header size against information completeness. Type 0 headers are the largest and carry the full set of fields: absolute timestamp, message length, and message type. They are used when a stream's parameters change, such as a new video frame type or a resolution switch. Type 1 headers omit the stream ID, assuming the same stream as the previous chunk, and carry a relative timestamp. Type 2 headers carry only a timestamp delta, used when message length and type are unchanged, which is common for steady audio. Type 3 headers carry no fields at all and are used for continuation chunks and for messages whose timestamp delta matches the previous one. The progression from Type 0 to Type 3 lets encoders minimize overhead dramatically on stable streams.
RTMP Message Types
Once reassembled, every chunk stream delivers messages, and the message type determines how the server handles the payload. The protocol reserves type numbers for the core categories that a live pipeline depends on.
Audio messages carry encoded audio frames, typically AAC, with a small header byte indicating codec and sample rate. Video messages carry encoded video frames, typically H.264, with a header distinguishing keyframes from interframes. The keyframe distinction is critical: a server can only start delivering a stream to a new viewer from a keyframe, which is why keyframe interval directly affects join time.
Data messages carry metadata using the Action Message Format, including details like video resolution, frame rate, and encoder settings. Command messages carry the protocol's control vocabulary: creating a stream, publishing to it, playing back a stream, and responding with status events such as a successful publish or an authentication rejection. Control messages, sent on a dedicated system stream, handle chunk size negotiation, window acknowledgments for flow control, ping keepalives, and stream-specific commands like pausing buffer flow.
In a real-world scenario, an OBS broadcast uses command messages to authenticate and open a publish stream, then interleaves audio and video messages over separate chunk streams, with control messages continuously managing flow and keepalives. A streaming CDN receiving that ingest uses the metadata data message to decide transcoding parameters before repackaging to HLS.
Security Extensions: RTMPS and RTMPT
Plain RTMP sends media in the clear, which is unacceptable for many production pipelines. Two variants address this, and choosing between them depends on your threat model and network environment.
RTMPS wraps the entire RTMP session in TLS, the same encryption layer that protects HTTPS. The handshake, commands, and media payloads are all encrypted, which prevents eavesdropping and protects stream keys from interception. Most major platforms, including YouTube and Twitch, now prefer or require RTMPS for ingest. The tradeoff is modest: a TLS handshake adds a small startup cost, and CPU overhead for encryption is negligible on modern hardware.
RTMPT tunnels RTMP inside HTTP requests, encapsulating protocol packets in HTTP bodies. Its purpose is firewall traversal: networks that block non-standard ports like 1935 often allow outbound HTTP. RTMPT adds meaningful overhead and latency because of HTTP's request-response framing, so treat it as a fallback for restrictive networks rather than a default. A third variant, RTMPE, used Adobe's proprietary encryption and is effectively deprecated; do not build new infrastructure around it.
For production ingest in 2026, the practical guidance is simple: use RTMPS wherever the ingest endpoint supports it, keep RTMPT available only for edge cases, and never rely on plain RTMP for anything carrying credentials or sensitive content.
Setting Up an RTMP Ingest Pipeline
A production RTMP ingest pipeline has four components: an encoder, an ingest endpoint, an authentication layer, and a distribution network. Getting each right is what separates a stable broadcast from a flaky one.
Start with the encoder. OBS Studio is the standard choice for interactive broadcasting, while FFmpeg suits automated and server-side pipelines. Configure the encoder with an H.264 keyframe interval of two to four seconds, a consistent bitrate appropriate to your resolution, and AAC audio. These settings matter because the ingest server repackages whatever you send, and irregular keyframes or fluctuating bitrates degrade every downstream format.
Next, configure the ingest URL. The encoder pushes to a URL that combines the server address, application name, and stream key, for example pointing at your media server or CDN ingest region. Choose an ingest region geographically close to the encoder to minimize round-trip time and handshake latency. If you are building your own ingest service rather than pushing to an existing platform, you will run a media server that accepts RTMP and outputs HLS, DASH, or RTMP forwarding.
Authentication deserves special attention. A stream key embedded in a URL is a shared secret, and anyone who obtains it can publish to your endpoint. Production systems generate short-lived, token-based credentials from an authentication server, validate them at ingest time, and revoke them on abuse. VideoSDK's architecture follows this pattern: tokens are generated server-side and scoped to specific rooms and permissions, and the same principle applies to ingest authorization.
Finally, connect the ingest to distribution. The flow works as follows: the encoder, such as OBS or FFmpeg, pushes the stream over an RTMPS connection to the ingest endpoint. Before the stream is accepted, an authentication server validates the token and stream key associated with the request. The validated feed arrives at the RTMP ingest endpoint, which may be a self-hosted media server or a CDN ingest region. From there, the server transcodes and repackages the feed into HLS or DASH segments that are delivered to viewers over HTTP. In parallel, the same feed can be forwarded via RTMP to destinations like YouTube and Twitch for multi-platform broadcasting. A VideoSDK interactive live streaming session plugs into this flow by pushing its RTMP output directly into the same ingest endpoint, so an in-app host broadcast reaches external platforms while in-app viewers continue watching with sub-second latency.
Common Pitfalls and How to Avoid Them
Four failure modes account for most RTMP ingest problems. Handshake failures usually mean port 1935 is blocked or the endpoint requires RTMPS while the encoder is configured for plain RTMP; verify the URL scheme and firewall rules first. Mismatched chunk sizes between encoder and server cause corrupted or stalled streams; ensure your media server honors chunk size negotiation rather than assuming a fixed value. Firewall blocks on corporate networks often require RTMPT or a different egress strategy. Latency spikes typically trace to encoder buffering, oversized keyframe intervals, or network congestion on the TCP path; reduce buffer settings and stabilize bitrate before blaming the protocol.
RTMP vs Modern Streaming Protocols
RTMP is no longer the right tool for every layer of a streaming stack, and honest engineering requires knowing where it wins and loses. The comparison that matters most for developers is RTMP vs HLS, because that pairing covers the ingest-versus-playback split that defines modern architectures.
HLS segments media into small files delivered over HTTP, which scales effortlessly through CDNs and plays natively in every browser. The cost is latency: standard HLS buffers several segments, adding 15 to 30 seconds of delay. Low-Latency HLS narrows that gap but adds complexity. DASH is functionally similar to HLS with an open standard and flexible codec support. SRT, by contrast, competes with RTMP directly on ingest: it runs over UDP with ARQ-based recovery, surviving packet loss far better than TCP-based RTMP on unreliable networks, at the cost of broader encoder support.
RTMP's strengths remain real: universal encoder support, low latency over a persistent connection, and a simple push model. Its weaknesses are equally real: no native browser playback, TCP head-of-line blocking, and a legacy codec ceiling that complicates modern formats.
| Dimension | RTMP | HLS | DASH | SRT |
|---|---|---|---|---|
| Transport | TCP, persistent | HTTP, segmented | HTTP, segmented | UDP with recovery |
| Typical latency | 2-5 seconds | 15-30 seconds | 15-30 seconds | 0.5-2 seconds |
| Browser playback | No plugin-free support | Native everywhere | Native in most browsers | No native support |
| Scalability | Moderate, server-bound | Excellent via CDN | Excellent via CDN | Moderate, point-to-point |
| Best for | Live ingest and contribution | Mass viewer distribution | Mass distribution, open standard | Unreliable networks, contribution |
The most important row is latency versus scalability: RTMP and SRT win the first mile, HLS and DASH win the last mile, and mature pipelines use both categories together.
When to Choose RTMP Protocol
Choose RTMP when you are solving the contribution problem: getting a live feed from an encoder to a server reliably and with low latency. This covers live ingest into a media server, multi-platform simulcasting where a single broadcast is forwarded to YouTube, Twitch, and Facebook simultaneously, and legacy workflows where RTMP support is already baked into existing hardware and software.
RTMP is also the pragmatic choice when encoder compatibility is the constraint. Every serious encoding tool speaks RTMP, while SRT and RIST support, though growing, is not yet universal. If your broadcasters use consumer tools like OBS, RTMP is the path of least resistance.
Do not choose RTMP for viewer-facing playback in 2026. Browsers do not play it natively, and HTTP-based protocols scale better for large audiences. The correct architecture is RTMP (or SRT) for ingest, HLS or DASH for distribution, and a real-time protocol like WebRTC when in-app viewers need true sub-second interactivity, which is exactly the model VideoSDK's interactive live streaming uses.
Future Outlook for RTMP
RTMP's future is as an ingest standard, not a playback one. Platform behavior confirms this: major destinations require or prefer RTMPS, encoders continue to add it as the default, and the ecosystem treats plain RTMP as legacy. The Enhanced RTMP initiative, backed by several major streaming companies, extends the protocol with modern codecs and richer signaling, signaling that the industry intends to keep the first mile on RTMP rather than replace it wholesale.
Alternatives are maturing at the edges. SRT and RIST are winning contribution traffic on unreliable networks, and WebRTC-based ingest is emerging for real-time workflows. But none of them matches RTMP's installed base. For the foreseeable future, a developer building live infrastructure needs RTMP fluency, and the safest bet is to design ingest endpoints that accept RTMPS today and remain open to SRT tomorrow.
Definitions Glossary
RTMP Protocol: A TCP-based protocol for transporting audio, video, and command messages over a persistent connection, primarily used for live stream ingest into media servers and streaming CDNs.
RTMP Handshake: The three-phase packet exchange (C0/C1/C2 from the client, S0/S1/S2 from the server) that verifies both peers are live before media flows.
Chunk Stream: The RTMP mechanism that splits large messages into smaller chunks and multiplexes multiple logical streams over one TCP connection.
RTMPS: RTMP wrapped in TLS encryption, protecting stream keys and media payloads from interception during ingest.
RTMP Output: A feature of streaming platforms, including VideoSDK's interactive live streaming, that forwards a live session to external destinations like YouTube and Twitch via RTMP.
Key Takeaways
- The RTMP protocol remains the dominant standard for live ingest, carrying encoder output to media servers and streaming CDNs over a persistent TCP connection with two to five seconds of latency.
- The three-phase RTMP handshake verifies both peers through echoed random data, and most handshake failures trace to blocked ports or TLS mismatches on RTMPS endpoints.
- Chunk stream architecture, including the four chunk header types, lets RTMP interleave audio and video efficiently while minimizing per-chunk overhead.
- Use RTMPS for production ingest, keep RTMPT only as a firewall-traversal fallback, and never rely on plain RTMP for credentials or sensitive content.
- The correct modern architecture pairs RTMP or SRT for ingest with HLS or DASH for distribution, and WebRTC-based solutions like VideoSDK's interactive live streaming for sub-second in-app interactivity.
Conclusion
The RTMP protocol has outlived the platform it was built for because it solves one problem exceptionally well: reliable, low-latency live contribution from encoder to server. Developers building streaming pipelines in 2026 need to understand its handshake, chunk streams, and security variants, and just as importantly, know when to hand off to HLS, DASH, or WebRTC for playback. If you are building live streaming into your application, explore VideoSDK's interactive live streaming, which combines sub-second in-app latency with RTMP output for simultaneous multi-platform broadcasting. Sign up free at app.videosdk.live and check the code samples to get started. What are you building with live streaming? Drop a comment, I'd love to hear what kind of ingest pipeline you're working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ