


A WebRTC leak occurs when the WebRTC protocol in your browser exposes your real IP address to remote peers, even when you are connected to a VPN or proxy. This happens because WebRTC uses its own UDP sockets to gather network paths via STUN servers, bypassing encrypted VPN tunnels. You can prevent these leaks by disabling WebRTC in your browser, using specialized privacy extensions, or deploying network-level firewall rules.
WebRTC is a powerful technology that enables real-time video and audio communication directly in the browser. However, it introduces a significant privacy vulnerability known as the WebRTC leak. If you are building applications with real-time communication or simply value your digital privacy, understanding this flaw is critical. This article breaks down the technical mechanics of WebRTC leaks, why your VPN might not save you, and how to test for and mitigate these exposures effectively.
What Is a WebRTC Leak?
A WebRTC leak is the unintended exposure of a user's real IP addresses during the WebRTC connection process. WebRTC relies on a mechanism called Interactive Connectivity Establishment (ICE) to find the most efficient path between two peers. To do this, it asks your operating system for all available network interfaces and their associated IP addresses.
When a leak occurs, the browser exposes this information to the remote peer or a malicious website. There are several types of data that can be exposed. A local IP leak reveals your internal network address, such as a 192.168.x.x address. A public IP leak exposes your actual internet-facing IP address, defeating the purpose of a VPN. An IPv6 leak occurs when the IPv4 traffic is routed through a VPN but the IPv6 traffic is not, exposing your real IPv6 address. Finally, an mDNS leak happens when the browser broadcasts your local machine's hostname via Multicast DNS, which can sometimes be resolved into a local IP address.
How WebRTC Works Under the Hood
To understand why WebRTC leaks happen, you need to look at how the protocol establishes peer-to-peer connections. WebRTC does not route media through a central server by default. Instead, it tries to connect clients directly to each other.
ICE (Interactive Connectivity Establishment)
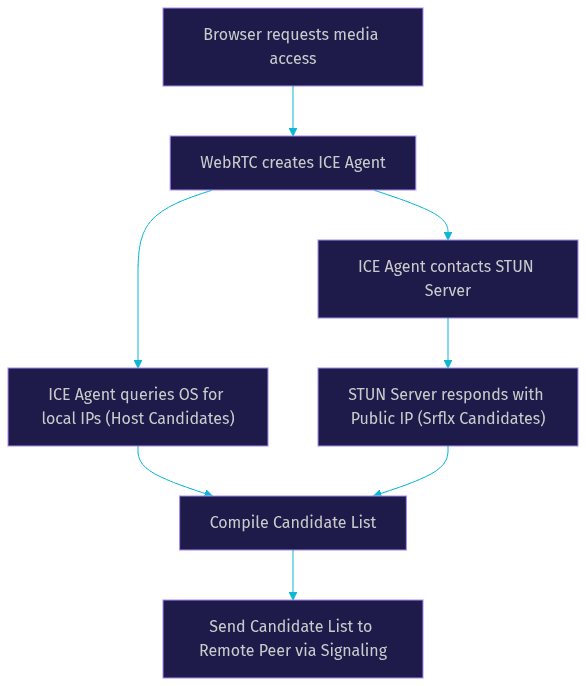
ICE is the framework used by WebRTC to connect two peers. It gathers all possible network paths, called candidates, and tests them to find the one with the lowest latency. The ICE agent inside the browser queries the operating system for local network interfaces and also contacts external servers to discover public addresses.
STUN and TURN Servers
STUN (Session Traversal Utilities for NAT) servers help a browser discover its public IP address and the type of NAT it is behind. The browser sends a request to a STUN server, and the server replies with the IP address it sees. This is how the browser learns its public-facing IP. TURN (Traversal Using Relays around NAT) servers act as relays when a direct peer-to-peer connection fails, routing media through a server to ensure connectivity.
Candidate Types (host, srflx, prflx, relay)
ICE gathers four main types of candidates. Host candidates are your local network interfaces, exposing your local IP. Server reflexive (srflx) candidates are your public IP addresses as seen by the STUN server. Peer reflexive (prflx) candidates are addresses discovered during the connection process. Relay candidates are addresses on a TURN server. The host and srflx candidates are the primary sources of WebRTC leaks.
Why Leaks Occur Even With a VPN or Proxy
You might assume that turning on a VPN encrypts all traffic and hides your IP address. For most web traffic over TCP, this is true. WebRTC, however, is built for low-latency real-time communication and primarily uses UDP.
When a browser initiates a WebRTC connection, the ICE agent creates its own UDP sockets to gather candidates. Depending on the operating system and the VPN client, these UDP packets might bypass the VPN tunnel entirely and go out through the default physical network interface. This means the STUN server sees your real ISP-assigned IP address, not the VPN server's IP.
Proxies fare even worse. Standard HTTP proxies only handle HTTP and HTTPS traffic. SOCKS5 proxies can handle UDP, but browsers often do not route WebRTC UDP traffic through SOCKS5 proxies by default. The operating system's network stack simply routes the WebRTC UDP packets out of the most direct available interface, resulting in a leak.
Types of Data Exposed by a WebRTC Leak
A WebRTC leak is not just about your public IP. The ICE gathering process can expose multiple layers of your network topology.
Local LAN IP (host)
The host candidate reveals your local network IP address, such as 192.168.1.5. While this does not expose your location to the outside world, it reveals your internal network structure. An attacker can use this to map your local network or identify other devices.
Public IP (srflx)
The server reflexive candidate exposes your true public IP address. This is the most dangerous leak for privacy-conscious users. It completely bypasses your VPN and reveals your approximate geographic location and your ISP to any website running a WebRTC leak test.
IPv6 Address
Many VPNs only tunnel IPv4 traffic. If your ISP assigns you an IPv6 address and your browser supports it, WebRTC might gather an IPv6 srflx candidate. This leaks your real IPv6 address, which is often tied directly to your physical location and ISP.
mDNS Hostname
Modern browsers try to obscure local IPs by using mDNS (Multicast DNS) hostnames instead of raw IP addresses. However, a sophisticated remote peer can sometimes resolve these mDNS hostnames back to a local IP address, or use the hostname itself as a unique browser fingerprinting vector.
Browser-Specific Leak Risk
Different browsers handle WebRTC and mDNS obfuscation differently. If you are building a real-time communication app using a platform like VideoSDK, you control the ICE configuration. But for general web browsing, the browser's default settings dictate your risk level.
| Browser | Default Leak Risk | Built-in Mitigation Options |
|---|---|---|
| Chrome | High | mDNS obfuscation enabled by default, but public IP still leaks. Can disable WebRTC via flags. |
| Edge | High | Similar to Chrome. mDNS obfuscation present. |
| Firefox | Medium | Can disable WebRTC entirely in about:config. mDNS obfuscation supported. |
| Safari | Medium | Apple restricts ICE candidate gathering, offering some protection. No simple toggle to disable WebRTC. |
| Brave | Low | Ships with built-in WebRTC IP handling policy set to restrict non-proxied UDP. |
| Opera | High | Based on Chromium, behaves like Chrome. Includes a built-in VPN but it does not prevent WebRTC leaks by default. |
| Vivaldi | High | Chromium-based. Relies on mDNS obfuscation. |
Testing for a WebRTC Leak
If you use a VPN or proxy, you should regularly test for WebRTC leaks. Testing is straightforward and involves visiting a website that runs a local WebRTC session to see what IP addresses your browser exposes.
Popular Online Leak Test Tools
Several reputable tools can detect WebRTC leaks. BrowserLeaks.io offers a comprehensive WebRTC test that shows your local IPs, public IPs, and the exact ICE candidates your browser generates. Whoer.net provides a quick IP leak test that checks for WebRTC exposure alongside DNS and proxy leaks. PrivacyTools.io also lists various leak testing utilities that are frequently updated.
Interpreting Test Results
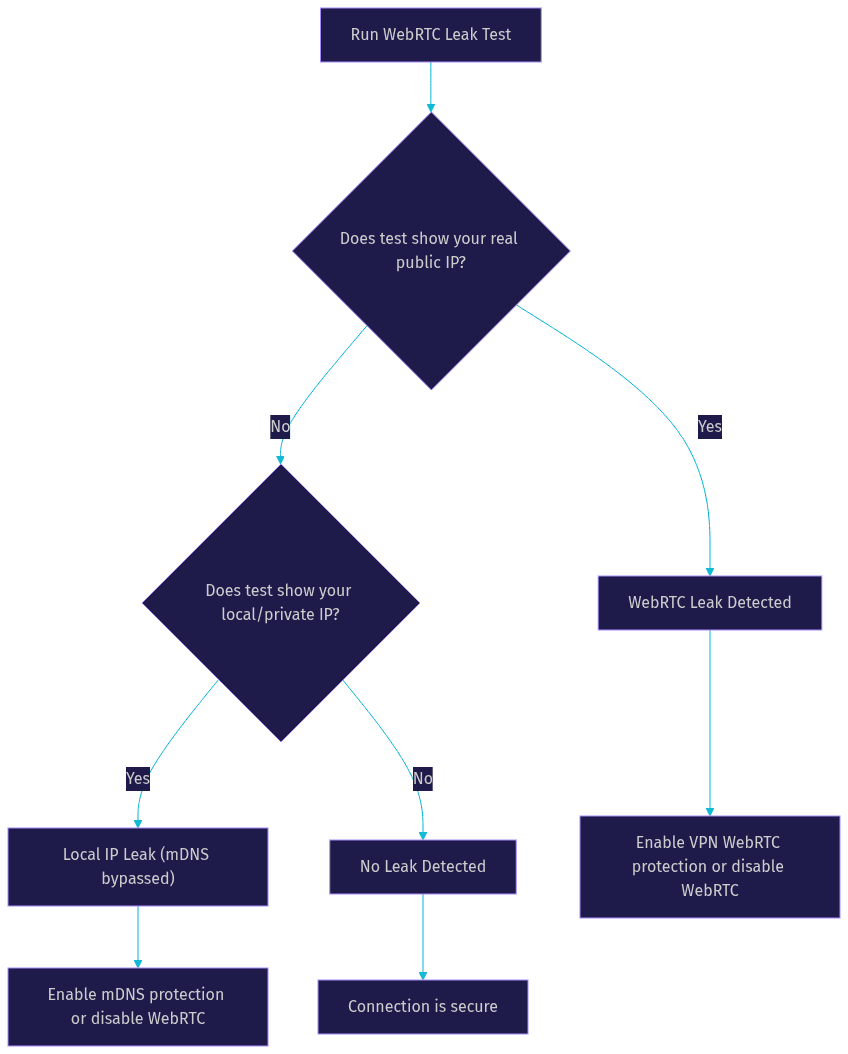
When you run a test, compare the IP addresses shown against your VPN IP address. If the test shows your real ISP IP address under the public IP section, you have a severe WebRTC leak. If it shows a 192.168.x.x address or an mDNS hostname, your local IP is exposed. If your real IP does not appear and only the VPN IP is visible, your setup is secure.
Mitigation Strategies
Preventing WebRTC leaks requires a multi-layered approach. You can adjust browser settings, install extensions, or enforce network-level rules.
Native Browser Settings
In Firefox, you can disable WebRTC entirely by navigating to the advanced configuration settings and modifying the media peerconnection preference. In Chrome and other Chromium-based browsers, you can disable WebRTC by toggling specific experimental flags, though these can reset after browser updates. Safari does not offer a simple toggle, relying instead on its internal restrictions.
Trusted Extensions
If you need WebRTC for legitimate use but want to prevent leaks, privacy extensions are the best solution. uBlock Origin includes a setting to prevent WebRTC from leaking local IP addresses. Extensions like WebRTC Leak Prevent and WebRTC Control force the browser to use only the default route, which is usually the VPN interface, effectively stopping public IP leaks.
Network-Level Blocking
For comprehensive protection, you can block WebRTC traffic at the network level. Configuring your firewall to block outbound UDP traffic on port 3478, which is commonly used by STUN servers, will prevent the browser from discovering its public IP. Additionally, using a VPN client that forces all traffic, including UDP, through the tunnel interface will mitigate most leaks.
Disabling WebRTC Completely
For high-privacy scenarios where you do not need real-time communication features, disabling WebRTC entirely is the safest option. This can be done through browser policies, extensions, or configuration settings. This ensures no ICE candidates are ever generated.
Advanced Mitigation
For developers and enterprise administrators, more granular control over WebRTC behavior is necessary.
Using TURN-Only Configurations
If you are developing a WebRTC application, you can configure the ICE servers to use only TURN candidates. By not providing STUN servers, the browser will not discover its public IP. All media traffic is routed through the TURN server, hiding the user's real IP from the peer. Managed RTC platforms like VideoSDK handle this secure routing automatically, ensuring that media streams are protected without exposing raw ICE candidates to the public internet.
Custom VPN Clients with Interface Binding
Some advanced VPN clients allow you to bind applications to specific network interfaces. By forcing the browser to only use the virtual network interface created by the VPN, you ensure that WebRTC UDP packets cannot escape through the physical interface. This requires a VPN client that supports split-tunneling and interface binding.
Enterprise Policies
In corporate environments, IT administrators can use Group Policy Objects (GPO) or Mobile Device Management (MDM) solutions to enforce WebRTC restrictions across all managed browsers. This ensures that employees do not accidentally leak internal corporate IP addresses when using external communication tools.
Impact on Privacy and Security
The impact of a WebRTC leak extends beyond simply knowing your IP address. Your IP address is a unique identifier that can be used for browser fingerprinting. When combined with other browser attributes, it creates a highly unique tracking profile.
Leaked IP addresses enable location tracking down to the city or neighborhood level. This undermines the anonymity provided by VPNs and proxies. In targeted attacks, knowing a user's real public IP allows an attacker to launch direct network attacks, such as DDoS, or attempt to exploit vulnerabilities in their home router. Recent statistics on privacy tools show that a significant percentage of VPN users still experience WebRTC leaks due to misconfigured clients or browser defaults, highlighting the ongoing relevance of this vulnerability.
Best-Practice Checklist
To verify and protect against WebRTC leaks, follow these steps:
- Test regularly: Use tools like BrowserLeaks.io to check for IP exposure while your VPN is active.
- Install a privacy extension: Use uBlock Origin or a dedicated WebRTC control extension to restrict ICE candidate gathering.
- Check browser settings: Ensure mDNS obfuscation is enabled in your browser to protect your local IP.
- Use a secure VPN: Choose a VPN provider that offers WebRTC leak protection or forces UDP traffic through the tunnel.
- Disable WebRTC if unused: If you do not use browser-based video calling, disable the WebRTC API entirely in your browser configuration.
Definitions Glossary
ICE (Interactive Connectivity Establishment): A protocol used by WebRTC to find the best path between two peers by gathering network candidates.
STUN (Session Traversal Utilities for NAT): A protocol that helps a device discover its public IP address and NAT type by communicating with an external server.
TURN (Traversal Using Relays around NAT): A protocol that relays WebRTC traffic through a server when a direct peer-to-peer connection fails.
mDNS (Multicast DNS): A protocol used by browsers to resolve hostnames on a local network without a dedicated DNS server, often used to obscure local IP addresses in WebRTC.
Host Candidate: An ICE candidate representing a local network interface IP address.
Key Takeaways
- A WebRTC leak exposes your real local and public IP addresses by bypassing VPN tunnels using direct UDP socket connections to STUN servers.
- Browsers like Chrome and Edge have a high default leak risk, while privacy-focused browsers like Brave offer built-in mitigation.
- Testing for leaks is simple using online tools like BrowserLeaks.io, which display the exact ICE candidates your browser generates.
- Mitigation requires a combination of browser settings, privacy extensions, and network-level firewall rules to effectively block UDP leaks.
- Developers building RTC applications should use managed platforms like VideoSDK to ensure secure media routing and proper TURN configurations without exposing user IPs.
Conclusion
WebRTC leaks remain a persistent privacy vulnerability for anyone relying on VPNs or proxies for anonymity. By understanding how ICE gathers candidates and why UDP bypasses encrypted tunnels, you can take informed steps to protect your real IP address. Regular testing with reputable tools and implementing robust mitigation strategies are essential for maintaining privacy. If you are a developer building real-time communication features, consider using a secure, managed SDK like VideoSDK to abstract away the complexities of ICE configuration and ensure your users' IP addresses remain protected. What are you building with WebRTC? Drop a comment and let me know how you handle privacy in your real-time applications.
FAQ