


ExpressVPN blocks most WebRTC leaks by routing STUN traffic through its VPN tunnel and enabling the Network Lock kill-switch by default. However, the protection depends on using the desktop client, keeping the app updated, and disabling browser extensions that bypass the tunnel. Test your setup with a WebRTC leak checker to confirm.
WebRTC leaks remain one of the most overlooked privacy vulnerabilities in 2026. Even when a VPN tunnel is active and your traffic appears encrypted, a browser feature called WebRTC can quietly expose your real public IP address to any website running a few lines of JavaScript. ExpressVPN has built a strong reputation for leak protection, but does ExpressVPN block WebRTC reliably across all scenarios? That question matters for developers, remote workers, journalists, and anyone whose privacy depends on their VPN actually working at every layer of the network stack.
This article breaks down what WebRTC leaks are, how ExpressVPN handles them, where its protection has gaps, and how you can test and strengthen your own setup. By the end, you will know exactly what ExpressVPN does under the hood, how to verify it with real testing tools, and what additional browser hardening steps are worth taking.
What is WebRTC and How It Can Leak IP Addresses?
Understanding WebRTC
WebRTC (Web Real-Time Communication) is an open-source project and browser API that enables peer-to-peer audio, video, and data streaming without plugins. Browsers like Chrome, Firefox, Edge, and Safari ship with WebRTC enabled by default because it powers features like Google Meet, Discord web, and in-browser screen sharing. To establish a direct peer connection, WebRTC uses a framework called ICE (Interactive Connectivity Establishment), which relies on STUN (Session Traversal Utilities for NAT) and TURN (Traversal Using Relays around NAT) servers to discover the public IP addresses of each participant.
The problem is that this IP discovery process happens inside the browser, at the application layer, and it can bypass network-layer VPN tunnels entirely. When a browser gathers ICE candidates, it queries STUN servers to find all reachable IP addresses, including your real public IP assigned by your ISP and even local network IPs. Any website with JavaScript access can trigger this process without your knowledge or consent.
How WebRTC Leaks Occur
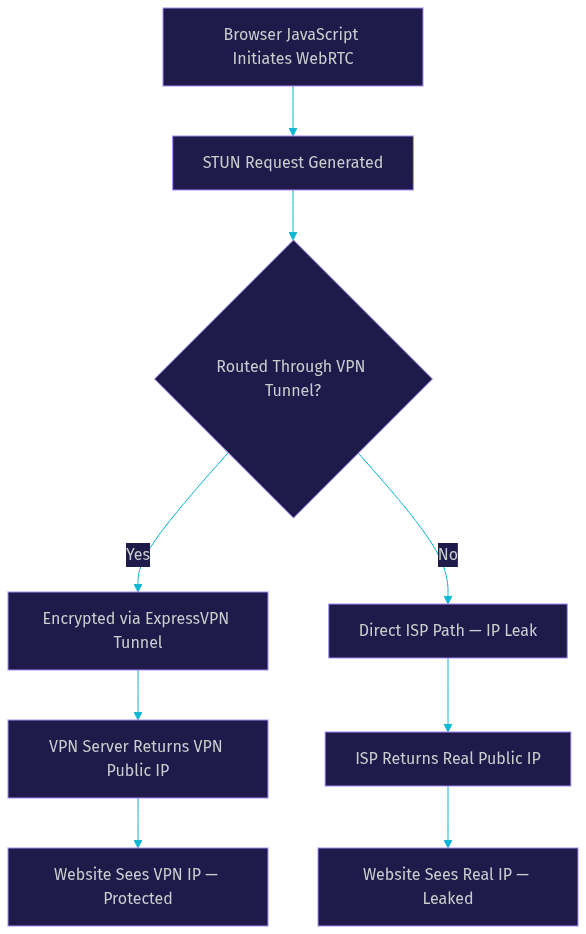
A WebRTC leak happens when a website uses JavaScript to initiate a STUN request through the browser's WebRTC API. The browser dutifully collects all ICE candidates, which include your true public IP address, and makes them available to the requesting script. Because this request originates from the browser application itself and may use a different network path than your VPN tunnel, the STUN traffic can travel directly through your ISP rather than through the encrypted VPN connection.
This means the leak operates at the application layer, not the network layer. Your VPN encrypts traffic at the network level, but the browser's WebRTC implementation can create a separate communication channel that sidesteps that encryption. The result is that a website can learn your real IP address even while your VPN is connected and functioning perfectly for all other traffic. This is why WebRTC leaks are particularly insidious: they do not indicate a VPN failure, but rather a gap in how browsers and VPNs interact.
Does ExpressVPN Block WebRTC Leaks?
Built-in Leak-Protection Features
ExpressVPN addresses WebRTC leaks through several mechanisms built into its desktop and mobile clients. The most important is Network Lock, ExpressVPN's implementation of a kill switch. When Network Lock is enabled, all internet traffic is blocked if the VPN connection drops unexpectedly, preventing your real IP from being exposed during reconnection. Network Lock is enabled by default in the ExpressVPN desktop apps for Windows, Mac, and Linux, which means most users have this protection active without needing to configure anything manually.
Beyond Network Lock, ExpressVPN routes STUN traffic through the VPN tunnel when the desktop client is active. This means that when your browser initiates a WebRTC ICE candidate gathering process, the STUN requests travel through the encrypted VPN connection rather than directly through your ISP. The VPN server's IP address is what gets returned as the public IP, not your real one. ExpressVPN also operates private, encrypted DNS servers, which prevents DNS leaks that could otherwise reveal your browsing activity or real location. You can verify your own setup using ExpressVPN's official leak test page, which checks for WebRTC, DNS, and IP leaks in a single scan.
Limitations and Known Gaps
Despite these protections, ExpressVPN's WebRTC blocking is not absolute in every scenario. Browser extensions that proxy traffic independently of the VPN client can create alternative paths for STUN requests, potentially bypassing the tunnel. Split-tunneling configurations, where certain apps or traffic types are excluded from the VPN, can also leave WebRTC traffic unencrypted if the browser is included in the split-tunnel exclusion list. Additionally, outdated versions of the ExpressVPN client may lack the latest STUN routing improvements, so running an older build can leave you vulnerable even if the current version would protect you.
Testing Whether ExpressVPN Blocks WebRTC
Manual Browser Test Steps
Testing your ExpressVPN setup for WebRTC leaks is straightforward and should be done whenever you install the client, update to a new version, or change network environments. The process involves comparing your exposed IP addresses before and after connecting to the VPN.
First, disconnect from ExpressVPN entirely. Open your browser and visit a WebRTC leak testing site such as the ExpressVPN leak test tool or an independent checker like BrowserLeaks. Note every IP address the tool reports, including both your public IP and any local network IPs. These are your baseline, unencrypted addresses.
Next, connect to an ExpressVPN server in your preferred location. Wait for the connection to fully establish, then refresh the leak test page or open it in a new tab. Compare the reported IP addresses against your baseline. If the tool now shows only the VPN server's IP address and none of your original public or local IPs, your WebRTC traffic is being routed through the tunnel correctly. If you see your real public IP alongside or instead of the VPN IP, you have an active WebRTC leak that needs attention.
Run this test in every browser you use regularly, since WebRTC behavior can differ between Chrome, Firefox, Edge, and Safari. Also test with any browser extensions enabled and disabled, as some extensions can interfere with STUN routing.
Automated Testing Tools
For developers and power users who want more rigorous leak detection, several automated tools go beyond simple browser-based checkers. Online services like MyIPScan and IPLeak.net run comprehensive tests that cover WebRTC, DNS, and IPv6 leaks simultaneously, providing a broader privacy audit in a single visit.
For those comfortable with network analysis, open-source tools can capture and inspect STUN traffic at the packet level. Network monitoring utilities can filter for UDP traffic on standard STUN ports (typically port 3478) and reveal whether those packets are traveling through the VPN tunnel interface or directly through your default network interface. This approach gives you definitive proof of which network path WebRTC traffic is taking, rather than relying on a web-based tool's interpretation.
When using automated tools, always test in a controlled environment. Close other applications that might generate network traffic, disable unnecessary browser extensions, and run the test multiple times to rule out transient network conditions. Document your results so you can compare them after any configuration change or software update.
Enhancing WebRTC Leak Protection
Browser Settings and Extensions
Even with ExpressVPN's built-in protections, adding browser-level WebRTC hardening provides defense in depth. Each major browser handles WebRTC differently, and knowing how to control it gives you an extra layer of security that does not depend on the VPN client alone.
In Firefox, you can disable WebRTC entirely by navigating to the browser's advanced configuration settings and modifying the media peerconnection preference. Firefox is the most cooperative browser for WebRTC control because it exposes this setting directly without requiring extensions. In Chrome and Edge, WebRTC cannot be fully disabled through standard settings, but you can use reputable extensions that restrict ICE candidate gathering to prevent local IP exposure. Extensions like WebRTC Control or WebRTC Leak Prevent override the browser's default behavior and limit what IP addresses WebRTC can access. In Safari, WebRTC can be disabled through the Developer menu if you have enabled developer features in Safari's preferences.
The key principle is to disable or restrict WebRTC in any browser you use for privacy-sensitive activities, and reserve a separate browser profile with WebRTC enabled only for applications that genuinely need it, like video conferencing platforms.
Using Network Lock and Kill Switch
Network Lock is ExpressVPN's kill switch, and verifying its configuration is essential for comprehensive leak protection. When enabled, Network Lock monitors the VPN connection and blocks all internet traffic if the connection drops, ensuring that no packets, including WebRTC STUN requests, can escape through your ISP's network.
To confirm Network Lock is active, open the ExpressVPN app and check the settings panel. Network Lock should be toggled on, and you should verify that it covers all relevant protocols, including IPv4, IPv6, and DNS traffic. Some older configurations only protected IPv4, leaving IPv6 traffic exposed, so confirming full protocol coverage is important in 2026 as more networks adopt IPv6.
After enabling or modifying Network Lock settings, test its effectiveness by manually disconnecting from the VPN while monitoring a leak test page. If Network Lock is working correctly, all traffic should halt immediately upon disconnection, and no IP addresses should be visible to the testing tool. If you see traffic flowing after disconnection, review your Network Lock settings and ensure no split-tunneling rules are overriding the kill switch.
Comparing ExpressVPN to Other VPNs for WebRTC
Not all VPN providers handle WebRTC leaks with the same rigor. The table below compares ExpressVPN against three popular alternatives, focusing on WebRTC leak handling, kill switch availability, and default browser extension support.
| VPN Provider | WebRTC Leak Handling | Kill Switch Name | Kill Switch Default | Browser Extension WebRTC Protection |
|---|---|---|---|---|
| ExpressVPN | Routes STUN through VPN tunnel | Network Lock | Enabled by default | Limited (routes through tunnel) |
| NordVPN | Routes STUN through VPN tunnel | Kill Switch | Enabled by default | Limited (routes through tunnel) |
| Surfshark | Routes STUN through VPN tunnel | KillSwitch | Manual enable | No native WebRTC blocking |
| ProtonVPN | Routes STUN through VPN tunnel | Kill Switch | Enabled by default | Limited (routes through tunnel) |
ExpressVPN and NordVPN stand out for having kill switches enabled by default, which means users get critical leak protection without needing to dig into settings. Surfshark requires manual kill switch activation, which creates a window of vulnerability for users who skip configuration. ProtonVPN matches ExpressVPN and NordVPN with default kill switch protection. None of these providers offer full browser-level WebRTC blocking through their extensions, which is why combining the VPN client with browser hardening remains the most reliable approach.
The following diagram illustrates how WebRTC traffic flows depending on whether it is routed through the VPN tunnel or bypasses it:
Best Practices for Developers and Users
Maintaining robust WebRTC leak protection requires ongoing vigilance rather than a one-time setup. The following practices should become part of your regular privacy hygiene routine.
Keep your ExpressVPN client updated to the latest version. ExpressVPN regularly improves its STUN routing and leak protection mechanisms, and running an outdated client means you may miss critical security patches. Enable automatic updates if the option is available, and check for updates manually at least once a month.
Always use the full desktop or mobile ExpressVPN application rather than relying solely on browser extensions. The desktop client operates at the system level, routing all traffic through the VPN tunnel, while browser extensions only proxy browser traffic and may not handle WebRTC STUN requests consistently. The desktop app is the foundation of your leak protection.
Disable WebRTC in browsers when engaging in privacy-critical activities. If you are researching sensitive topics, communicating as a source, or accessing services where your IP must remain hidden, turn off WebRTC at the browser level as an additional safeguard. Use a separate browser profile with WebRTC enabled only when you need video conferencing or other WebRTC-dependent applications.
Run leak tests regularly, especially after updating your VPN client, changing browsers, installing new extensions, or switching network environments. A quick test takes under a minute and can reveal configuration issues before they become privacy incidents. Treat leak testing as a habit, not a one-time check.
Finally, audit your browser extensions periodically. Some extensions, particularly proxy or privacy tools, can interfere with VPN tunnel routing or create alternative network paths that bypass ExpressVPN's protections. Remove extensions you no longer use, and test your leak status after installing any new extension.
Definitions Glossary
WebRTC: An open browser API that enables peer-to-peer audio, video, and data communication without plugins. WebRTC uses STUN and TURN servers to discover public IP addresses for establishing direct connections, which can expose real IPs even when a VPN is active.
STUN (Session Traversal Utilities for NAT): A protocol used by WebRTC to discover the public IP address of a device behind a NAT router. STUN requests can bypass VPN tunnels if not properly routed, causing IP leaks.
ICE (Interactive Connectivity Establishment): A framework used by WebRTC to find the best network path between two peers. ICE candidate gathering collects all reachable IP addresses, including local and public addresses, which is the mechanism behind WebRTC leaks.
Network Lock: ExpressVPN's implementation of a kill switch. When enabled, Network Lock blocks all internet traffic if the VPN connection drops, preventing real IP addresses from being exposed during reconnection or disconnection.
Split Tunneling: A VPN feature that allows specific apps or traffic types to bypass the VPN tunnel and connect directly through the ISP. Split tunneling can inadvertently expose WebRTC traffic if the browser is excluded from the tunnel.
Key Takeaways
- ExpressVPN blocks most WebRTC leaks by routing STUN traffic through its VPN tunnel and enabling Network Lock by default on desktop clients.
- WebRTC leaks occur at the application layer, meaning they can bypass network-layer VPN encryption if the browser's STUN requests are not properly routed.
- Browser extensions, split-tunneling configurations, and outdated client versions are the most common causes of WebRTC leaks even when ExpressVPN is connected.
- Combining ExpressVPN's desktop client with browser-level WebRTC disabling provides the strongest protection against IP leaks.
- Regular leak testing using tools like ExpressVPN's leak test page, BrowserLeaks, or IPLeak.net is essential for verifying that your protection remains effective over time.
Conclusion
ExpressVPN generally blocks WebRTC leaks effectively when you use the desktop client, keep it updated, and leave Network Lock enabled. The combination of STUN routing through the VPN tunnel and a default kill switch covers the most common leak vectors. However, no VPN client alone can guarantee complete WebRTC protection in every scenario, especially when browser extensions or split-tunneling rules create alternative network paths. Adding browser-level WebRTC hardening and running periodic leak tests transforms good protection into reliable protection. If you are working on real-time communication features in your own applications and want to understand how WebRTC interacts with network infrastructure, explore the VideoSDK documentation for developer-focused WebRTC resources. What are your results from testing ExpressVPN's WebRTC protection? Drop a comment and share which browser and configuration you tested.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ