


SIP TLS is the practice of running Session Initiation Protocol signaling over Transport Layer Security, encrypting every hop of your call setup traffic on port 5061. It protects registration data, credentials, and phone numbers from eavesdropping and tampering in ways plain SIP over UDP or TCP cannot. VideoSDK applies the same TLS-protected signaling principles in its telephony and SIP integration, bridging secure SIP trunks into WebRTC rooms. This guide covers the handshake, certificates, configuration, and troubleshooting you need to deploy SIP TLS correctly.
Every time a phone registers, places a call, or joins a conference, SIP messages carry usernames, authentication digests, and dialed numbers across the network. On unsecured transports, anyone on the path can read and modify that traffic. In 2026, with carriers, regulators, and enterprise security teams all tightening requirements, running SIP signaling in the clear is no longer defensible. SIP TLS is the standard answer, defined in RFC 3261 and hardened by a decade of TLS evolution.
By the end of this article you will understand what SIP TLS actually protects, how the TLS handshake and certificate chain work, how to enable SIP TLS on OpenSIPS, Asterisk, and FreeSWITCH, and how to keep certificates healthy in production.
What Is SIP TLS?
SIP TLS is defined as the transport of SIP signaling messages inside a TLS-encrypted connection, typically on port 5061, as specified in RFC 3261. SIP itself is transport-agnostic: the protocol runs happily over UDP, TCP, TLS, or WebSocket. The choice of transport determines whether your signaling is readable by third parties.
SIP TLS works by establishing a TLS session between two SIP endpoints, such as a softphone and a proxy server, before any SIP message is exchanged. Once the session is up, every SIP request and response, from INVITE to BYE, travels inside the encrypted tunnel. An observer on the wire sees only encrypted bytes, the peer identities, and connection metadata.
The critical concept is hop-by-hop encryption. SIP TLS protects the connection between two adjacent SIP nodes, not the entire end-to-end path. If a call traverses your phone, your local proxy, a carrier SBC, and the destination PBX, each leg needs its own TLS session. This differs from media encryption like SRTP, which protects the voice stream itself. A complete security posture uses SIP TLS for signaling and SRTP for media, and that pairing is what standards like SIP-TLS deployments in enterprise and carrier networks aim for.
Compared with plain SIP over UDP or TCP, SIP TLS adds confidentiality, integrity, and peer authentication. Plain SIP over UDP offers none of these: digest authentication protects credentials from replay but the rest of the message, including headers and routing data, is visible and modifiable.
Why Use SIP TLS?
The case for SIP TLS rests on three concrete protections. First, confidentiality: without TLS, SIP registration traffic exposes usernames, realm data, and digest hashes that support offline password-cracking attempts. Second, integrity: TLS guarantees that an attacker cannot silently rewrite routing headers, redirect calls, or inject fake responses mid-dialog. Third, authentication: the TLS certificate proves the server you are sending credentials to is actually yours, which blocks man-in-the-middle interception of trunk registrations.
Compliance is the second driver. Regulations and frameworks including GDPR, HIPAA for healthcare telephony, and PCI DSS for contact centers handling card payments all push toward encrypted signaling wherever personal or financial data crosses the network. Carriers increasingly require TLS on SIP interconnects, and many enterprise procurement checklists now list SIP TLS as a mandatory line item rather than an option.
There is a performance cost, but it is smaller than most teams expect. TLS adds handshake latency when a connection is established and modest CPU overhead for encryption. TLS 1.3 reduces the handshake to a single round trip, and session resumption keeps long-lived SIP connections cheap. For a proxy handling thousands of registrations, the overhead is measurable but manageable with modern hardware and cipher acceleration.
TLS Handshake and Certificate Basics for SIP TLS
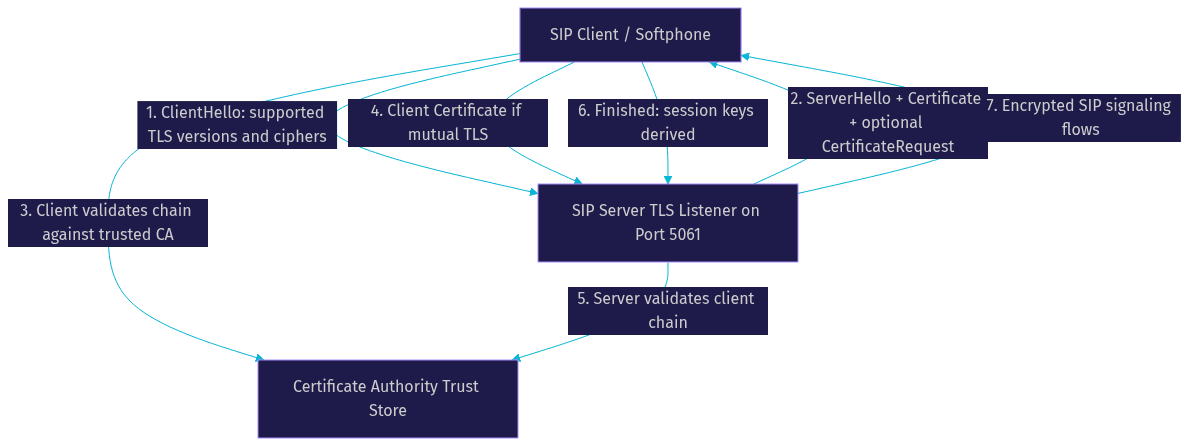
The SIP TLS handshake follows the standard TLS handshake, initiated when a SIP client opens a connection to the server's TLS listener on port 5061. The client proposes a protocol version and a list of supported cipher suites. The server picks a version and cipher, presents its certificate, and, if mutual authentication is configured, requests a certificate from the client as well. Both sides derive session keys, confirm the handshake, and only then does the first SIP message flow.
Certificates are the identity layer of SIP TLS. A server certificate binds a domain name or hostname to a public key, and it is issued by a Certificate Authority whose own certificate sits in the trust store of the connecting client. When your SIP phone connects to your proxy, it validates three things: that the certificate chain resolves to a trusted CA, that the hostname in the SIP URI matches the name on the certificate, and that the certificate is within its validity period and not revoked.
Mutual authentication, often called mTLS, extends this in both directions. The server also demands and validates a client certificate, so both parties prove identity cryptographically. For carrier interconnects and high-value trunk links, mutual SIP TLS authentication is the recommended baseline because it eliminates spoofed endpoint registrations entirely.
Certificate Types and Formats for SIP TLS
SIP TLS deployments encounter two certificate encodings: PEM, a base64 text format used by nearly all open-source SIP servers, and DER, a binary format common on hardware phones and some appliances. Most tools convert between them, so the format is rarely a blocker, but mismatched formats are a classic cause of load failures.
The bigger decision is self-signed versus CA-signed. Self-signed certificates work for internal labs and controlled fleets where you distribute the trust anchor to every device yourself. CA-signed certificates, including free ones from Let's Encrypt, validate automatically against standard trust stores and are the right choice for anything involving third parties.
Cipher Suites and Protocol Versions in SIP TLS
TLS 1.2 remains widely deployed in SIP infrastructure, but TLS 1.3 is the better choice in 2026: it completes the handshake in one round trip, removes legacy cipher families by design, and supports session resumption that suits long-lived SIP connections. For TLS 1.2 deployments, restrict the cipher list to authenticated-encryption suites such as AES-GCM and ChaCha20-Poly1305, and disable NULL, export, and CBC-mode ciphers. One caution: some older SIP hardware phones only support TLS 1.0 or 1.1, and deciding whether to keep supporting them is a genuine risk trade-off, not a technical footnote.
Configuring SIP TLS in Popular SIP Servers
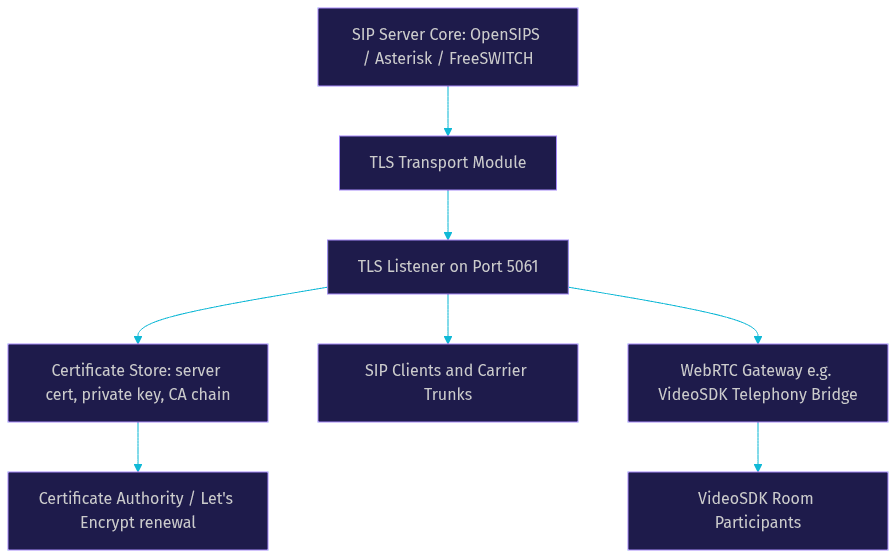
The configuration details differ across platforms, but the conceptual checklist is identical everywhere: enable the TLS listener, point it at your certificate and private key, define the trust store for validating peers, and make sure SIP endpoints are told to use the TLS transport in their addressing.
SIP TLS in OpenSIPS
In OpenSIPS, SIP TLS is enabled by activating the TLS transport module and declaring one or more TLS domains. Each TLS domain maps a listening socket to a certificate, private key, and optional CA list, which lets a single proxy serve different certificates for different hostnames using Server Name Indication. After defining the domains, you add a TLS listener on port 5061 and reload the TLS configuration. OpenSIPS supports hot certificate reload, so renewals do not require a full restart. Verify the listener with a TLS client probe before pointing production traffic at it.
SIP TLS in Asterisk
In Asterisk, SIP TLS starts with enabling the TLS-capable SIP channel driver and declaring a TLS listener in the channel configuration, then supplying certificate and key file paths through the TLS settings section. The certificate, its private key, and the CA certificate are referenced by file path, and Asterisk validates them at load time, so a mismatched key pair prevents the channel driver from starting. Endpoints then register using a TLS transport URI on port 5061. For PJSIP-based deployments, the same concepts apply through the transport configuration object, which binds certificates and cipher preferences to a specific listener.
SIP TLS in FreeSWITCH
FreeSWITCH loads SIP TLS through its SIP TLS module, which is enabled in the modules configuration and configured in the Sofia SIP profile. The profile references a certificate chain file, a private key file, and a CA bundle, and binds the TLS listener to port 5061. FreeSWITCH supports multiple profiles, so you can run a TLS profile for external trunking alongside a plain internal profile during migration. After a profile restart, the TLS endpoint appears in the status output, and certificate changes take effect on the next profile restart.
Managing SIP TLS Certificates and Renewal
Certificate expiry is the number one operational failure mode for SIP TLS deployments. When a certificate lapses, every TLS connection to that server fails, and phones fall back to registration loops or, worse, unencrypted transports if fallback is permitted. The fix is automation: issue certificates through Let's Encrypt using the ACME protocol with a DNS or HTTP challenge, and schedule automated renewal well before expiry, typically at two-thirds of the certificate lifetime.
Rotation should be zero-downtime. Write the renewed certificate and key to the live path, then trigger a hot reload where the platform supports it, as OpenSIPS does, or schedule a brief listener restart during a maintenance window where it does not. Always deploy the full chain, server certificate plus intermediates, because missing intermediates cause validation failures on clients that do not fetch them.
Key storage deserves equal attention. Private keys should be readable only by the service account running the SIP server, never committed to source control, and ideally generated on the host that will use them. For carrier interconnects with mutual authentication, track client certificate expiry on both sides, because an expired client certificate produces the same hard failure as an expired server certificate.
Troubleshooting Common SIP TLS Issues
Most SIP TLS failures cluster into four patterns. Handshake failures usually mean a protocol version or cipher mismatch: the client offers TLS 1.3 while an old appliance only speaks TLS 1.0, or the server's cipher list excludes the one suite the phone supports. Certificate validation failures come from expired certificates, missing intermediate chains, or a hostname mismatch between the SIP URI and the certificate's subject name. SNI errors appear when a server hosting multiple TLS domains receives a connection without the right Server Name Indication hint and presents the wrong certificate. Finally, silent plaintext fallback happens when a client fails TLS and quietly retries over UDP, which hides the problem while defeating the security goal.
SIP TLS Log Analysis
SIP TLS failures are almost always visible in the server logs if you know the vocabulary. Look for alerts describing handshake failure, which points to version or cipher negotiation problems; messages about certificate verification failure, which point to trust chain or expiry issues; and decode errors, which usually indicate a client speaking plaintext to a TLS port. Correlating the timestamp of a failed registration with the TLS log entry is usually enough to classify the failure in one pass.
SIP TLS Connectivity Checks
The standard verification tool is the OpenSSL command-line client, which can open a TLS connection to your SIP server's port 5061 and print the negotiated protocol version, cipher, and the full certificate chain as the server presents it. In prose terms: connect to the listener, read the reported certificate subject and issuer, confirm the chain resolves to a trusted root, and note whether the server requests a client certificate for mutual authentication. Running the same probe from a network segment that mirrors your carrier's path often reveals firewall or SNI issues that local testing misses.
SIP TLS Security Considerations and Best Practices
A hardened SIP TLS deployment in 2026 should follow a short, enforceable list. Disable TLS 1.0 and 1.1 entirely; both are formally deprecated and their presence weakens every connection negotiated against your server. Restrict cipher suites to authenticated encryption, prefer TLS 1.3 where clients support it, and document any exception granted for legacy hardware with a retirement date. Enforce mutual authentication on trunk and interconnect listeners, since server-only TLS still permits any holder of a valid client credential to register.
Operational hygiene matters as much as configuration. Keep the SIP server and its TLS library patched on a regular cadence, because TLS vulnerabilities are found in implementations, not just the protocol. Monitor certificate expiry with alerting rather than relying on renewal automation alone, and log TLS handshake failures so downgrade attempts and misconfigured endpoints surface quickly. Finally, never allow silent fallback to UDP or TCP on production endpoints; if TLS fails, the connection should fail loudly.
For teams bridging SIP into modern applications, the same principles apply at the gateway. VideoSDK's telephony integration terminates secure SIP trunks and routes calls into WebRTC rooms, so the SIP leg can carry TLS while the application leg carries DTLS-SRTP, keeping signaling and media encrypted end to end.
Future Trends for SIP TLS
SIP TLS will evolve along two tracks. The first is transport diversification: DTLS already secures SIP over WebSocket for WebRTC-based telephony, and QUIC-based SIP transport is an active area of IETF discussion, promising faster handshakes and better behavior on lossy mobile networks than TCP-based TLS. The second is protocol hardening: TLS 1.3 adoption in SIP infrastructure continues to grow, and post-quantum certificate algorithms are beginning to appear in general TLS deployments, which will eventually reach telephony PKI.
Practically, this means designing certificate management to be algorithm-agnostic and keeping transport configuration modular. Platforms that treat TLS as a swappable layer, rather than a hardcoded assumption, will absorb these changes without re-architecture.
Definitions Glossary
SIP TLS: The transport of SIP signaling messages over a TLS-encrypted connection, typically on port 5061, providing confidentiality, integrity, and peer authentication for call setup traffic.
Hop-by-hop encryption: The property that each leg between two adjacent SIP nodes is encrypted separately, requiring a TLS session on every hop rather than one end-to-end tunnel.
Mutual authentication (mTLS): A TLS mode where both the server and the client present certificates, so each party cryptographically verifies the other before any SIP message is exchanged.
Server Name Indication (SNI): A TLS extension letting a client indicate which hostname it is connecting to, allowing one SIP server to present different certificates for multiple TLS domains on a single listener.
Certificate chain: The sequence of certificates from the server certificate through intermediate authorities to a root CA trusted by the client, which must validate fully for a SIP TLS connection to succeed.
Key Takeaways
- SIP TLS encrypts signaling hop by hop on port 5061, protecting registration credentials, dialed numbers, and routing headers from eavesdropping and tampering.
- TLS 1.3 is the preferred protocol version in 2026, with a single-round-trip handshake and modern cipher suites; TLS 1.0 and 1.1 should be disabled everywhere.
- OpenSIPS, Asterisk, and FreeSWITCH all follow the same conceptual setup: enable the TLS listener, bind certificates and keys, define the trust store, and point endpoints at the TLS transport.
- Certificate expiry is the leading cause of SIP TLS outages, so automate renewal, deploy full chains, and alert on expiry rather than trusting automation alone.
- Enforce mutual authentication on trunk listeners and never allow silent fallback to plaintext transports in production.
Conclusion
SIP TLS is no longer optional for any serious VoIP deployment: it is the difference between signaling that anyone on the path can read and rewrite, and signaling that is confidential, tamper-proof, and mutually authenticated. Start with a TLS 1.3-capable listener on port 5061, automate your certificate lifecycle, enforce mutual authentication on trunks, and monitor handshake failures as a first-class operational signal. If you are bridging telephony into real-time applications, explore how VideoSDK's SIP and telephony integration connects secure SIP trunks into WebRTC rooms, and grab a free account at app.videosdk.live/login to try it. What are you securing with SIP TLS, a carrier interconnect, an enterprise PBX, or something stranger? Drop a comment, I'd love to hear about your deployment.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ