


Socket.IO architecture is a two-layer design: Engine.IO handles the low-level transport (HTTP long-polling with an upgrade to WebSocket), while Socket.IO adds an event-driven layer with namespaces, rooms, acknowledgments, and reconnection on top. Scaling horizontally requires an adapter, such as the Redis adapter, plus sticky sessions at the load balancer. If you are building production real-time features, pairing Socket.IO with a managed real-time communication platform like VideoSDK can offload the hardest scaling problems entirely.
Most developers meet Socket.IO through a chat tutorial, wire it up, and never look under the hood. That works until the first production incident: a load balancer that drops WebSocket upgrades, a second server instance that cannot see broadcasts from the first, or mobile clients on flaky networks silently disconnecting. Every one of those failures traces back to a misunderstanding of Socket.IO architecture.
This guide walks through the full internal design: the two-layer Engine.IO and Socket.IO split, how packets are serialized and transported, how the heartbeat and reconnection machinery keeps connections alive, and how adapters plus sticky sessions let you scale across multiple nodes. By the end, you will know exactly which component does which job, and where the architecture breaks when you scale it carelessly.
Understanding Socket.IO Architecture
Socket.IO is defined as an event-driven real-time communication library built on top of Engine.IO, a lower-level transport layer that manages the actual connection between client and server. The design goal is reliability first: a Socket.IO client will communicate even when WebSockets are blocked by proxies, firewalls, or corporate networks, and it will recover from disconnections without application code doing anything special.
Socket.IO works by negotiating the best available transport at connection time, then wrapping an application-level event system over that transport. The library is not a protocol replacement for WebSocket; it is a superset that adds connection recovery, event acknowledgments, rooms, and broadcasting semantics. This is why the Socket.IO client and server are not wire-compatible with a raw WebSocket client, a common source of confusion for teams mixing the two.
For applications that need audio and video rather than just messaging, the same architectural thinking applies to purpose-built real-time SDKs. VideoSDK, for example, provides video calling and interactive live streaming with rooms, participants, and token-based authentication handled at the platform level, so you are not hand-rolling signaling and scaling yourself.
Two-Layer Design: Engine.IO and Socket.IO
The separation of concerns is the single most important architectural idea in Socket.IO. Engine.IO owns everything about the wire: transport negotiation, the handshake, heartbeats, packet framing, and upgrade probes. Socket.IO owns everything about semantics: events, namespaces, rooms, acknowledgments, and automatic reconnection with buffered events.
This split means you could theoretically run Engine.IO alone as a bare transport, and some projects do. It also means transport problems and event problems have different debugging surfaces. A dropped connection every 25 seconds is an Engine.IO heartbeat issue; a broadcast that only some clients receive is a Socket.IO rooms or adapter issue. Knowing which layer owns which failure saves hours of guessing.
Core Components
A Socket.IO deployment is built from a small set of building blocks. The server instance listens for connections and hosts the event system. Each connected client gets a socket object representing its individual connection and its event handlers. Namespaces partition a single connection endpoint into isolated communication channels, which is useful for separating concerns like an admin channel from a public one. Rooms group sockets dynamically so you can broadcast to subsets of connected clients, such as everyone in a specific chat channel. Adapters abstract the broadcasting operation so it can work across multiple server processes, not just one. Finally, middleware functions run during the connection handshake, letting you authenticate or reject connections before any events flow.
Serialization and Packet Flow
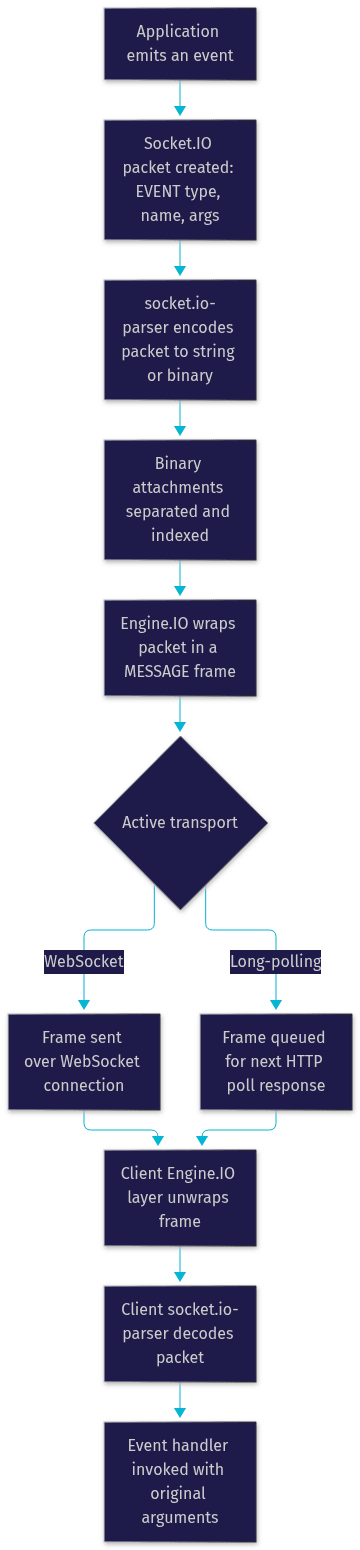
Data in Socket.IO never travels as raw application objects. When your server emits an event, the payload passes through a serialization pipeline that converts it into a compact wire format before it ever touches the network. Understanding this pipeline explains both the protocol overhead and the debugging artifacts you will see in network traces.
The flow has three stages. First, the Socket.IO layer creates a packet describing the operation: an event name, its arguments, and metadata like the packet identifier used for acknowledgments. Second, the socket.io-parser encodes that packet into a string or binary buffer, handling attached binary data such as images or files. Third, the Engine.IO layer wraps the encoded packet inside its own message frame and sends it over whichever transport is active, WebSocket or long-polling.
Packet Types and Encoding Process
The socket.io-parser recognizes a fixed set of packet categories. CONNECT packets establish a namespace connection on the client or server side. DISCONNECT packets signal a graceful teardown of a namespace. EVENT packets carry the application events you emit and listen for. ACK packets confirm receipt of an event that requested an acknowledgment. BINARYEVENT and BINARYACK variants handle the same operations when binary payloads are attached.
The encoding process is deliberately compact. Each packet begins with a numeric type identifier, followed by namespace and acknowledgment metadata where relevant, then the event payload itself. Binary attachments are stripped out, indexed, and sent as separate frames, with placeholders in the main packet marking where each attachment belongs. The client reassembles them on arrival. This is why a single emit with an image can produce multiple frames on the wire.
Message Wrapping and Transport
Once a Socket.IO packet is encoded, Engine.IO treats it as opaque payload data. Engine.IO adds its own framing: a packet type byte indicating whether the frame is a message, a ping, a pong, or a close signal. That framed message is then handed to the active transport.
Over WebSocket, the frame goes out immediately as a text or binary message. Over long-polling, the frame is queued and delivered in the response to the client's next HTTP poll request, which is why long-polling adds latency and why the transport upgrade matters so much for responsiveness. The two-layer wrapping also explains a subtle point: Engine.IO can carry any payload, and Socket.IO just happens to be the most common occupant of that envelope.
Transport Mechanisms and Reliability
Socket.IO's reputation for reliability comes from its transport negotiation strategy. Rather than assuming WebSocket works everywhere, the library starts with the most compatible option and upgrades opportunistically. This design decision, made in the original Engine.IO design, is why Socket.IO connections survive hostile networks where raw WebSocket clients simply fail.
Handshake, Long-Polling, and WebSocket Upgrade
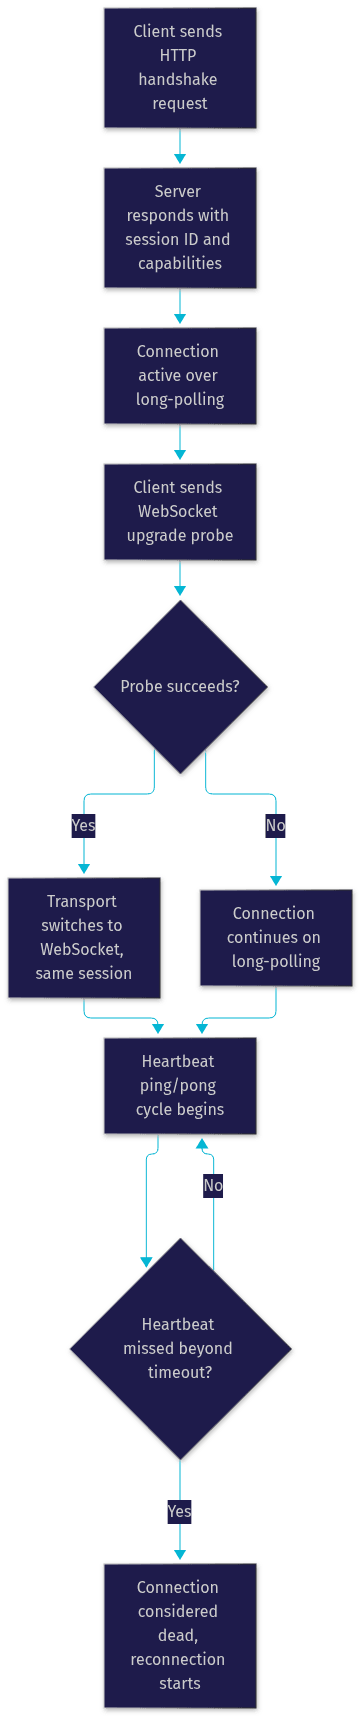
A connection begins with an ordinary HTTP request carrying handshake parameters: the client's supported transports, a session identifier, and any connection options. The server responds with its own capabilities and assigns the session. At this point the connection is already functional over long-polling: the client repeatedly issues HTTP requests that the server holds open until data is available or a timeout expires, then responds and the client immediately polls again.
In parallel, the client sends a WebSocket upgrade probe. Only when the probe round-trips successfully does the client switch the active transport to WebSocket, keeping the same session identifier so no state is lost. If the probe fails, due to a proxy stripping upgrade headers or a firewall blocking the port, the connection quietly continues on long-polling. The application never notices the difference except in latency.
Heartbeats and Reconnection Strategies
Engine.IO maintains connection liveness with a ping and pong heartbeat. The server periodically sends a ping packet, and the client must respond with a pong within a configured timeout window. If the server misses the response, it considers the connection dead and closes it, firing the disconnect event. The client similarly monitors the server, and if no heartbeat arrives within its own threshold, it assumes the network is down.
On top of this, the Socket.IO layer implements automatic reconnection. When a connection drops, the client enters an exponential backoff retry loop, attempting to re-establish the same session and, failing that, negotiate a fresh one. Events emitted while disconnected can be buffered and flushed on reconnect. The practical implication is significant: your application code can treat disconnection as a transparent, self-healing condition rather than something to handle manually, as long as you tune the heartbeat intervals to your network profile rather than accepting defaults blindly.
Scaling Socket.IO
A single Socket.IO server process handles thousands of concurrent connections comfortably. The architecture problem appears the moment you run a second process. Rooms and broadcasts live in process memory by default, so server instance A has no idea that server instance B holds a socket that should receive your broadcast. Horizontal scaling in Socket.IO is fundamentally about solving this visibility problem.
Adapter Pattern for Horizontal Scaling
The adapter is the architectural answer. Every broadcast operation in Socket.IO, whether targeting a room, a namespace, or all connected sockets, is delegated to an adapter object. The default in-memory adapter performs the broadcast locally, which is correct for one process and silently incomplete for several.
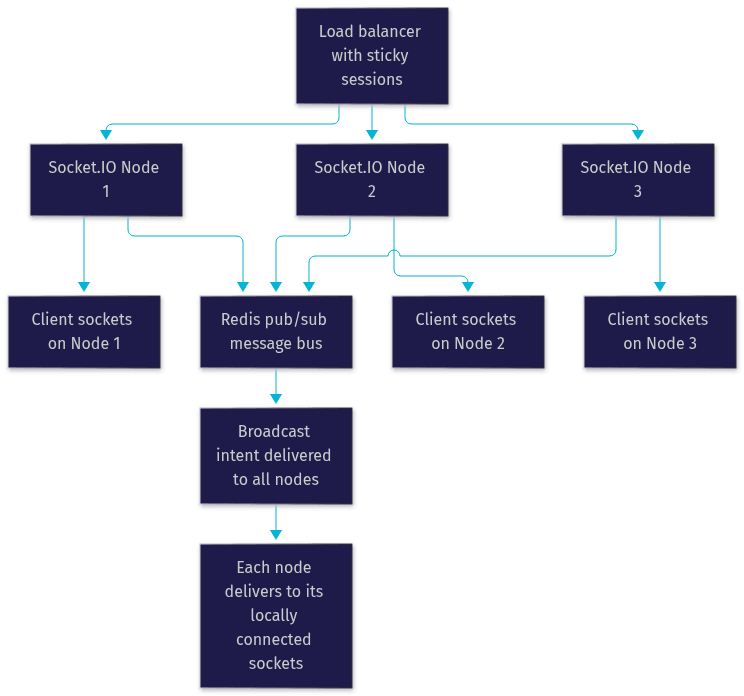
A distributed adapter changes the broadcast path: instead of only delivering to local sockets, it publishes the broadcast intent to a shared message bus, and every Socket.IO node subscribed to that bus receives the intent and delivers it to its own local sockets. The application code is unchanged; only the adapter wiring differs. This is a clean instance of the adapter pattern abstracting away the physical location of connected clients.
Popular Adapters
The Redis adapter is the most widely deployed option. It uses Redis pub/sub as the message bus, is simple to operate, and fits teams already running Redis for caching or sessions. Its main limitation is that Redis pub/sub is fire-and-forget: if a node is briefly disconnected from Redis, it misses broadcasts during that window.
The PostgreSQL adapter uses PostgreSQL's LISTEN and NOTIFY mechanism, which suits teams that want fewer moving parts and already run PostgreSQL, though it carries database-specific throughput characteristics. The built-in cluster adapter is designed for Node.js cluster mode on a single machine, using worker-to-worker communication instead of an external broker, making it a good fit for vertical scaling before you need a full multi-node setup.
Choosing between them is a deployment decision, not an application one. Pick the adapter that matches infrastructure you already run and understand.
Deployment Considerations
Running Socket.IO in production introduces constraints that localhost development never surfaces. The two that bite hardest are load balancer behavior and stateful connections.
Load Balancing and Sticky Sessions
Socket.IO connections are stateful: a client's handshake, session, and upgrade state live on one specific server node. If a load balancer routes the client's requests to different nodes on each poll, the handshake state will not be found and the connection collapses. This is why sticky sessions, also called session affinity, are mandatory when you scale beyond one node.
Session affinity means the load balancer pins a client to the same backend node for the life of the connection, typically keyed on a cookie set during the handshake. Most mainstream load balancers and reverse proxies support this configuration directly. The alternative, disabling long-polling entirely and forcing WebSocket-only connections, reduces the sticky session requirement in some setups but sacrifices the fallback reliability that motivated Socket.IO in the first place. In practice, enabling cookie-based affinity is the safer default.
Containerization and Serverless Options
Socket.IO deploys cleanly into containers. A Docker image wrapping your server, orchestrated by Kubernetes with a deployment and a service in front, is a common production shape. The key Kubernetes-specific requirement is still session affinity at the ingress or load balancer layer, plus a distributed adapter since your pods are separate processes by definition.
Serverless is a poorer fit. Platforms like AWS Fargate work well because each task is a long-running container that holds stateful connections. But function-per-request platforms such as AWS Lambda conflict with Socket.IO's core model: connections need a process that stays alive between requests, holds handshake state, and maintains heartbeats. If your target platform cannot keep a process resident, you need a different architecture, such as a managed real-time platform, rather than a workaround.
Real-World Use Cases
The architecture choices map directly onto application categories. Chat systems are the canonical case: namespaces separate public and direct-message channels, rooms hold conversation groups, and the Redis adapter lets multiple chat nodes broadcast consistently. Collaborative editing adds a different pressure, high-frequency small events, where packet encoding overhead and heartbeat tuning matter more than raw broadcast scale.
Live dashboards stream server metrics or analytics to many viewers with few writers, a pattern where room broadcasting shines because one emit reaches thousands of subscribed sockets. Multiplayer games stress the reliability layer hardest: mobile clients on unstable networks depend on automatic reconnection and buffered events, while competitive play demands the lowest-latency transport path, meaning you should verify the WebSocket upgrade actually succeeds rather than silently degrading to long-polling.
For use cases that extend beyond messaging into live audio and video, such as live classrooms, live shopping, or virtual events, teams commonly pair Socket.IO-style signaling with a dedicated real-time media SDK. VideoSDK's interactive live streaming handles the media plane, host and viewer roles, and RTMP output, leaving Socket.IO or an equivalent to handle lightweight coordination events.
Common Pitfalls and Best Practices
The recurring production failures are predictable. The most common is deploying multiple Socket.IO nodes without a distributed adapter, producing broadcasts that only reach clients on the emitting node. The fix is choosing and configuring an adapter before you add the second instance, not after users report missing messages.
The second is skipping sticky sessions at the load balancer, which manifests as random handshake failures and reconnect loops that look like client-side bugs. The third is ignoring heartbeat configuration: default ping intervals suit desktop browsers on stable networks, but mobile and IoT clients on intermittent connections often need more generous timeouts to avoid the server killing healthy-but-slow connections.
The fourth is over-relying on in-memory room state for business logic. Rooms are a broadcast routing tool, not a database; membership is lost on disconnect and restart. Persist authoritative state in a real datastore and treat rooms as an ephemeral index. Finally, monitor the transport mix in production. If a large share of clients sit on long-polling because an intermediary blocks upgrades, your latency budget is being silently consumed, and the fix belongs in your proxy configuration, not your application.
Definitions Glossary
Engine.IO: The low-level transport layer inside Socket.IO that manages the handshake, transport negotiation, heartbeats, and packet framing over WebSocket or long-polling.
Namespace: A named communication channel partitioning a single Socket.IO connection endpoint, allowing isolated event flows such as an admin channel alongside a public one.
Room: A dynamic grouping of connected sockets that broadcast operations can target, used for routing messages to subsets of clients like the members of one chat conversation.
Adapter: The pluggable component that abstracts broadcast delivery, enabling a message to reach sockets connected to other server processes through a shared bus such as Redis pub/sub.
Sticky Sessions: A load balancer configuration that pins each client to the same backend node for the duration of a connection, required because Socket.IO handshake state is held on a specific server process.
Long-Polling: A fallback transport where the client repeatedly issues HTTP requests that the server holds open until data is available, providing compatibility when WebSocket is blocked.
Key Takeaways
- Socket.IO architecture is a two-layer design: Engine.IO owns transport, handshake, and heartbeats, while Socket.IO owns events, namespaces, rooms, and reconnection semantics.
- Connections start on long-polling and upgrade to WebSocket via a probe, which is why Socket.IO survives networks where raw WebSocket clients fail.
- Every emitted event passes through a serialization pipeline: a Socket.IO packet is encoded by the socket.io-parser, then wrapped in an Engine.IO frame before hitting the wire.
- Horizontal scaling requires a distributed adapter, such as the Redis adapter, plus sticky sessions at the load balancer; either one missing produces silently broken broadcasts.
- Rooms are ephemeral broadcast routing, not persistent storage, so keep authoritative application state in a real datastore.
- For real-time audio and video use cases beyond messaging, a managed platform like VideoSDK's video calling SDK handles rooms, scaling, and media delivery at the infrastructure level.
Conclusion
Socket.IO architecture rewards the effort of understanding it. The Engine.IO and Socket.IO layer split tells you where every failure lives, the serialization pipeline explains what actually crosses the network, and the adapter-plus-sticky-sessions combination is the complete recipe for horizontal scaling. Most production Socket.IO incidents trace back to one of these four areas being misunderstood rather than any defect in the library itself.
If you are designing a real-time feature, map your requirements against this architecture first, then review the scaling diagrams above before writing integration code. And if your use case extends into live audio and video, explore VideoSDK's documentation and try it free at app.videosdk.live. What are you building with Socket.IO or VideoSDK? Drop a comment, I'd love to hear what kind of real-time use case you are working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ