


TSIP (Trunking Session Initiation Protocol) is an extension of the Session Initiation Protocol designed specifically for carrier-grade SIP trunking scenarios. It adds enhanced security (TLS, mutual authentication), multi-tenant support, and SIP-connect compliance on top of standard SIP signaling. VideoSDK's telephony and SIP integration layer can accept TSIP-enabled trunks, letting developers bridge traditional carrier infrastructure with real-time WebRTC video and audio rooms. To get started, explore the VideoSDK Telephony documentation.
SIP trunking adoption has been accelerating sharply. According to industry projections, the global SIP trunking services market is expected to surpass $30 billion by 2026, driven by enterprises migrating from legacy ISDN and TDM lines to IP-based carrier connections. If you are building or maintaining a VoIP infrastructure, you have likely encountered the term TSIP in carrier documentation, RFC references, or trunk configuration guides. The question "what is tsip" surfaces frequently among developers integrating enterprise telephony with modern real-time communication platforms.
This article breaks down what TSIP is, how it differs from standard SIP and SIP-T, where it fits in a real call flow, and what you need to know to deploy it in production. By the end, you will understand the protocol layers, security mechanisms, deployment considerations, and how TSIP connects to platforms like VideoSDK for embedded video calling.
What is TSIP? Definition and Core Purpose
TSIP is defined as Trunking Session Initiation Protocol, an extension profile of SIP (Session Initiation Protocol) engineered for high-volume trunking between enterprises, IP-PBX systems, and carrier networks. While standard SIP handles peer-to-peer and end-user call signaling, TSIP focuses on the trunking layer where thousands of concurrent calls traverse a single logical connection between a PBX and a service provider.
TSIP works by layering additional header extensions, mandatory TLS transport, and carrier-grade authentication mechanisms on top of the SIP signaling defined in RFC 3261. The protocol profile enforces compliance with SIP-connect specifications, ensuring that interoperability between different vendors' equipment remains predictable. In practice, TSIP defines a stricter ruleset than vanilla SIP: it mandates encrypted transport, requires explicit tenant identification in multi-tenant environments, and standardizes how media negotiation occurs across trunk boundaries.
For developers, the key distinction is that TSIP is not a brand-new protocol. It is a constrained, hardened profile of SIP that removes ambiguity. Where standard SIP allows loose interpretation of header usage and transport selection, TSIP narrows those choices to a carrier-safe subset. This is why telecom carriers and large enterprises adopt TSIP profiles rather than raw SIP for their trunk connections.
TSIP vs. SIP-T
SIP-T (SIP for Telephones) is an older extension defined in RFC 3666 and RFC 3372 that focuses on carrying ISUP (ISDN User Part) signaling over SIP for interworking with traditional SS7-based PSTN networks. SIP-T encapsulates ISUP messages inside SIP bodies so that calls traversing from a SIP network to the PSTN retain their SS7 signaling context.
TSIP, by contrast, is a trunking profile that does not inherently deal with ISUP encapsulation. Instead, it addresses the modern problem of securing and scaling SIP trunks between IP-native endpoints. TSIP adds mandatory TLS encryption, tenant-scoped authentication headers, and SIP-connect compliance, none of which SIP-T specifies. In short, SIP-T solves PSTN interworking. TSIP solves carrier-grade IP trunking at scale.
Key TSIP Features
TSIP profiles typically include the following capabilities that distinguish them from baseline SIP deployments:
- TLS-encrypted signaling transport: All SIP messages traverse TLS tunnels, preventing eavesdropping and signaling tampering on the trunk leg.
- SIP-connect compliance: Adherence to the SIP-connect specification ensures vendor interoperability for IP-PBX to carrier trunk connections, reducing configuration friction.
- Media-path optimization: TSIP profiles encourage direct media paths between endpoints where possible, reducing latency by avoiding unnecessary media relay hops.
- Carrier-grade authentication: Mutual TLS authentication and token-based trunk credentials replace the simpler digest authentication used in user-level SIP registrations.
- Multi-tenant support: Header extensions allow a single trunk to carry traffic for multiple tenant organizations, with the carrier able to identify and route based on tenant context.
- Header standardization: TSIP reduces ambiguity in SIP header usage, which is one of the leading causes of inter-vendor interoperability failures in standard SIP deployments.
How TSIP Fits Into the SIP Call Flow
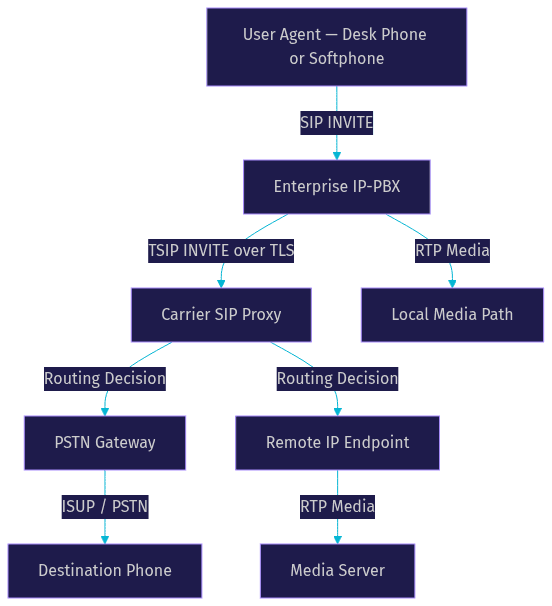
Understanding what TSIP is requires seeing where it sits in a real call flow. Consider a scenario where an enterprise user places an outbound call through an IP-PBX that connects to a carrier via a TSIP-enabled trunk. The call flow involves several hops, and TSIP governs the trunk leg specifically.
The user agent (a desk phone or softphone) sends a SIP INVITE to the enterprise IP-PBX. The PBX processes the dialed number, applies internal routing rules, and determines that the call must exit through the carrier trunk. At this point, the PBX constructs a TSIP-compliant INVITE. This means the INVITE is sent over TLS, includes the required TSIP header extensions for tenant identification and trunk authentication, and carries an SDP body that conforms to the codec and media parameters negotiated for that trunk.
The carrier's SIP proxy receives the TSIP INVITE, validates the TLS certificate presented by the PBX, checks the trunk authentication headers, and routes the call toward the destination. If the destination is on the PSTN, the carrier's gateway converts the SIP signaling to ISUP or another PSTN protocol. If the destination is another IP endpoint, the carrier routes the SIP signaling onward and establishes a media path.
The critical value TSIP adds is on the trunk leg between the PBX and the carrier. This is the segment where security, scalability, and multi-tenancy matter most. Standard SIP on this leg would leave transport encryption optional, authentication weak, and tenant isolation undefined. TSIP closes those gaps.
The diagram below illustrates a typical TSIP call flow from user agent through to the media server:
Technical Building Blocks
TSIP relies on several protocol layers working in concert. At the signaling layer, it uses the SIP message format defined in RFC 3261, the core SIP specification. At the transport layer, it mandates TLS, typically following the guidelines in RFC 3261 for SIP-over-TLS and the SIPS URI scheme. At the media negotiation layer, it uses SDP (Session Description Protocol) as defined in RFC 4566, with codec and media attribute negotiation following standard SDP offer-answer procedures.
For DNS resolution of SIP trunk targets, TSIP deployments rely on RFC 3263, which defines how SIP entities locate the appropriate server using DNS SRV and NAPTR records. This is particularly important for TSIP because carriers often publish multiple proxy endpoints for redundancy, and the PBX must resolve and failover between them correctly.
SIP-connect compliance, which TSIP profiles build upon, references additional RFCs for specific behaviors. RFC 7585 and related specifications address aspects of SIP trunking architecture and interdomain routing. Developers implementing TSIP-compatible systems should familiarize themselves with RFC 3261 (core SIP), RFC 3263 (SIP DNS resolution), and the SIP-connect specification published by the SIP Forum.
TSIP Header Extensions
TSIP profiles define several header extensions that carry trunk-specific metadata. Common extensions include a private authentication header that carries trunk credentials or token references, and a tenant identification header that allows the carrier to associate the call with a specific tenant organization in a multi-tenant trunk deployment. Additional headers may carry trunk group identifiers, which help carriers apply routing and billing rules based on the logical trunk group the call belongs to.
These headers are typically prefixed with a private designation, indicating they are non-standard extensions defined by the TSIP profile or the specific carrier's implementation. Developers should consult their carrier's TSIP documentation for the exact header names and values expected, as these can vary between providers.
Security Mechanisms
Security is where TSIP diverges most significantly from baseline SIP. The first layer is transport security: all SIP signaling on the trunk leg must traverse TLS. This is not optional in a TSIP profile. The carrier and the PBX present mutual TLS certificates, establishing bidirectional identity verification before any SIP message is exchanged.
The second layer is trunk authentication. Beyond the TLS certificate, TSIP profiles may require additional credential headers in the SIP REGISTER or INVITE messages. These credentials are typically provisioned by the carrier and tied to a specific trunk or tenant.
The third layer, which is optional but recommended for sensitive deployments, is SRTP (Secure Real-time Transport Protocol) for the media path. While TSIP primarily governs signaling, many TSIP deployments also encrypt the media using SRTP with keys exchanged via SDES (Session Description Protocol Security Descriptions) or DTLS-SRTP. This ensures that neither the signaling nor the media can be intercepted on the trunk leg.
Deployment Considerations
Deploying a TSIP-compatible trunk involves several practical steps that go beyond standard SIP configuration. The first step is selecting a carrier or SIP trunk provider that supports TSIP or SIP-connect compliance. Not all providers advertise TSIP support explicitly, but those who comply with the SIP-connect specification generally support the profile's requirements.
The second step is configuring TLS certificates. You need a certificate that the carrier trusts, which may mean obtaining a certificate from a recognized CA or provisioning a carrier-specific certificate. The certificate must be installed on your PBX or session border controller, and the carrier's certificate must be trusted on your side. Mutual TLS configuration is the most common stumbling block in TSIP deployments because certificate chain issues, expired certificates, and hostname mismatches all cause silent failures.
The third step is NAT traversal. If your PBX sits behind a firewall or NAT device, you need to ensure that SIP signaling and RTP media can traverse the boundary correctly. Session border controllers (SBCs) are typically used for this purpose, as they handle NAT traversal, media anchoring, and topology hiding. For TSIP, the SBC must also terminate or pass through TLS correctly, which adds configuration complexity.
The diagram below shows a production TSIP deployment architecture with an enterprise edge gateway, firewall, and monitoring stack:
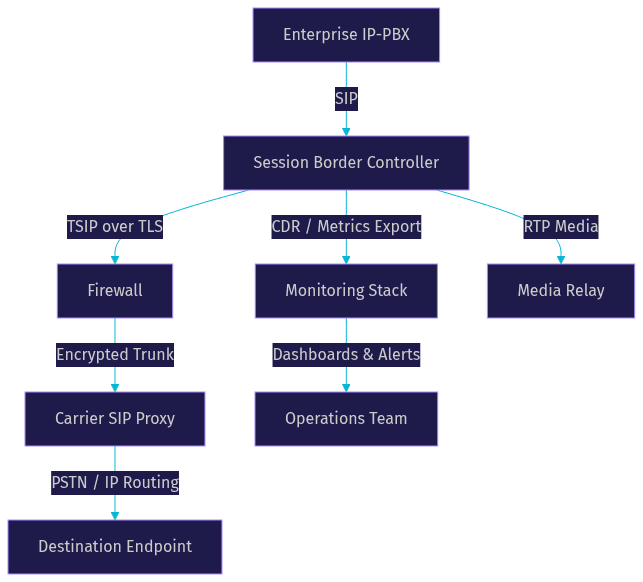
What most tutorials skip is production-grade monitoring. Once your TSIP trunk is live, you need visibility into call success rates, signaling error codes, media quality metrics, and TLS handshake failures. Without a monitoring stack that ingests CDRs (Call Detail Records) and RTCP (RTP Control Protocol) reports, you are flying blind. Carriers will blame your equipment, and you will have no data to refute or diagnose. Invest in a monitoring solution that correlates SIP signaling traces with media quality metrics before you go live.
Common Pitfalls and Troubleshooting
Three issues account for the majority of TSIP deployment problems. The first is certificate mismatch. The hostname in your TLS certificate must match the hostname the carrier expects. If your certificate says one hostname and your SIP signaling presents another, the TLS handshake fails. Diagnose this by capturing the TLS handshake and comparing the certificate's subject and subject alternative names against the carrier's documented requirements.
The second issue is mismatched TSIP header extensions. Different carriers may expect slightly different header names or value formats for tenant identification and trunk authentication. If your PBX sends headers the carrier does not recognize, the carrier may reject the call or route it incorrectly. Diagnose this by comparing a SIP message trace from your PBX against the carrier's TSIP specification document.
The third issue is codec incompatibility. TSIP trunks are typically provisioned with a specific set of codecs. If your PBX offers codecs the trunk does not support, the SDP negotiation fails and the call never connects. Diagnose this by examining the SDP offer and answer in a SIP trace, and ensure your PBX's codec list matches the carrier's provisioned codec set.
TSIP Use Cases
TSIP profiles are deployed across several real-world scenarios. Carrier-to-carrier trunking is the most common: when two telecom operators exchange traffic, they use TSIP-compatible trunks to ensure secure, scalable, and interoperable signaling. The multi-tenant headers allow each carrier to identify the originating and terminating tenant for billing and routing purposes.
Large-scale contact center deployments use TSIP trunks to connect their PBX or contact center platform to their carrier. These environments handle thousands of concurrent calls, and the TLS-encrypted signaling and carrier-grade authentication that TSIP provides are essential for compliance and security. Contact centers also benefit from the media-path optimization in TSIP profiles, which reduces latency for customer interactions.
A growing use case is secure video-calling gateways that combine TSIP trunks with WebRTC-based video platforms. In this scenario, an enterprise uses a TSIP trunk to receive inbound calls from the PSTN, then bridges those calls into a WebRTC video room where a remote expert, healthcare provider, or support agent joins via video. This is where VideoSDK's telephony integration becomes relevant.
How TSIP Relates to VideoSDK
VideoSDK's SIP and telephony integration bridges traditional SIP telephony with VideoSDK's WebRTC-based real-time communication rooms. The VideoSDK telephony layer includes an inbound gateway that accepts SIP calls from external providers and routes them into VideoSDK rooms, and an outbound gateway that initiates calls from VideoSDK rooms to external phone numbers.
For enterprises running TSIP-enabled trunks, this means you can connect your existing carrier trunk to VideoSDK's telephony gateway. The TSIP trunk handles the secure, carrier-grade leg between your PBX and your carrier. VideoSDK handles the WebRTC leg between the room and your application's video participants. The gateway translates between SIP and WebRTC media, so a PSTN caller on a TSIP trunk can join a VideoSDK video room and interact with participants who joined via web or mobile SDKs.
This architecture is particularly useful for telehealth, customer support, and remote expert scenarios where PSTN callers need to be bridged into a video session without installing an app. Developers can use VideoSDK's REST APIs to manage the telephony routing, and the Python SDK for AI-powered voice agent pipelines that process calls entering through TSIP trunks.
Quick Recap
- TSIP is a carrier-grade trunking profile of SIP that mandates TLS encryption, multi-tenant headers, and SIP-connect compliance for secure, scalable trunk connections.
- It differs from SIP-T, which focuses on ISUP encapsulation for PSTN interworking, while TSIP focuses on IP-native trunk security and scalability.
- VideoSDK's telephony integration can accept TSIP-enabled trunks, bridging traditional carrier infrastructure into WebRTC-based video and audio rooms.
Further Reading
- VideoSDK Telephony Introduction — how SIP calls connect to VideoSDK rooms
- VideoSDK REST API Reference — room and participant management endpoints
- VideoSDK AI Agents Documentation — building voice agent pipelines on top of telephony
- VideoSDK Code Samples — integration examples across platforms
- W3C WebRTC Specification — the WebRTC standard that VideoSDK builds upon
- IETF RFC 3261 — the core SIP specification
Definitions Glossary
TSIP (Trunking Session Initiation Protocol): A carrier-grade extension profile of SIP designed for high-volume trunking between enterprises, IP-PBX systems, and carrier networks, mandating TLS encryption and SIP-connect compliance.
SIP-T (SIP for Telephones): An older SIP extension that encapsulates ISUP signaling within SIP messages for interworking with traditional SS7-based PSTN networks.
SIP-connect: A specification published by the SIP Forum that defines interoperability requirements for IP-PBX to carrier SIP trunk connections, which TSIP profiles build upon.
Session Border Controller (SBC): A network element that sits at the boundary between two SIP networks, handling NAT traversal, security, media anchoring, and protocol normalization for SIP trunks.
SRTP (Secure Real-time Transport Protocol): A protocol for encrypting RTP media streams, used optionally in TSIP deployments to secure the media path alongside TLS-secured signaling.
Key Takeaways
- TSIP is not a new protocol but a hardened, constrained profile of SIP that removes ambiguity and mandates security for carrier-grade trunking scenarios.
- The protocol's mandatory TLS transport, multi-tenant header extensions, and SIP-connect compliance make it suitable for high-volume enterprise and carrier deployments where standard SIP would be too loose.
- Developers deploying TSIP trunks should prioritize mutual TLS certificate management, NAT traversal via session border controllers, and production-grade monitoring of signaling and media quality.
- VideoSDK's telephony integration can accept TSIP-enabled trunks, allowing PSTN callers to join WebRTC-based video rooms without installing an application.
- Understanding the distinction between TSIP and SIP-T is essential for developers working on modern VoIP infrastructure, as the two address fundamentally different problems.
Conclusion
TSIP represents the telecom industry's answer to a real problem: standard SIP is too permissive for the trunking layer where security, scalability, and multi-tenancy are non-negotiable. By mandating TLS, standardizing header usage, and enforcing SIP-connect compliance, TSIP profiles give enterprises and carriers a predictable, secure framework for IP-native trunk connections. For developers building real-time communication applications, understanding what TSIP is and how it interacts with modern WebRTC platforms like VideoSDK opens up architectures that bridge the PSTN and the web seamlessly. If you are ready to connect your TSIP trunk to a video calling platform, explore the VideoSDK telephony docs or sign up at app.videosdk.live/login to get started. What are you building with VideoSDK? Drop a comment below, I would love to hear what kind of telephony or video calling use case you are working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ