


Socket.IO over HTTPS means running its real-time engine on a TLS-encrypted server so every WebSocket connection uses the secure wss protocol instead of plain ws. You need a valid certificate (self-signed for development, CA-signed for production), an HTTPS server in Node.js or an Nginx reverse proxy in front of it, and client options that trust the certificate. This guide walks through the full setup, dual HTTP/HTTPS architectures, and the most common wss connection errors and their fixes. For production-grade real-time apps with built-in security, VideoSDK's video calling SDK handles transport security for you out of the box.
Introduction
Every unencrypted WebSocket connection is a open microphone into your application. Anyone on the same network can read messages, hijack sessions, or inject packets, and browsers increasingly refuse plain ws connections from HTTPS pages altogether. That last point is the one that catches most developers: you deploy your app behind HTTPS, and your Socket.IO client silently fails because the browser blocks the insecure WebSocket as mixed content.
Securing Socket.IO with HTTPS is not optional in 2026, it is the baseline. Whether you are building a chat app, a live dashboard, or a multiplayer game, the fix is the same: terminate TLS, upgrade your transport to wss, and make sure every layer of your stack, from the Node.js server to the Nginx proxy to the client options, agrees on the certificate and protocol.
By the end of this article you will understand how Socket.IO and HTTPS interact, how to configure each layer, and how to diagnose the errors that appear when something in the chain is misconfigured.
Understanding Socket.IO and HTTPS
Socket.IO is defined as a real-time communication library built on top of the WebSocket protocol, with automatic fallback to HTTP long-polling when a direct WebSocket connection cannot be established. Socket.IO works by first performing an HTTP handshake with the server, negotiating a connection identifier, and then upgrading that connection to a persistent WebSocket channel whenever both sides support it.
HTTPS enters the picture at the transport layer. When your server is wrapped in TLS, the initial HTTP handshake and the subsequent WebSocket upgrade both happen over an encrypted channel. The WebSocket protocol's secure variant, wss, is simply WebSocket running inside that TLS tunnel. Everything Socket.IO sends, event names, payloads, acknowledgments, is encrypted in transit.
This matters for two reasons. First, without TLS, anyone between the client and server can read every event your app emits. Second, browsers enforce mixed-content rules: a page loaded over HTTPS cannot open a plain ws connection, so an unsecured Socket.IO server simply will not connect from a secured page. If you are evaluating real-time platforms, VideoSDK's real-time communication architecture applies the same principle, encrypting all media and signaling traffic by default.
Setting Up an HTTPS Server for Socket.IO
The foundation of Socket.IO over HTTPS is a Node.js server initialized with TLS credentials instead of a plain HTTP listener. Get the certificate right first, because every downstream error traces back to it.
Choosing a Certificate Type
You have two options. A self-signed certificate is generated locally, costs nothing, and is fine for development, but browsers and Node clients will not trust it by default. A certificate signed by a public certificate authority, such as one issued by Let's Encrypt, is trusted everywhere and is mandatory for production. The practical rule: use self-signed certificates only on localhost, and automate CA-signed certificates with a renewal tool like Certbot for anything users touch.
Creating the HTTPS Server in Node.js
Node.js provides a dedicated TLS server constructor for this purpose. The setup intent is straightforward: read your private key file and certificate file from disk, pass them together into the secure server constructor alongside your request handler, and start listening on port 443 or a high port for local testing. The expected behavior is that all incoming connections arrive encrypted, and the handshake completes only if the client trusts your certificate chain. If your certificate authority provided an intermediate chain file, include it as well, otherwise some clients, particularly mobile runtimes and Node processes, will reject the connection even though desktop browsers may accept it.
Attaching Socket.IO to the HTTPS Server
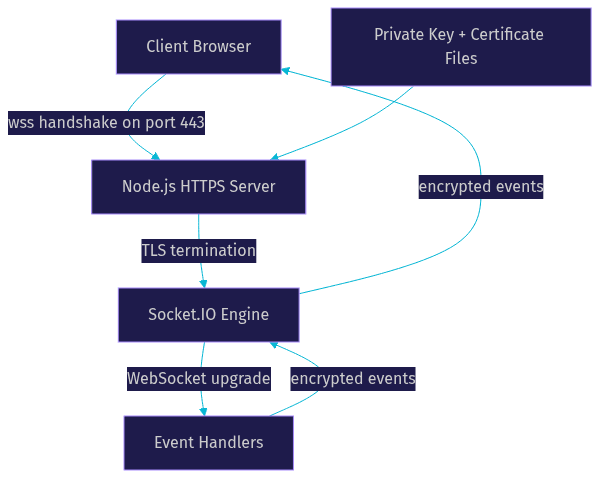
Once the secure server exists, you initialize Socket.IO by passing that server instance to it rather than a port number. The engine then rides on the TLS listener, and every client connects using the wss scheme. No separate configuration is needed inside Socket.IO itself for encryption, because TLS is handled entirely by the server it is attached to.
The overall flow looks like this:
Supporting Both HTTP and HTTPS Simultaneously
Many real-world deployments need to serve plain HTTP and HTTPS at the same time, and Socket.IO supports this cleanly.
Why Dual Protocols May Be Needed
The most common scenario is a device network: local devices on a LAN reach your server by IP address over HTTP, while public users arrive through a domain name over HTTPS. Another case is a staged migration, where you enable HTTPS for new clients while older clients still connect over HTTP until they are updated. In both situations you want one Socket.IO instance, one set of event handlers, and two entry points.
Architecture Overview
The approach is to create two server listeners, one plain HTTP on port 80 and one HTTPS on port 443, and attach the same Socket.IO instance to both. In Node.js this means constructing the Socket.IO engine with an explicit parent-less instance and then attaching each server to it in turn. Clients that connect over HTTP negotiate ws, clients over HTTPS negotiate wss, and both land in the same event space, so a message emitted by one reaches participants on both transports.
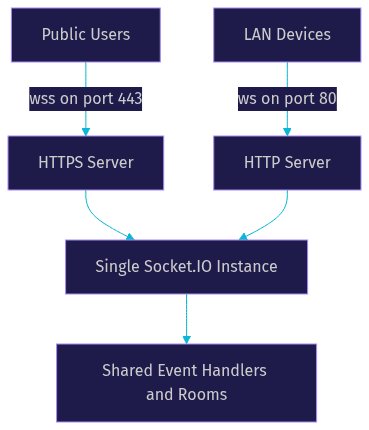
One caution: if you serve an HTTPS page, its scripts still cannot open ws connections due to mixed-content rules, so dual protocol only helps when the page itself is served over the matching protocol. For production, redirect all HTTP traffic to HTTPS and treat the dual setup as transitional.
Configuring Nginx as a Reverse Proxy for Secure Socket.IO
In most production deployments, Nginx terminates TLS and forwards traffic to a plain Socket.IO server running on localhost. This is the recommended pattern because it centralizes certificate management and lets Nginx handle static assets and load balancing.
Basic Proxy Settings
The core of the configuration is a location block that proxies requests to your Node.js process. The proxy pass directive points at your local server address, typically port 3000 on localhost. Two header directives are essential for WebSockets: the upgrade header and the connection header set to the literal value upgrade. These headers tell your Node.js process that the client requested a protocol upgrade to WebSocket, and omitting either one is the single most common cause of Socket.IO falling back to long-polling behind a proxy.
Handling WebSocket Upgrade Over HTTPS
Nginx defaults to HTTP/1.0 when proxying, but the WebSocket handshake requires HTTP/1.1 features, specifically the ability to carry the upgrade request. Setting the proxy HTTP version to 1.1 in your location block enables this. Additionally, raise the proxy read timeout, because a WebSocket connection is long-lived and Nginx's default of 60 seconds will silently drop idle connections, causing clients to reconnect in a loop.
Common Pitfalls
Three mistakes account for most broken setups. First, missing upgrade headers, which forces Socket.IO into polling mode and produces laggy, reconnecting clients. Second, mixed content, where an HTTPS page tries to open a ws connection and the browser blocks it silently. Third, CORS misalignment: when Socket.IO runs on a different origin than your frontend, the server must explicitly allow the frontend's origin, and the allowed origin must match the scheme exactly, https included. If you would rather avoid managing this stack yourself, VideoSDK's Prebuilt UI Kit delivers secure real-time communication without any proxy configuration.
Client-Side Connection Options for HTTPS
The client side has its own set of considerations, especially around certificate trust and local development.
Using the Secure Flag and RejectUnauthorized
When connecting from a Node.js client, the secure option forces the client to use HTTPS for the initial handshake and wss for the WebSocket channel. The rejectUnauthorized option controls certificate validation: leaving it at its default true state means the client verifies the server certificate against its trust store, which is what you want in production. Setting it to false disables verification, which is occasionally necessary for self-signed certificates in development but should never reach a production environment, because it opens the connection to interception.
Dealing with Self-Signed Certificates
For local development with a self-signed certificate, the cleaner approach is to add the certificate to your system or runtime trust store rather than disabling verification. Node.js accepts an extra certificate authority file through an environment variable, which lets your client validate the self-signed chain properly. Browsers are stricter: you must visit the HTTPS endpoint once and accept the warning before the page can open a wss connection to it.
Fallback to HTTP for Local Development
A common pattern is conditional connection logic: the client inspects the current page protocol and builds its Socket.IO URL accordingly, using wss when the page is served over HTTPS and ws or localhost HTTP otherwise. This keeps local development frictionless while ensuring production always connects securely, without hardcoding either scheme.
Troubleshooting Common HTTPS Issues
Even with a correct setup, connection errors surface. Here are the three you will meet most often, with their causes and fixes.
"Transport unknown" Error
This error appears when the client requests a transport the server does not recognize, and behind a proxy it almost always means the upgrade headers never reached Node.js. Check that your Nginx location block sets both the upgrade and connection headers and that the proxy HTTP version is 1.1. A second cause is a version mismatch between the client and server Socket.IO libraries, since the handshake format has changed across major versions, so keep both sides on the same major version.
Certificate Verification Failures
Browsers and Node clients fail differently. A browser shows a certificate warning page, usually caused by an expired certificate, a hostname mismatch, or a missing intermediate chain. A Node client throws a verification error during the handshake with no visible warning, often because the intermediate certificate was not bundled with the server certificate. The fix in both cases is the same: verify the chain with an online SSL checker, confirm the certificate covers the exact hostname the client connects to, and reload the full chain into your server configuration.
WebSocket Connection Refused
A refused connection means the request never reached a listening process. Work through the chain in order: confirm your Node.js process is running and listening on the expected port, confirm Nginx is proxying to that exact port, and confirm any firewall or cloud security group allows inbound traffic on 443. A frequent variant is the server listening only on localhost while Nginx proxies to a public interface, or vice versa. Finally, check that the client URL uses the wss scheme and the correct port, since a client pointing at port 3000 directly will be refused when TLS is only terminated on 443.
Best Practices for Production-Ready Secure Socket.IO
Once the basic setup works, a few operational habits keep it secure and reliable at scale.
Enforce HSTS and Secure Cookies
Enable HTTP Strict Transport Security on your domain so browsers refuse any future plain HTTP requests, eliminating downgrade and mixed-content problems permanently. If your app uses cookies for session identity, mark them secure so they are only transmitted over HTTPS, and set the same-site attribute to restrict cross-site abuse.
Rotate Certificates Regularly
Automate certificate renewal with your CA's tooling, such as Certbot for Let's Encrypt, and set renewal hooks that reload Nginx so the new certificate takes effect without downtime. An expired certificate is the most preventable production outage in this stack, and monitoring expiry dates costs minutes compared to the hours an outage consumes.
Monitor and Log TLS Handshakes
Log handshake failures at the Nginx layer and alert on spikes. A sudden rise in handshake errors usually indicates a certificate problem, a protocol version misconfiguration, or an attempted attack, and catching it early turns a mystery outage into a five-minute fix.
Scale with Load Balancers
When you run multiple Socket.IO processes, use the ip_hash or sticky-session strategy on your load balancer, because the Socket.IO handshake must reach the same process that issued the session. Combine this with the Redis adapter so events broadcast across all nodes, and terminate TLS at the load balancer so certificate management stays centralized.
Definitions Glossary
wss: The secure WebSocket protocol, which is WebSocket running inside a TLS-encrypted channel. Socket.IO automatically uses wss when attached to an HTTPS server or reached through a TLS-terminating proxy.
TLS/SSL certificate: A digital credential that binds a public key to a hostname, allowing clients to verify server identity and encrypt traffic. Self-signed variants work for development but require explicit client trust.
Mixed content: A browser security rule that blocks insecure ws or HTTP requests initiated from a page loaded over HTTPS. It is the most common reason a Socket.IO client silently fails on a secured page.
Reverse proxy: An intermediary server, such as Nginx, that terminates TLS and forwards requests to a backend process. For Socket.IO it must pass upgrade headers and use HTTP/1.1 to support the WebSocket handshake.
Sticky sessions: A load balancing strategy that routes each client to the same backend process. Socket.IO requires them when scaled horizontally because the handshake and the upgraded connection must land on the same server.
Key Takeaways
- Socket.IO over HTTPS requires a TLS-encrypted server or a TLS-terminating proxy, after which all WebSocket traffic automatically uses the secure wss protocol.
- Browsers block plain ws connections from HTTPS pages due to mixed-content rules, so an unsecured Socket.IO server fails silently on any secured frontend.
- Nginx reverse proxying works only when the upgrade and connection headers are set and the proxy uses HTTP/1.1, otherwise Socket.IO degrades to long-polling.
- Self-signed certificates are acceptable only for development, and disabling certificate verification in a client must never reach production.
- If you want production-grade secure real-time communication without managing certificates, proxies, and scaling yourself, VideoSDK's SDKs provide encrypted real-time transport across ten-plus platforms out of the box.
Conclusion
Securing Socket.IO with HTTPS comes down to three coordinated layers: a valid certificate, a TLS-aware server or proxy, and a client that trusts the chain. Start with a self-signed certificate on localhost, graduate to a CA-signed certificate behind Nginx for production, enforce HSTS once everything works, and automate renewal so an expired certificate never takes you down. The troubleshooting patterns above, upgrade headers, certificate chains, and port reachability, resolve the overwhelming majority of wss connection failures.
If you are building real-time features and want to skip the infrastructure work entirely, explore VideoSDK's documentation or try the free tier at app.videosdk.live. What are you building with Socket.IO over HTTPS? Drop a comment, I would love to hear what kind of real-time use case you are working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ