


Mastodon WebRTC integration means adding real-time video and voice calls to a federated Mastodon instance using the browser-native WebRTC protocol stack. Because WebRTC runs peer-to-peer in the browser, media can flow directly between users without routing through a central video provider, which fits Mastodon's decentralized, privacy-focused model. This guide walks through the architecture, signaling options, federation challenges, and a step-by-step integration path, including how a managed service like VideoSDK can shortcut the hardest parts of building RTC on Mastodon.
Since Elon Musk's acquisition of Twitter drove millions of users toward alternatives, Mastodon has grown into the most widely adopted federated social network built on the ActivityPub protocol. As of 2026, the network spans thousands of independent instances, each with its own community, moderation policy, and infrastructure. But one thing almost every instance lacks is real-time communication. Threads, boosts, and DMs are asynchronous by design, and that leaves a gap: communities that want live town-halls, voice rooms, or one-on-one video calls have nowhere to go without leaving the platform for a centralized service.
That gap is exactly where WebRTC fits. WebRTC is the browser-native real-time communication stack, and it aligns naturally with Mastodon's ethos: no plugins, no central media provider, and media that can flow directly between participants. By the end of this article, you'll understand the full architecture for Mastodon WebRTC integration, the signaling and federation challenges you'll face, and a practical step-by-step path to shipping video and voice on your own instance.
What Is WebRTC?
WebRTC is defined as a free, open-source technology stack that enables real-time audio, video, and data exchange directly between browsers and devices without plugins or downloads. It works by establishing a peer connection between two or more participants, negotiating network paths through a process called ICE (Interactive Connectivity Establishment), and then streaming encrypted media over that connection.
The core components are worth understanding before you integrate anything with Mastodon. The peer connection is the object that manages media negotiation and transmission between participants. ICE is the framework that finds a usable network path between peers, testing multiple candidate routes. STUN servers help peers discover their public IP address so they can attempt a direct connection. TURN servers act as encrypted relays when a direct path fails, which happens frequently behind corporate firewalls and symmetric NATs. Data channels carry arbitrary structured data alongside media, useful for chat overlays or shared state during a call.
WebRTC works in every modern browser, including mobile Safari and Chrome on Android, because the media engine, encryption layer (mandatory DTLS/SRTP), and network traversal logic are built into the platform itself. Your application only supplies two things: a signaling mechanism to exchange connection metadata, and the UI to render media streams. That second part, signaling, is where Mastodon integration gets interesting.
Why Integrate WebRTC with Mastodon?
Adding real-time communication to a federated social network gives communities something they currently have to leave the platform to get: live interaction. A Mastodon instance that supports video calls can host community town-halls, moderator Q&A sessions, live tutoring, or private one-on-one calls between members, all without sending users to a centralized video provider that monetizes their metadata.
The privacy argument is the strongest one. Mastodon's user base skews heavily toward people who chose decentralization deliberately, and routing their video calls through a big-tech conferencing tool undermines that choice. WebRTC media is encrypted end-to-end at the transport layer by default, and with a peer-to-peer topology, media never touches a third-party server at all. For privacy-focused video conferencing, that combination is hard to beat.
The challenge, of course, is federation. Mastodon instances are independent servers that communicate asynchronously through ActivityPub, a protocol that was never designed for real-time media negotiation. Cross-instance calls require solving signaling across server boundaries, which we cover in detail below. The reward for solving it is significant: real-time communication in federated platforms is one of the most requested missing features in the entire fediverse.
Architecture Overview: Mastodon + WebRTC
A Mastodon WebRTC deployment has four logical pieces: the Mastodon instance itself, a signaling service, the WebRTC peers (user browsers), and the media path between them. The Mastodon instance handles identity, authentication, and social context, such as who is allowed to call whom. The signaling service exchanges the session descriptions and ICE candidates that let browsers find each other. The peers then stream media directly to one another, or through a TURN relay if direct connection fails.
The key architectural decision is keeping signaling separate from media. Mastodon's Ruby on Rails backend was not built for persistent, low-latency WebSocket connections at scale, so the standard pattern is a lightweight signaling microservice sitting alongside the instance, authenticated against Mastodon's token system. Media never passes through the signaling layer at all; it flows peer-to-peer or through TURN.
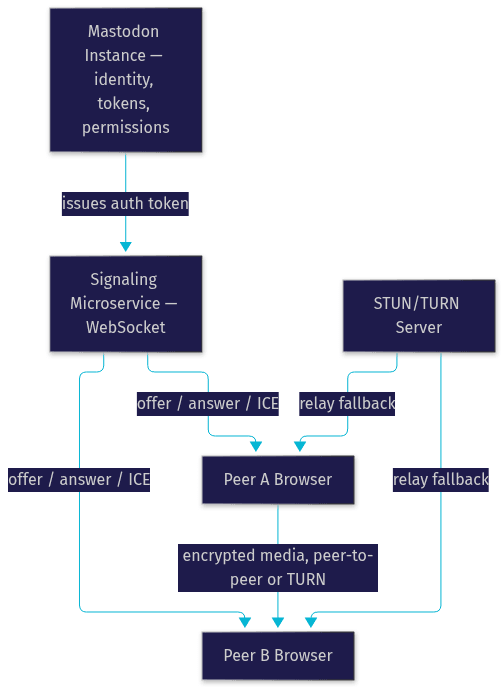
This separation matters for federation too. Because signaling is its own service, you can decide independently whether it serves only your instance's users or federates across instances. That decision shapes everything else, so it's worth making deliberately rather than defaulting into a single-instance design and retrofitting federation later.
Signaling Options for Mastodon
Signaling is the exchange of connection metadata, offers, answers, and network candidates, needed before two browsers can talk. WebRTC deliberately leaves the transport of this metadata up to the application, and on Mastodon you have three realistic options.
A WebSocket-based signaling server is the recommended approach. A small Node.js service using a WebSocket library gives you persistent bidirectional channels, sub-second message delivery, and full control over authentication and room logic. It's a well-understood pattern with mature tooling.
MQTT-based signaling trades some latency and simplicity for scalability, publishing signaling messages to topics that subscribers receive. It works, but topic-based access control gets awkward when you want per-call authorization tied to Mastodon identities.
ActivityPub-based signaling is the most federated option in spirit, but ActivityPub delivery is asynchronous and can take seconds, which breaks the interactive nature of call setup. In practice, treat ActivityPub as the discovery layer, such as announcing that a user is callable, and use WebSockets for the actual real-time handshake.
Handling Federation and Cross-Instance Calls
Cross-instance calls are the hardest problem in Mastodon WebRTC, because two users may be on entirely different servers with no shared trust relationship. The cleanest pattern is a shared signaling service that both instances trust: each instance's backend validates its own user's identity and issues a short-lived token scoped to a specific call, and the signaling service accepts tokens from any participating instance. This mirrors how Mastodon already handles cross-instance verification for other interactions.
An alternative is federated signaling messages, where instance A's signaling server forwards call setup messages to instance B's signaling server over an authenticated server-to-server channel. This preserves full decentralization, since no third service is involved, but it requires every participating instance to run compatible signaling software, which limits reach in a network where software versions vary widely.
For most communities in 2026, the pragmatic answer is the shared signaling approach for cross-instance calls, with peer-to-peer media flowing directly between the two browsers once setup completes. Federation then only affects the handshake, not the media path, which keeps latency low regardless of how far apart the instances are.
Step-by-Step Integration Guide
This walkthrough explains the full integration path in natural language. Every step describes what to do, why it matters, and what you should see when it works.
Step 1: Verify Prerequisites
Your Mastodon instance needs a standard production stack: a supported Ruby version matching your Mastodon release, Node.js for the signaling service, Redis for pub/sub and caching, and PostgreSQL for the instance database. You'll also need a domain or subdomain for the signaling service with a valid TLS certificate, since browsers only allow WebRTC media and secure WebSockets on HTTPS origins. Confirm your reverse proxy can forward WebSocket upgrades on the signaling subdomain before moving on.
Step 2: Add the Signaling Microservice
Stand up a small Node.js service whose only job is relaying signaling messages between authenticated participants. It should accept WebSocket connections, validate a token presented at connection time, and then route offer, answer, and ICE-candidate messages between the two peers in a call. Keep it stateless where possible: call state can live in Redis so that restarting the service doesn't drop in-progress setups. The expected behavior is that when one browser creates a call offer, the other browser receives it within milliseconds and can respond.
Step 3: Extend Mastodon's Backend
Add a small set of call-initiation endpoints to your instance, either as a Mastodon patch or as a companion service that reads the Mastodon database. These endpoints handle three things: creating a call record with a unique call identifier, checking permissions (is the callee accepting calls, are they blocked, is the caller allowed), and issuing a short-lived signaling token scoped to that specific call. The token should carry the caller's identity, the call identifier, and an expiry, and should be signed with a secret shared with the signaling service. This is the same token-based pattern VideoSDK uses for its own authentication and token flow, and it's worth studying as a reference design even if you build your own.
Step 4: Update Mastodon's Frontend
On the frontend, add a call button to profile and DM views that requests a call initiation from the backend, receives the call identifier and token, and opens a WebSocket to the signaling service. Then implement the WebRTC side in a React overlay component: request camera and microphone permission, create a peer connection, generate an offer, send it through the signaling channel, and handle the incoming answer and ICE candidates. When negotiation completes, attach the remote media stream to a video element in the overlay. The user-visible result is a call button that transitions into a full call UI with both participants' video.
If you'd rather not hand-build the call UI and negotiation logic, this is also the point where a Prebuilt UI Kit can be embedded instead, giving you a working call interface while your custom code only handles identity and permissions.
Step 5: Manage Permissions and Token Authentication
Every call must be authorized twice: once by the Mastodon backend when the call is initiated, and once by the signaling service when the WebSocket connects. Tokens should expire quickly, ideally within minutes, and should be scoped so that a token for one call cannot be reused for another. Respect user preferences, such as a per-user setting for who may call them, and surface consent UI before any camera or microphone access is requested, since browsers will prompt anyway and a jarring permission dialog with no context causes users to deny it.
Step 6: Deploy to Production
Production deployment changes several things. HTTPS is mandatory for both the instance and the signaling service. You need a STUN server for basic NAT discovery, and realistically a TURN server with short-term credentials, because a meaningful fraction of real-world users, often estimated at 10 to 20 percent depending on audience, cannot complete direct peer-to-peer connections. Run the signaling service behind a load balancer with sticky sessions or Redis-backed state so horizontal scaling works. Finally, monitor signaling latency and connection failure rates, since those two metrics catch most real-world WebRTC problems before users report them.
Setting Up the Signaling Server
The signaling server needs four logical message types: join, offer, answer, and ICE candidate exchange. A join message authenticates the participant and attaches them to a call room. Offer and answer messages carry the session descriptions that negotiate codecs and media parameters. ICE messages carry network candidates as peers probe for usable paths. Mastodon's backend calls into this service only indirectly, by issuing the tokens that grant access to it, which keeps the coupling between your instance and the signaling layer minimal and lets you restart or replace either side independently.
Updating Mastodon's UI
The frontend work centers on three elements: a call button in appropriate contexts, an overlay component that hosts the call, and media stream attachment. The overlay should render local and remote video, expose mute and hang-up controls, and handle the disconnection case gracefully by showing a reconnection state rather than silently dropping the call. Attaching media streams means binding the incoming remote stream to a video element as soon as it arrives, which in practice is the moment users perceive the call as "working," so test it early and often.
Security and Privacy Considerations
Security for Mastodon WebRTC has four layers. First, transport encryption is automatic: WebRTC mandates DTLS and SRTP for all media, so media in transit is always encrypted. Second, end-to-end encryption for multi-party calls requires inserting keys in a way only participants can access, which is significantly more engineering work and is worth doing only if your threat model demands it. Third, token scoping: signaling tokens must be short-lived, single-call, and signed, as described in the integration steps above. Fourth, consent: users must explicitly opt in to being callable, and the UI must make clear when camera and microphone are live.
Privacy considerations extend to GDPR if your instance serves EU users. Call metadata, who called whom and when, is personal data, so log only what you need, retain it briefly, and document it in your instance privacy policy. If you use a TURN server, note that it relays encrypted media but can see connection metadata, and disclose it accordingly.
Testing and Debugging Tips
Debugging WebRTC is mostly about inspecting the negotiation sequence. Browser developer tools expose the internal state of peer connections, including which ICE candidates were gathered, which candidate pair was selected, and whether the connection is using a direct path or a TURN relay. When a call fails, the first check is always whether ICE completed: if no candidate pair succeeds, the problem is network traversal, and you should verify your TURN server credentials and reachability.
For cross-instance testing, simulate it locally by running two browser profiles with different accounts on two different instances pointed at your shared signaling service. Test on a real mobile network at least once, since carrier NAT behaves very differently from home networks. And test the permission-denied path deliberately: what does your UI do when a user blocks camera access? A graceful fallback to audio-only is far better than a broken call screen.
Scaling WebRTC on Large Mastodon Communities
Scaling breaks into two problems: signaling scale and media scale. Signaling scales horizontally with load-balanced WebSocket servers backed by Redis for shared state, and this part is conventional engineering. Media scale is harder, because peer-to-peer mesh topologies degrade quickly as participants are added; a mesh call with eight participants means each browser uploads seven separate streams, which overwhelms typical upstream bandwidth.
For calls beyond roughly four to six participants, you need a media relay architecture, either an SFU (selective forwarding unit) that routes streams server-side, or a managed RTC platform. This is exactly the problem VideoSDK's video calling infrastructure solves, with network-adaptive streaming that adjusts bitrate and resolution per participant, built-in TURN fallback, and server-side room management via REST APIs. For a large Mastodon instance hosting regular town-halls, offloading media to a managed SFU while keeping identity and permissions in Mastodon is a defensible architecture: your instance stays the source of truth for community and trust, and the RTC layer handles what it's built for.
TURN server selection matters at scale too. Run TURN with short-lived rotating credentials rather than static ones, place it geographically near your user base, and monitor its bandwidth, since TURN relay traffic is the hidden cost multiplier in any large deployment.
Real-World Use Cases
The use cases cluster around community life. Community town-halls let instance admins host live Q&A sessions for their members, with the instance's own moderation tools governing who speaks. Live tutoring and classrooms fit naturally on education-focused instances, where a teacher can drop a call link into a thread. Decentralized video conferences serve activist groups, privacy communities, and organizations that specifically cannot use centralized conferencing tools. One-on-one calls between mutuals are the simplest and probably most-demanded case, turning Mastodon DMs into a full communication medium.
A concrete example: imagine a 4,000-member Mastodon instance focused on open-source software, running monthly "ask the maintainer" voice rooms. With WebRTC integrated, the maintainer joins a voice room from a post on the timeline, members raise hands through the existing moderation system, and the whole event stays on infrastructure the community controls.
Definitions Glossary
WebRTC: A browser-native technology stack for real-time audio, video, and data exchange between peers, with mandatory transport encryption and no plugins required.
Signaling: The application-provided mechanism for exchanging connection metadata, offers, answers, and ICE candidates, between peers before media can flow. WebRTC does not define a signaling protocol, so Mastodon integrations must supply one, typically over WebSockets.
ICE (Interactive Connectivity Establishment): The framework WebRTC uses to find a usable network path between two peers by testing candidate routes in parallel.
STUN/TURN: STUN helps peers discover their public network address for direct connection; TURN is an encrypted relay used when direct connection fails, common behind restrictive NATs and firewalls.
ActivityPub: The federated protocol Mastodon uses for cross-instance communication. It is asynchronous by design, which makes it unsuitable for real-time signaling but useful for call discovery and presence.
SFU (Selective Forwarding Unit): A media server that receives each participant's stream and forwards it selectively to others, enabling group calls without the bandwidth cost of a full peer-to-peer mesh.
Key Takeaways
- WebRTC fits Mastodon's decentralized ethos because media flows directly between users' browsers with mandatory encryption, without a central video provider.
- Keep signaling separate from your Mastodon Rails backend: a small WebSocket microservice, authenticated with short-lived signed tokens, is the recommended architecture.
- Cross-instance calls are best handled by a shared signaling service that trusts tokens from participating instances, with ActivityPub reserved for discovery rather than real-time handshake.
- Production requires HTTPS, a TURN server for the 10 to 20 percent of users who can't connect directly, and horizontal scaling of the signaling layer.
- For group calls beyond four to six participants, peer-to-peer mesh breaks down; use an SFU or a managed RTC platform like VideoSDK, which offers network-adaptive streaming and REST-based room management.
Conclusion
Mastodon WebRTC integration turns a federated social network into a full communication platform: live town-halls, voice rooms, and private calls, all on infrastructure your community controls. The engineering path is clear, from a WebSocket signaling service and token-scoped authentication to TURN fallback and SFU-based scaling for larger groups. If you want to shortcut the media layer entirely, VideoSDK's SDKs handle rooms, adaptive streaming, and TURN out of the box, with a free tier to start experimenting, and code samples to reference. What are you building with WebRTC on Mastodon? Drop a comment, I'd love to hear what kind of federated calling use case you're working on.
Step 5: Implement Participant View
In this step, we will implement the participant view, which displays all participants in the WebRTC session. This feature is crucial for providing a comprehensive and interactive experience by showing the video streams of all connected users.
Participant View Implementation
[a] HTML Structure
Ensure your HTML file includes a container to display the participant video streams.
HTML
1   <div id="videoChat" style="display: none;">
2     <video id="localVideo" autoplay muted></video>
3     <div id="remoteVideos"></div>
4     <div id="controls">
5       <button id="muteBtn">Mute</button>
6       <button id="endCallBtn">End Call</button>
7     </div>
8   </div>
[b] JavaScript to Handle Remote Streams
Update your WebRTC integration code to handle multiple participants and display their video streams.
JavaScript
1   const SimplePeer = require('simple-peer');
2   const io = require('socket.io-client');
3
4   const socket = io.connect('http://localhost:3000');
5   let localPeer;
6   let peers = {}; // Store peer connections
7
8   // Function to initialize a WebRTC connection
9   function initWebRTC(isInitiator, stream) {
10     localPeer = new SimplePeer({
11       initiator: isInitiator,
12       stream: stream,
13       trickle: false
14     });
15
16     localPeer.on('signal', data => {
17       socket.emit('signal', { room: 'webrtc_room', signal: data });
18     });
19
20     localPeer.on('stream', remoteStream => {
21       addRemoteStream(remoteStream);
22     });
23
24     socket.on('signal', data => {
25       if (data.signal) {
26         localPeer.signal(data.signal);
27       }
28     });
29   }
30
31   // Function to add remote stream to the participant view
32   function addRemoteStream(stream) {
33     const remoteVideo = document.createElement('video');
34     remoteVideo.srcObject = stream;
35     remoteVideo.autoplay = true;
36     remoteVideo.playsInline = true;
37     document.getElementById('remoteVideos').appendChild(remoteVideo);
38   }
39
40   // Function to start a WebRTC session
41   function startSession() {
42     navigator.mediaDevices.getUserMedia({ video: true, audio: true })
43       .then(stream => {
44         const localVideo = document.getElementById('localVideo');
45         localVideo.srcObject = stream;
46         localVideo.play();
47         initWebRTC(true, stream); // Initialize WebRTC as the initiator
48       })
49       .catch(err => console.error('Error accessing media devices.', err));
50   }
51
52   // Event listener for joining a room
53   socket.on('connect', () => {
54     socket.emit('join', 'webrtc_room');
55   });
56
57   // Export the startSession function
58   module.exports = { startSession };
[c] CSS for Participant View
Add CSS to style the remote video elements and ensure a responsive layout.
CSS
1   #remoteVideos {
2     display: flex;
3     flex-wrap: wrap;
4     justify-content: center;
5     margin-top: 20px;
6   }
7
8   #remoteVideos video {
9     width: 45%;
10     margin: 10px;
11     border: 1px solid #ccc;
12     background-color: #000;
13   }
[d] JavaScript to Handle New Participants
Update the socket event to handle new participants joining the session.
JavaScript
1   socket.on('newParticipant', data => {
2     if (!peers[data.id]) {
3       const peer = new SimplePeer({ initiator: false });
4       peers[data.id] = peer;
5
6       peer.on('signal', signal => {
7         socket.emit('signal', { id: data.id, signal: signal });
8       });
9
10       peer.on('stream', remoteStream => {
11         addRemoteStream(remoteStream);
12       });
13
14       peer.signal(data.signal);
15     }
16   });
By implementing the participant view, users can see all participants in the WebRTC session, enhancing the interactive experience. The next step will focus on running and testing your complete Mastodon WebRTC application.
Step 6: Run Your Code Now
With all the components in place, it's time to run and test your Mastodon WebRTC application. Follow these steps to ensure everything works seamlessly.
[a] Start the Mastodon Server
Make sure your Mastodon server is running:
sh
1 RAILS_ENV=production bundle exec rails s[b] Start the WebRTC Signaling Server
Run your Socket.IO server to handle signaling:
sh
1 node server/socket.js[c] Access Your Application
Open your Mastodon instance in a web browser and navigate to the page with your WebRTC integration.
[d] Test the Functionality
- Click the "Start Session" button.
- Allow access to your camera and microphone.
- Verify that your local video stream is displayed.
- Test the mute/unmute and end call functionalities.
- Ensure that remote participants' video streams are displayed correctly.
Congratulations! You've successfully integrated WebRTC into your Mastodon instance, enabling real-time communication features. This integration enhances user interaction by providing video and audio capabilities directly within the social network platform and social wall.
Conclusion
This guide walked you through setting up a Mastodon WebRTC application, from project initialization and environment setup to implementing key features like the join screen, controls, and participant view. By following these steps, you've created a dynamic and interactive Mastodon instance that leverages the power of WebRTC.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ