


OpenAI Agents are autonomous AI systems that perform multi-step workflows by combining language models with tools, memory, and guardrails. They operate through a continuous loop of reasoning, tool execution, and handoffs, enabling complex task automation without constant human intervention. Developers can build and deploy these agents using OpenAI's managed APIs or self-hosted SDKs, and platforms like VideoSDK extend their capabilities into real-time voice and telephony scenarios.
Developers building production AI applications in 2026 are hitting a wall that simple chatbot APIs cannot solve. A user asks a complex question that requires querying a database, calling an external API, waiting for a result, and then synthesizing a response across multiple steps. Single-turn model calls break down here. OpenAI Agents solve this by giving models the autonomy to loop through reasoning, tool calls, and handoffs until a task completes. Whether you are building a customer support bot that triages tickets or a data analysis pipeline that queries warehouses and generates reports, understanding how OpenAI Agents work under the hood is essential for shipping reliable AI workflows.
What Are OpenAI Agents?
OpenAI Agents are AI systems designed to complete multi-step tasks autonomously by combining a language model with tools, persistent memory, and safety guardrails. Instead of responding to a single prompt and stopping, an agent reasons about what to do next, calls external functions when needed, hands off to specialized sub-agents for complex subtasks, and loops until the user's request is fully addressed. The core premise is that modern AI applications need orchestration, not just inference. An agent wraps the model in a control loop that manages context, executes tools, and enforces behavioral boundaries.
VideoSDK extends this paradigm into real-time communication through its AI Voice Agent SDK, which connects OpenAI's models to live audio and video rooms. This lets developers build agents that not only reason and call tools but also speak, listen, and interact with users over phone calls and web sessions in real time.
Core Concepts
An agent is the top-level entity that receives instructions and decides actions. Tools are external functions the agent can call to fetch data or perform operations. Handoffs transfer control from one agent to another when a task requires specialized expertise. Guardrails are validation checks that run before or after agent actions to enforce safety and correctness. Sessions preserve conversation state across turns so agents maintain context without reprocessing entire histories each time.
Understanding the OpenAI Agents Architecture
The OpenAI Agents architecture is built around a managed execution environment that handles the complexity of running autonomous AI workflows. At the center is the Codex harness, a managed runtime that provides sandboxed execution environments where agents can run code, call tools, and interact with external systems safely. The sandbox isolates agent actions from the host system, preventing untrusted tool outputs or model-generated code from causing unintended side effects.
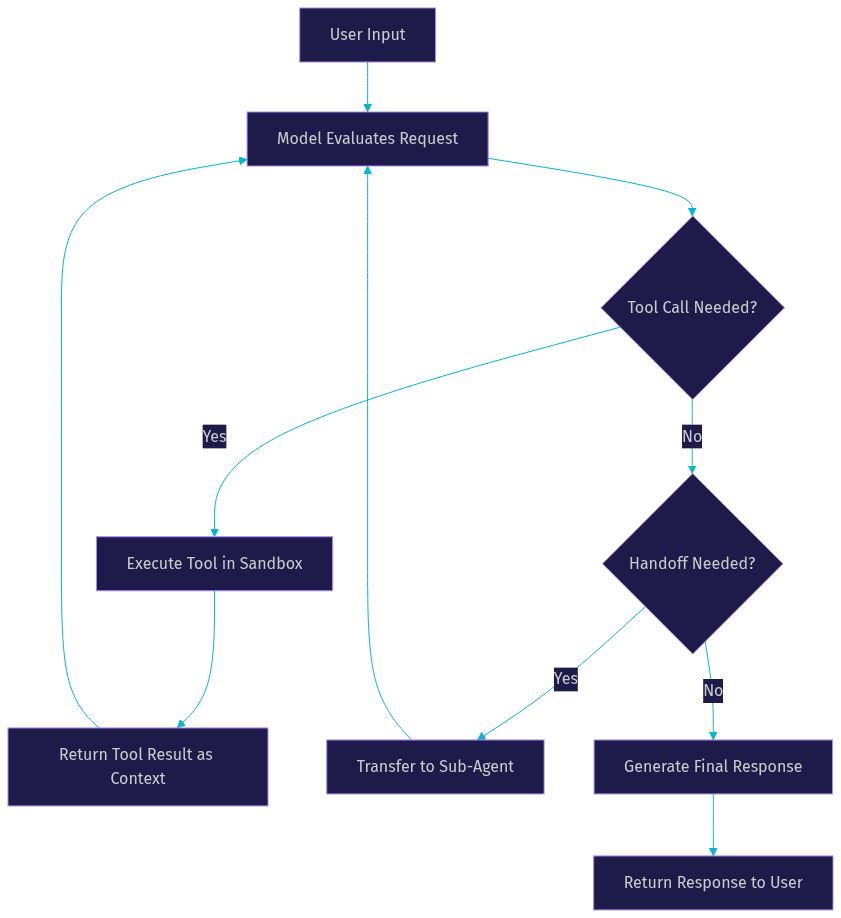
Data flows through the system in a structured pipeline. User input enters the agent loop, where the model evaluates the current state and decides whether to respond directly, call a tool, or hand off to another agent. Tool results feed back into the loop as new context, triggering another round of reasoning. This cycle continues until the agent produces a final response or explicitly terminates the session. The architecture supports both stateless and stateful execution, with session management handled at the platform level so developers can focus on agent behavior rather than infrastructure.
For developers building voice-based agents, VideoSDK's Python SDK integrates with this architecture by providing the media transport layer that carries audio streams between users and AI models, complementing the reasoning and tool-calling capabilities of the OpenAI platform.
The Agent Loop Explained
The agent loop is the heartbeat of every OpenAI Agents workflow. It begins when user input arrives and the model evaluates the request against its instructions and available tools. If the model determines that a tool call is needed, it emits a structured tool request. The runtime executes that tool and returns the result as additional context. The model then re-evaluates with the new information. If the task requires a different agent's expertise, a handoff occurs, transferring the conversation and relevant state to the specialized agent. This loop repeats until the agent generates a final response with no further tool calls or handoffs.
Session and State Management
OpenAI Agents support four primary state-persistence strategies, each suited to different scenarios. The result history approach retains the full conversation transcript locally and resends it with each turn, which is simple but token-expensive for long conversations. The session object stores state server-side within the OpenAI platform, reducing token usage but requiring session lifecycle management. The conversationId approach references a prior conversation by identifier, enabling lightweight continuity without resending context. The previousResponseId strategy chains responses by referencing the last response ID, which is the most token-efficient option for sequential interactions. Choose result history for short, stateless workflows. Use sessions for long-running multi-turn conversations. Use previousResponseId for cost-sensitive sequential chains.
Tool Integration and Handoffs
Tools extend agent capabilities by exposing external functions, APIs, and data sources. The OpenAI Agents platform supports function tools defined as structured schemas, Model Context Protocol (MCP) servers that provide standardized tool interfaces, and sub-agents that act as specialized tools with their own instructions and guardrails. When an agent decides to call a tool, the runtime validates the request against the tool schema, executes the function in the sandbox, and returns the result. Handoffs work similarly but transfer full control rather than returning a result. A customer support agent might hand off to a billing specialist agent when it detects a payment-related query, carrying the conversation context forward seamlessly.
Choosing the Right Runtime for OpenAI Agents
Selecting the right runtime for your OpenAI Agents workflow depends on your control requirements, infrastructure preferences, and deployment constraints. OpenAI offers three primary runtime surfaces, each with distinct tradeoffs between managed convenience and self-hosted flexibility. Understanding these options early prevents costly architecture changes later.
Agents API vs Agents SDK vs Responses API
The Agents API is a fully managed runtime where OpenAI handles execution, sandboxing, and state management. You define agents, tools, and guardrails declaratively, and the platform runs the agent loop on your behalf. This is the fastest path to production for teams that want to avoid infrastructure overhead. The Agents SDK is a self-hosted library that gives you programmatic control over the agent loop, tool execution, and session handling. You run it in your own environment, which means you manage scaling, security, and persistence yourself but gain full control over customization. The Responses API is the lowest-level surface, providing direct access to model responses with tool-calling capabilities but without the orchestration layer. Use it when you need fine-grained control over every model call and want to build your own agent loop from scratch.
When to Use the Managed Codex Harness
The managed Codex harness shines in scenarios where sandboxed code execution is a core requirement. If your agent needs to run user-submitted code, execute data transformations, or interact with file systems safely, the harness provides an isolated environment that prevents security breaches. It is also ideal for rapid prototyping, where the overhead of setting up your own execution environment would slow down iteration. Compliance-driven teams benefit from the harness because OpenAI manages the security boundary, reducing the audit surface for your application. For production workloads that require custom networking, proprietary tool integrations, or specific data residency requirements, the self-hosted Agents SDK is the better choice.
Building a Reliable OpenAI Agents Workflow
Building a production-grade OpenAI Agents workflow requires careful attention to instruction design, tool exposure, and task decomposition. The goal is to create agents that are capable but bounded, autonomous but observable, and efficient without sacrificing correctness.
Designing Effective Instructions and Guardrails
Agent instructions should be specific, structured, and outcome-oriented. Rather than telling an agent to "help the user," describe the exact steps it should follow, the tools it should prefer, and the conditions under which it should hand off. Guardrails are equally important. They are validation checks that run before or after agent actions to prevent harmful or incorrect behavior. Input guardrails can filter prohibited content before it reaches the model. Output guardrails can verify that responses meet formatting requirements or safety standards before they reach the user. In practice, teams that skip guardrails often see agents drift into unexpected behaviors during long sessions, especially when tool outputs introduce ambiguous context.
Implementing Tool Calls and MCP Integration
Tools should be narrowly scoped and well-documented. Each tool should do one thing clearly, with a schema that leaves no ambiguity about parameters and return types. When integrating external services through the Model Context Protocol, expose only the operations your agent needs rather than entire API surfaces. This reduces the chance of the model selecting the wrong tool or passing incorrect parameters. For developers connecting agents to real-time communication systems, VideoSDK's telephony integration can be exposed as a tool that lets agents initiate or receive phone calls, transfer calls, and handle DTMF events, extending agent capabilities into the voice channel.
Managing Long-Running Tasks and Sub-Agents
Large tasks should be decomposed into subtasks handled by specialized sub-agents. A data analysis agent might spawn a query agent to retrieve data, a transformation agent to clean it, and a reporting agent to generate summaries. Each sub-agent operates with its own instructions, tools, and guardrails, and the parent agent coordinates the handoffs. This approach improves reliability because each agent has a narrow focus, and it improves observability because you can trace failures to specific sub-agents. For complex multi-agent orchestration with deterministic flow control, VideoSDK's Conversational Graph provides a graph-based orchestration layer that complements OpenAI's agent loop by enforcing step ordering and business rules.
Production Best Practices for OpenAI Agents
Moving OpenAI Agents from prototype to production introduces challenges around cost, security, and observability that do not appear during local development. A disciplined approach to these areas separates reliable deployments from fragile ones.
Scaling and Cost Optimization
Token budgeting is the single most effective cost control for OpenAI Agents. Set maximum token limits per session and per tool call to prevent runaway loops where an agent repeatedly calls tools without converging on a response. Session reuse reduces costs by avoiding redundant context processing. Instead of starting a new session for every user interaction, chain interactions using previousResponseId or conversationId to leverage cached context. Concurrency limits prevent cost spikes when multiple agents run simultaneously. Set a maximum number of concurrent agent loops per account or per user to avoid unexpected billing during traffic spikes. Always verify current pricing on OpenAI's official pricing page before estimating production costs.
Security and Compliance Considerations
Agent security starts with sandbox isolation. The managed Codex harness provides this by default, but self-hosted deployments need containerized execution environments with restricted network access and filesystem permissions. Data handling policies should specify what user data agents can access, how long it is retained, and whether it is used for model training. For applications handling sensitive information, end-to-end encryption of agent communications is essential. Tool schemas should include authentication requirements so agents cannot call privileged operations without proper credentials. For voice agents handling phone interactions, VideoSDK provides secure transport layers and SIP integration with IP whitelisting and geo-fencing to protect telephony endpoints.
Monitoring, Tracing, and Debugging
OpenAI Agents include built-in tracing capabilities that log every step of the agent loop, including model calls, tool executions, handoffs, and guardrail evaluations. Enable tracing from the start, even in development, so you have a baseline to compare against when issues arise in production. Key metrics to monitor include loop iteration count (agents that loop excessively may have poorly designed instructions), tool call success rate (frequent failures indicate schema mismatches or service outages), and token usage per session (unexpected spikes may indicate context bloat). For voice agents, VideoSDK's pipeline observability tools provide additional telemetry on audio quality, latency, and turn detection accuracy, giving you a complete picture of agent performance across both reasoning and communication layers.
Real-World Use Cases of OpenAI Agents
Customer Support Automation
A SaaS company deploys an OpenAI Agent as the first responder for customer support tickets. The agent receives a ticket, classifies it by category, and calls a tool to search the knowledge base for relevant articles. If it finds a matching solution, it drafts a response and sends it through the ticketing system. For billing issues, it hands off to a specialized billing agent that can query payment records and initiate refunds within guardrail-defined limits. For complex technical issues, it escalates to a human agent with a summary of the conversation and suggested troubleshooting steps. This workflow reduces first-response time from hours to seconds while maintaining a human safety net for edge cases.
Data Analysis and Reporting
A financial services firm uses OpenAI Agents to automate weekly portfolio reports. A coordinator agent receives the report request and spawns a data retrieval agent that queries the portfolio database through an MCP-connected tool. A transformation agent cleans and aggregates the data, applying business rules encoded as guardrails. A visualization agent generates charts and tables, and a narrative agent writes the executive summary. The coordinator assembles the components into a final report and delivers it via email. What previously required a team of analysts two days now completes in under an hour, with human review focused on exceptions flagged by the agents' guardrails.
Common Pitfalls When Using OpenAI Agents
Several recurring mistakes undermine OpenAI Agents deployments. Over-reliance on tool calls is the most common. Developers expose too many tools or tools that are too broadly scoped, causing the model to call tools when it should reason directly. The fix is to expose only narrowly scoped tools and to include instructions that specify when direct reasoning is preferred. State duplication occurs when developers manually maintain conversation history while also using session-based persistence, leading to inflated token usage and inconsistent context. Choose one persistence strategy and stick with it. Inadequate guardrails allow agents to drift into unsafe or incorrect behaviors during long sessions. Implement both input and output guardrails from day one. Finally, ignoring tracing in development makes production debugging nearly impossible. Enable tracing early and review logs regularly to catch subtle issues before they reach users.
Definitions Glossary
Agent: An autonomous AI entity that receives instructions, reasons about tasks, calls tools, and produces responses through a continuous loop until a task is complete.
Agent Loop: The cycle of reasoning, tool execution, and handoffs that an agent repeats until it generates a final response or terminates the session.
Handoff: The transfer of control from one agent to another, carrying conversation context and relevant state to a specialized sub-agent.
Guardrails: Validation checks that run before or after agent actions to enforce safety, correctness, and behavioral boundaries.
MCP Integration: The Model Context Protocol, a standardized interface that connects agents to external tools, data sources, and services through a consistent schema.
Sandbox Environment: An isolated execution environment where agents can run code and call tools without risking the host system or surrounding infrastructure.
Session Management: The persistence strategy that retains conversation state across turns, enabling agents to maintain context without reprocessing entire histories.
Key Takeaways
- OpenAI Agents combine language models with tools, memory, and guardrails to complete multi-step tasks autonomously through a continuous reasoning loop.
- The three runtime options (Agents API, Agents SDK, Responses API) offer different tradeoffs between managed convenience and self-hosted control.
- Session and state management strategies directly impact both cost and performance, with previousResponseId being the most token-efficient for sequential interactions.
- Production deployments require disciplined attention to token budgeting, sandbox isolation, guardrails, and tracing from day one.
- VideoSDK extends OpenAI Agents into real-time voice and telephony scenarios through its AI Voice Agent SDK and SIP integration capabilities.
Conclusion
OpenAI Agents represent a shift from single-turn model calls to orchestrated, multi-step AI workflows that can reason, act, and hand off autonomously. By understanding the agent loop, choosing the right runtime, and implementing production best practices for cost, security, and observability, developers can build AI systems that handle real business tasks reliably. The architecture is powerful on its own, but when combined with real-time communication platforms like VideoSDK, agents gain the ability to speak, listen, and interact with users over live audio and phone channels. Start with the OpenAI Agents documentation to build your first workflow, and explore VideoSDK's AI Voice Agent guide to extend your agents into real-time voice experiences. What are you building with OpenAI Agents? Drop a comment below, and check out the VideoSDK Discord community to connect with other developers working on agent-powered applications.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ